 VED
 by ITSECOPS
CMMC Phase 2 is paused. The work is not.
On 13 July 2026 the Department of War suspended the CMMC Phase 2 transition and opened a 60-day review; the reform task force report is due late September or early October. Nothing in that pause touches DFARS 252.204-7012, the 7019 and 7020 clauses, your SPRS score, the annual affirmation or False Claims Act exposure for a score you cannot evidence. Read the ITSECOPS analysis: CMMC Phase 2 suspended, what still applies.
Phase 2 suspended, review under way
Level 2 certification roll-out paused; NIST SP 800-171 Rev 2 self-assessment, SPRS and 7012 obligations continue unchanged.
Primes keep enforcing
Elbit America told suppliers to confirm requirements with their buyer before cancelling a C3PAO assessment; L3Harris kept its Level 2 deadline. Flow-down did not pause.
Why CMMC programmes end up in Excel: the FedRAMP trap
DFARS 252.204-7012 requires that any cloud service used to store, process or transmit CUI meets security requirements equivalent to the FedRAMP Moderate baseline. A GRC platform does not look like a CUI system on day one. Then someone uploads the network diagram, the SSP with system boundaries, a screenshot of the enclave configuration, a marked document as evidence for control 3.1.3. From that moment the GRC tool holds CUI, and the assessor will ask where it is hosted.
The SaaS vendors know this. The answer is a GovCloud or "FedRAMP Moderate equivalent" edition, priced for primes, sold per user and per framework, with a 5 to 10% uplift at renewal. For a 40 to 400 person defense supplier that is a second CMMC budget just for the tracking tool. So the compliance lead does the rational thing and opens a spreadsheet.
The rule of thumb: if your SSP, POA&M, diagrams or evidence can contain CUI, the platform holding them must sit inside a boundary that already meets FedRAMP Moderate or equivalent. Your Microsoft 365 GCC or GCC High tenant already does. A SaaS GRC tool's commercial cloud does not.
What the spreadsheet method actually costs
Excel is free until you count the hours. NIST SP 800-171 has 110 controls and, under 800-171A, 320 assessment objectives, every one of which needs an implementation statement, an owner, evidence and a date. Then the duties repeat: weekly log reviews, monthly access recertifications, quarterly vulnerability scans, annual policy approvals and training. A spreadsheet has no clock, no reminder and no memory.
| Where it breaks | What happens in Excel | What it costs you |
|---|---|---|
| Recurring duties | Weekly, monthly and quarterly tasks live in someone's head or a calendar that nobody else sees | Missed reviews surface at the assessment as failed objectives |
| Evidence | Files in mailboxes, Teams chats and personal OneDrives, renamed "final_v3" | Days of re-collection before every assessment; no freshness, no version history |
| Multiple sites or enclaves | One workbook per site, then a "master" that is always behind | Nobody can answer "are we compliant today" without a week of reconciliation |
| SPRS score | Recalculated by hand from a column of 1, 3 and 5 point weights | Arithmetic errors in a score you affirm under the False Claims Act |
| POA&M | Separate sheet, no link to the control, no 180-day conditional clock | Items age out silently; conditional status expires unnoticed |
| Dashboard | None. A pivot table if you are lucky | Leadership and the prime get a PDF that was true last quarter |
| Staff change | The workbook leaves with the person who built it | Programme restarts from scratch; months redone |
ITSECOPS has walked into this workbook at dozens of defense suppliers. The pattern is always the same: eighteen months of effort, a score nobody can defend, and a sinking feeling before the C3PAO arrives. The tool is not the compliance programme, but the wrong tool is why the programme stalls.
VEDVERA for CMMC: what changes on day one
VEDVERA is a signed SharePoint Framework package deployed into your own tenant's App Catalog. It creates the lists and libraries a CMMC programme needs and runs in the browser against your SharePoint, in the signed-in user's context. There is no VEDVERA cloud, no vendor database and no new external service provider to describe in your SSP. If your tenant is inside your assessed CUI boundary, so is VEDVERA.
- Level 1 and Level 2 control libraries with all 110 NIST SP 800-171 controls and the 320 800-171A assessment objectives, each with implementation statement, owner, status and linked evidence.
- Official SPRS scoring calculated from objective status using the DoD weights, so the number you affirm is the number the portal shows.
- POA&M tied to the control, with due dates, owners and the conditional-status clock in view, not in a separate sheet.
- Compliance calendar with 45 recurring duties out of the box, owner reminders and a live "who is late" view; the weekly, monthly and quarterly work stops depending on memory.
- Evidence library with versioning, freshness clock, retention labels and 55 evidence recipes telling each owner exactly what to export from Entra, Intune, Defender or the firewall.
- Policy and procedure library generated from your scoping answers and inventory, approval workflow, branded PDF output, consistency check against the SSP.
- Multi-site and enclave aware: departments, sites and enclaves are structure in the portal, not separate workbooks; the dashboard rolls up and drills down.
- Assessor role: read-only, evidence-centric view for your C3PAO or prime, with an append-only audit trail of who changed what and when.
- Spreadsheet import during deployment, so the eighteen months you already spent are not thrown away.
Inside the tool
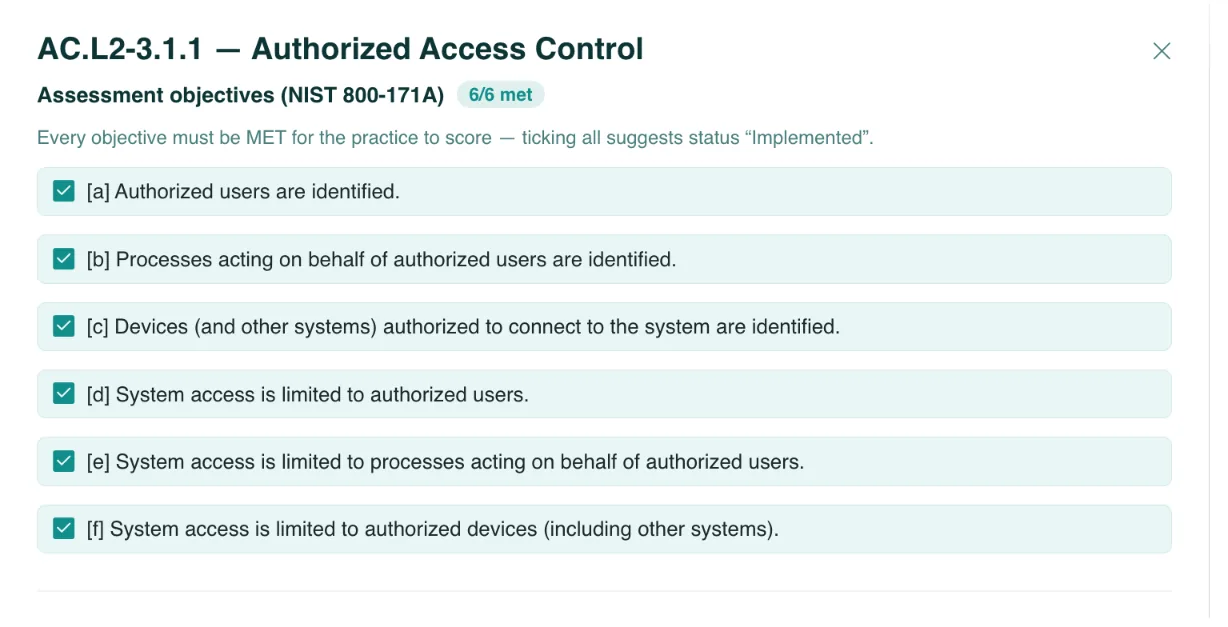
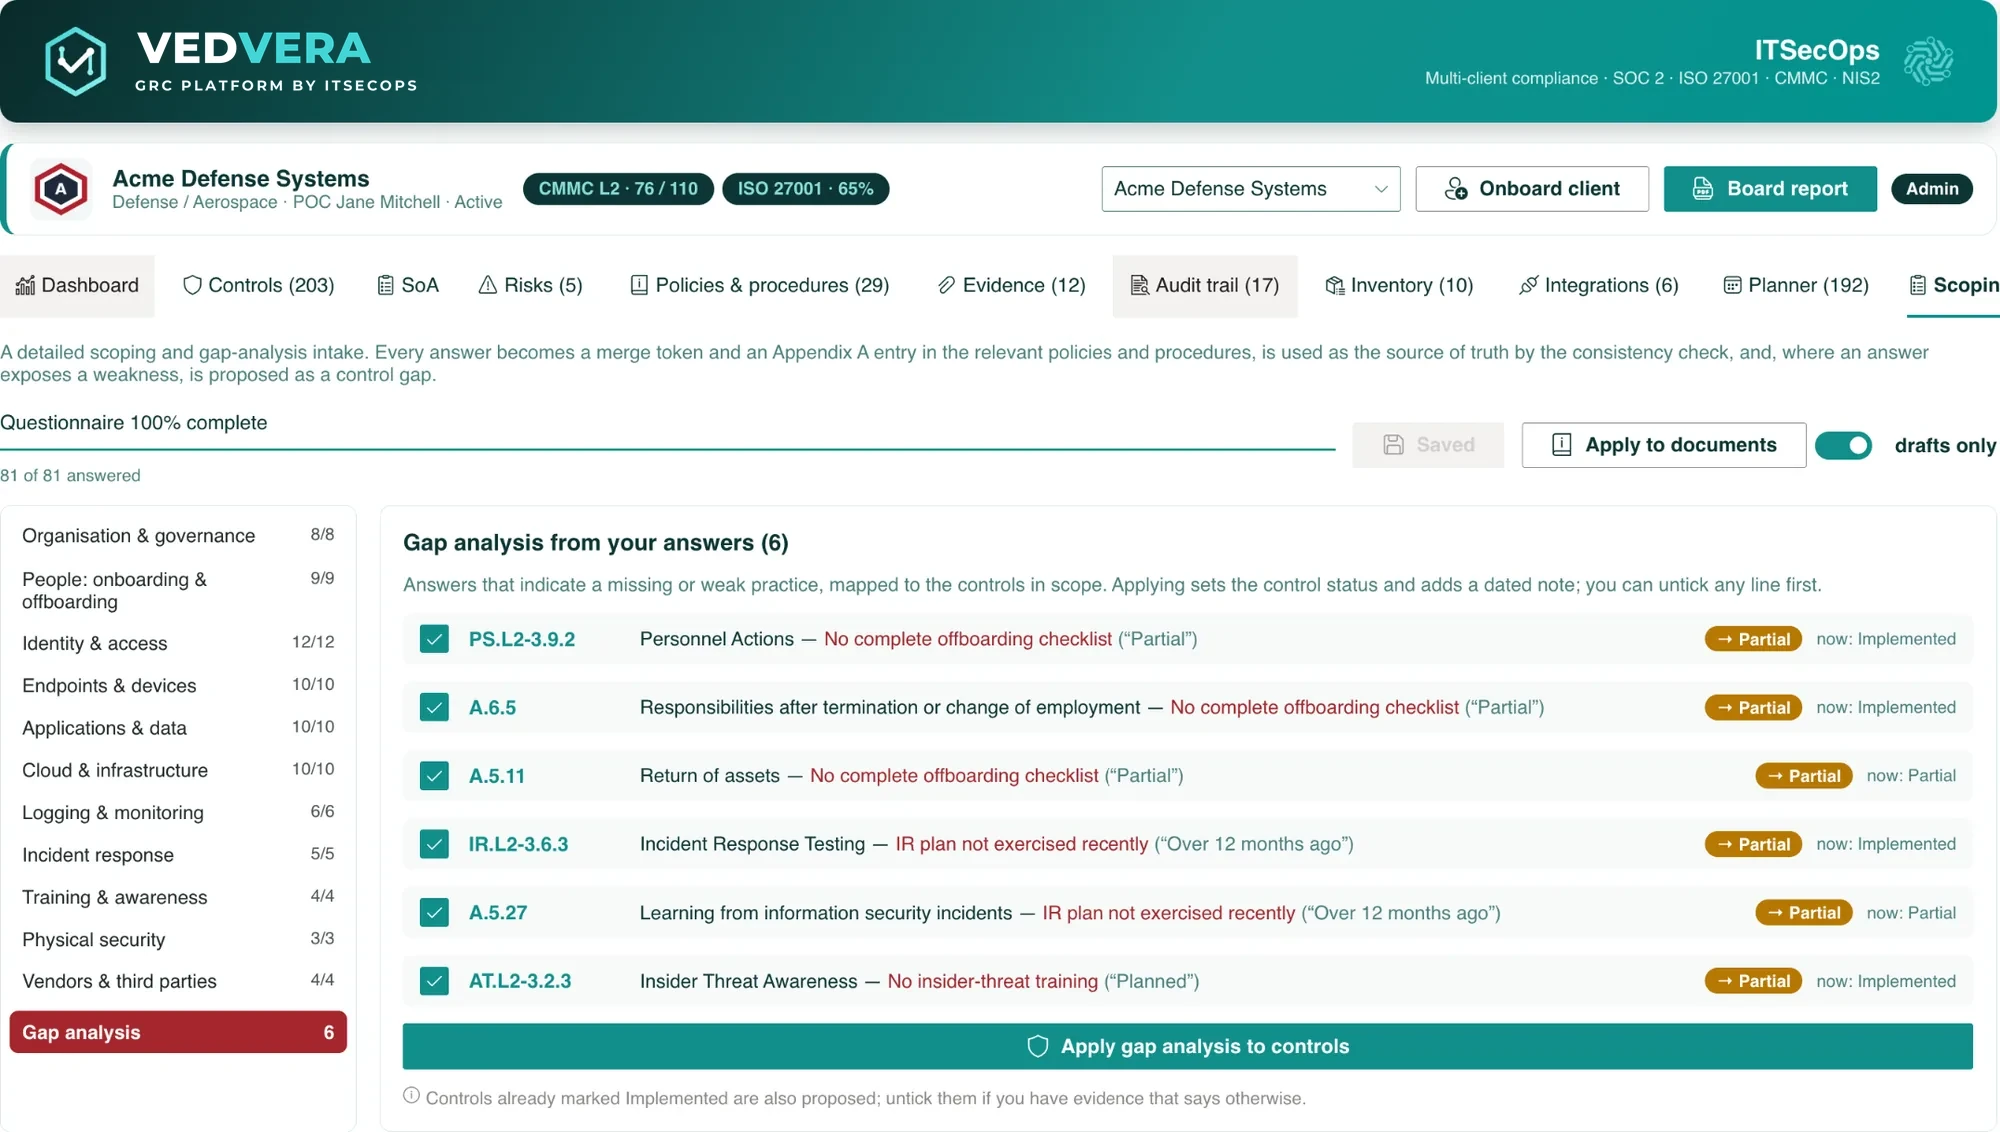
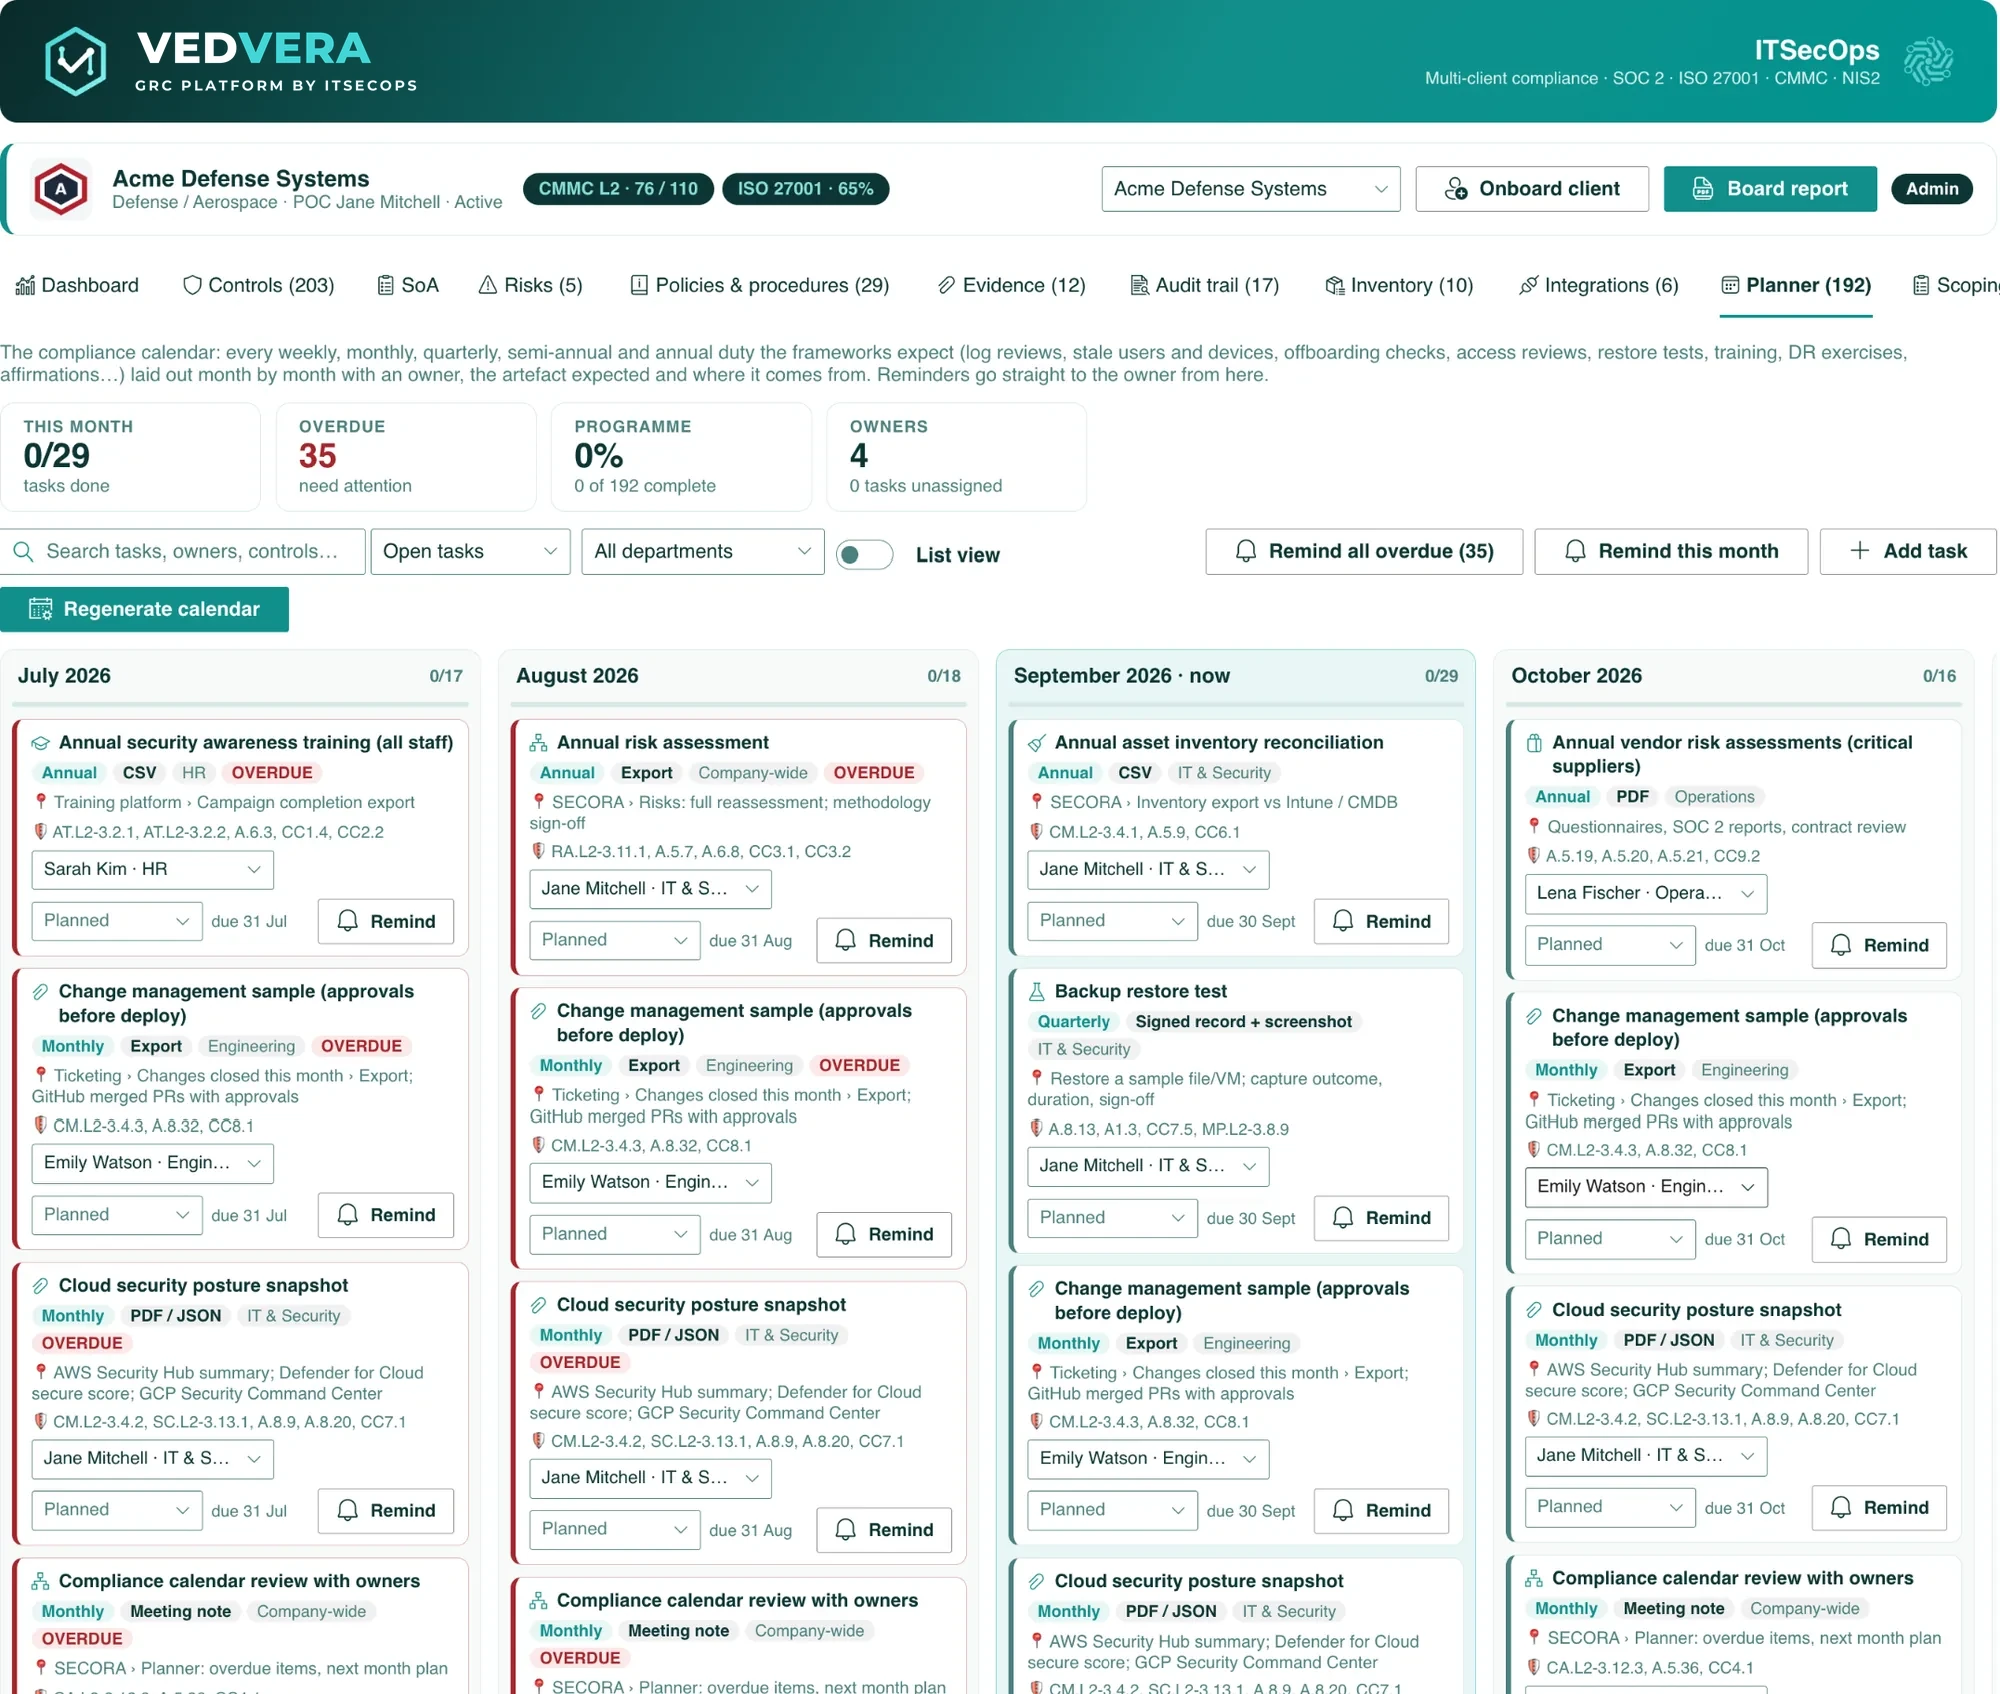
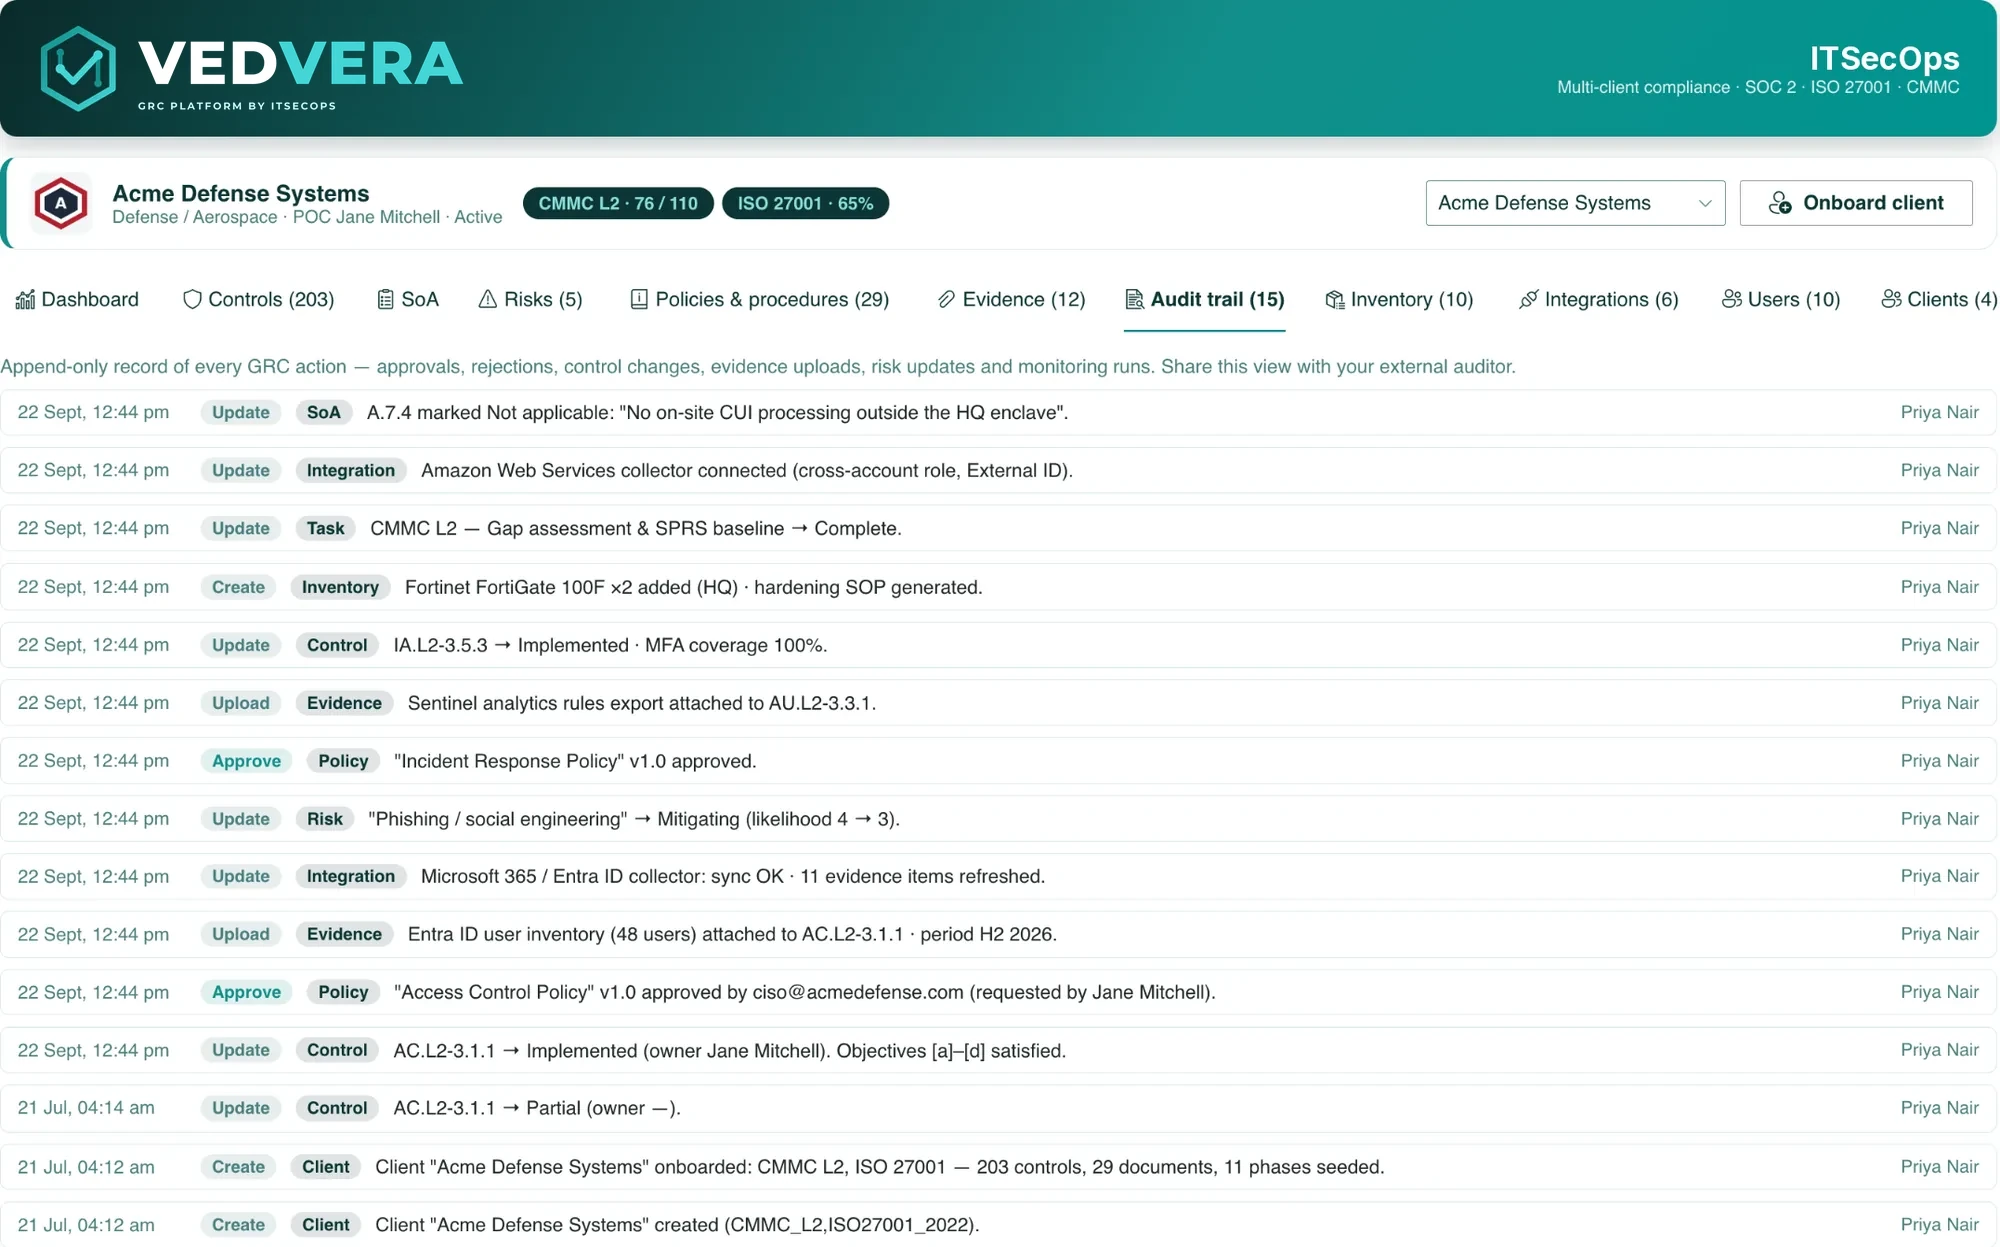
Screens show the VEDVERA demo workspace (Acme Defense Systems, a fictional client).
Excel vs SaaS GRC vs VEDVERA for CMMC
| Question the assessor asks | Excel and SharePoint lists (DIY) | Commercial SaaS GRC | SaaS GRC, FedRAMP or GovCloud edition | VEDVERA by ITSECOPS |
|---|---|---|---|---|
| Where do the SSP, POA&M and evidence live? | Your tenant, scattered | Vendor's commercial cloud | Vendor's government cloud | Your Microsoft 365, GCC or GCC High tenant |
| Does the tool need its own FedRAMP answer? | No | Yes, and usually cannot give one | Yes, provided at a premium | No. It inherits your tenant's boundary |
| New external service provider in scope? | No | Yes | Yes | No. ITSECOPS holds no data |
| Licence model | Free, paid in hours | Per user, per framework, annual uplift | Per user at government pricing | One-time deployment per organisation |
| Hosting cost | Included in Microsoft 365 | In the subscription | In the subscription | $0. SharePoint is already in your licence |
| Recurring duties, reminders, freshness | None | Yes | Yes | Yes, 45 duties seeded |
| Multi-site, multi-enclave dashboard | None | Yes | Yes | Yes |
| SPRS score | By hand | Varies | Varies | Official weights, live |
| Identity, MFA, Conditional Access | Entra ID | Vendor login plus SSO add-on | Vendor login plus SSO | Entra ID, already enforced |
| Exit | Keep the files | Export, lose history | Export, lose history | Nothing to export; the lists are yours |
$0 hosting, zero new vendors, your security policy already applied
SharePoint Online is part of every Microsoft 365 Business and Enterprise plan, including GCC and GCC High. VEDVERA runs there. There is no server to rent, no database to patch, no SaaS subscription and no hosting line on the invoice: the platform costs nothing to host because you already host it.
Because every VEDVERA record is a SharePoint record, your existing controls apply to it automatically: Entra ID single sign-on, MFA, Conditional Access and device compliance, role-based access through SharePoint groups (Compliance admins, Control owners, Auditors), PIM for admins, Purview audit, retention labels, DLP and eDiscovery. You do not write a vendor risk assessment for VEDVERA, because VEDVERA is not a vendor in your data flow.
Outside Microsoft 365? VEDVERA is also available as a standalone web application installed on your own Linux server behind your own identity provider, and on SharePoint Server on-premises. Same product, same one-time licence; the deployment is scoped during discovery.
For RPOs, MSPs and CMMC consultancies
If you run CMMC readiness for many defense suppliers, the multi-client edition partitions every record by client key. Each client's programme is a separate workspace inside your tenant, or deployed into the client's own tenant when their boundary requires it. The client switcher re-scopes every tab; optional guest access lets the client's point of contact see only their workspace. No per-client SaaS seat, ever. Details on VEDVERA for MSPs and consultancies.
What VEDVERA costs for a CMMC programme
One-time deployment fee per organisation, covering installation in your tenant, CMMC Level 1 or Level 2 configuration with the 800-171A objectives, policy library seeding, dashboard set-up, optional spreadsheet migration and hand-over. Twelve months of maintenance, updates and support by ITSECOPS are included; renewal from year two is optional. There are no per-user, per-month or per-framework charges, so adding ISO 27001 or NIST CSF later reuses the shared controls at no licence cost. Compare against per-seat SaaS with the 3-year GRC cost calculator, or ask for an exact quote for your scope.
If your CUI boundary is a Microsoft tenant, the GRC tool should be in it too.
That is the whole argument. Everything else on this page is detail.
Sources: DFARS 252.204-7012(b)(2)(ii)(D) on FedRAMP Moderate equivalence for cloud services handling CUI; DoD CIO memo on FedRAMP Moderate equivalency (December 2023); Department of War CMMC Phase 2 suspension notice, 13 July 2026, and industry reporting on prime contractor flow-down (July to September 2026); NIST SP 800-171A assessment objectives. VEDVERA does not certify you; a C3PAO or your self-assessment does. VEDVERA keeps the evidence that makes either defensible.
Frequently asked
Not the tool itself, but the place where CUI is stored, processed or transmitted must meet security requirements equivalent to the FedRAMP Moderate baseline under DFARS 252.204-7012. A GRC platform holding your SSP, network diagrams, POA&M or marked evidence is holding CUI-adjacent material, which is why SaaS vendors sell GovCloud or FedRAMP equivalent editions at a premium. VEDVERA avoids the question by running inside your own Microsoft 365, GCC or GCC High tenant, which is already the boundary you assess.
VEDVERA deploys to Microsoft 365 commercial and GCC tenants as a signed SharePoint Framework package. GCC High and other sovereign or on-premises environments are scoped during discovery, and SharePoint Server on-premises is supported where the SharePoint Framework is supported. Book a walkthrough and tell us your tenant type.
No. VEDVERA has no cloud of its own; every record is a SharePoint list item or library file in your tenant. ITSECOPS deploys and maintains the package but holds no data at rest. Support access is granted by you, scoped and revocable, and logged in the append-only audit trail.
Yes. Spreadsheet migration is an optional step in deployment. ITSECOPS maps your control statements, statuses, owners and POA&M items into the VEDVERA lists so the work you already did carries over.
Yes. The score is calculated from the status of each NIST SP 800-171 requirement using the official DoD weighting (1, 3 and 5 point deductions), so the number you submit to SPRS and affirm annually is the number the portal shows, with the evidence behind it.
The suspension announced on 13 July 2026 paused the certification roll-out, not the obligations. DFARS 252.204-7012, the 7019 and 7020 clauses, NIST SP 800-171 self-assessment, SPRS submission and the annual affirmation all continue, and primes such as Elbit America and L3Harris kept their own flow-down deadlines. The risk in a pause is that spreadsheets rot while nobody is watching; a platform with recurring duties and a freshness clock is what keeps a programme alive.
Nothing. VEDVERA runs on the SharePoint Online that is included in your Microsoft 365 or GCC licence, or on your own SharePoint Server. There is no separate hosting fee, no server to rent and no database to manage. The only charge is the one-time deployment fee, which includes twelve months of ITSECOPS maintenance.
Microsoft 365 is the primary home because it makes hosting free and inherits Entra ID security. For organisations outside Microsoft 365, VEDVERA is available as a standalone web application installed on your own Linux server behind your identity provider. The commercial model is the same.
Yes. The multi-client edition partitions every record by client key with a client switcher and optional guest access per client, and there is no per-client seat charge. Where a client's CUI boundary requires it, VEDVERA can instead be deployed into the client's own tenant.