 SEC
 by ITSECOPS
The GRC software market is worth roughly $21 to 23 billion in 2025 and growing about 11% a year. Sixty to seventy percent of first-time SOC 2 organisations now use a platform, and the all-in first-year cost of a SOC 2 programme sits between $85,000 and $110,000 once audit and remediation are counted. The platform is a meaningful slice of that, and the way it is priced decides what year three looks like.
14 GRC platforms compared
| Platform | Pricing model | Reported annual price (2026) | Where your data lives | AI reads your evidence | Frameworks |
|---|---|---|---|---|---|
| SECORA by ITSECOPS | One-time deployment per organisation + optional maintenance | Quote for your scope; no per-user fees | Your Microsoft 365 tenant or SharePoint Server | No | CMMC, ISO 27001, SOC 2, NIS2, HIPAA, GDPR, NIST CSF, custom |
| Vanta | Per framework + headcount bands + add-ons | Median $20,000; $7,500 to $57,221 | Vanta cloud (AWS, US default) | Yes (AI agents) | SOC 2, ISO 27001, HIPAA, GDPR, many more |
| Drata | Company size + framework count | Median $25,000; $9,494 to $67,350 | Drata cloud (US) | Yes (agentic) | SOC 2, ISO 27001, HIPAA, GDPR, CMMC, many more |
| Secureframe | Employee count + frameworks | Median $20,000; $12,000 to $80,000 plus | Vendor cloud | Yes (Comply AI) | SOC 2, ISO 27001, HIPAA, PCI, many more |
| Sprinto | Scope-based bundle | $8,000 to $30,000 estimated | Vendor cloud (AWS) | Automated evidence | SOC 2, ISO 27001, GDPR, HIPAA, more |
| Hyperproof | Named users + frameworks + tier | Median $41,400; $22,215 to $70,000 | Azure, US and EU; FedRAMP Moderate edition | Yes | 100 plus frameworks |
| AuditBoard | Per named user, per module | Median $45,947; $21,220 to $111,208 | Vendor cloud | Yes | Enterprise audit, risk, compliance |
| OneTrust | Per module, usage-based | Median $12,000; $1,620 to $48,215 | Vendor cloud, multi-region | Yes | Privacy, GRC, AI governance |
| Thoropass | Subscription by framework and size, in-house audit | Median $25,000; $1,145 to $50,880 | Vendor cloud | AI assist | SOC 2, ISO 27001, HIPAA, PCI |
| Scrut Automation | Flat rate, all frameworks bundled | About $15,000 start; $40,000 plus enterprise | Vendor cloud | AI mapping | 60 plus frameworks |
| LogicGate | Per application + power users | Median $53,783; $12,294 to $136,130 | Vendor cloud | Spark AI | Enterprise risk and compliance |
| Scytale | Platform + per framework (about $2,100 each) | From $7,500 | Vendor cloud | Yes | SOC 2, ISO 27001, HIPAA, GDPR, more |
| Apptega | Base platform + team size + frameworks, MSP white-label | About $9,950 start; $20,000 plus for 5 plus users | Vendor cloud | Harmony AI | Many, MSP-oriented |
| Open source (Eramba, CISO Assistant, SimpleRisk, GovReady) | Free or paid enterprise tier; you host and maintain | Hosting and engineering time | Your servers | No | Varies by project |
Sources: Vendr marketplace data (Feb 2026) · SOC2Auditors pricing insights · ComplianceRated: Scrut and Apptega pricing · Compyl: state of GRC 2026 · Agency: SOC 2 statistics 2026. Competitor figures are observed contract data or published estimates, not list prices; verify with the vendor.
How to choose a GRC platform in 2026
1. Decide where the evidence is allowed to live
This is the question most buyers skip and most assessors now ask. Your policies, risk register, vendor list and evidence are a map of your weaknesses. In a vendor-hosted platform they sit in someone else’s cloud, protected by someone else’s controls, and that vendor becomes an entry in your own third-party risk register. In June 2026 the Klue OAuth incident pulled Salesforce data from 195 organisations including a GRC vendor, the third SaaS supply-chain event in a year. A tenant-resident platform removes the question entirely.
2. Model three years, not one
Per-seat and headcount pricing plus 5 to 10% escalators compound. A $20,000 year-one contract with 8% uplift and modest seat growth is about $70,000 over three years before audit fees. A one-time deployment with optional maintenance is a different curve. Use the GRC cost calculator with your real quote.
3. Check how frameworks are added
Adding ISO 27001 to a SOC 2 programme should reveal only the extra controls, because 80% plus of the document workstream is shared. On several platforms it is a tier upgrade. Try the framework overlap tool to see how much work is actually new.
4. Ask what the AI does with your evidence
AI mapping saves time and also means confidential exports are processed by a third party. Boards and assessors increasingly want a yes or no answer to "does an AI service ingest our evidence". Make sure you can give one.
5. Match the platform to your estate
Cloud-native startups on AWS or GCP with hundreds of SaaS tools are well served by Vanta, Drata or Secureframe. Microsoft 365 organisations, defense suppliers with CMMC and SPRS obligations, European entities under NIS2, and MSPs running many clients are better served by a platform that sits inside the tenant and is priced per organisation.
The four categories of GRC tools
Compliance automation SaaS (Vanta, Drata, Secureframe, Sprinto, Scytale, Thoropass, Scrut): fast, integration-heavy, priced per seat or headcount, vendor-hosted, AI-driven. Best for startups chasing a first SOC 2 or ISO 27001.
Enterprise GRC suites (Hyperproof, AuditBoard, LogicGate, OneTrust, ServiceNow IRM, Archer): broad, expensive, module-based, built for internal audit and enterprise risk teams. Often over-scoped for a single-framework SMB.
Open source (Eramba, CISO Assistant, SimpleRisk, GovReady, VerifyWise): full data sovereignty at the cost of hosting, patching and building your own framework content. Attractive to teams with spare engineering time.
Tenant-resident platforms (SECORA by ITSECOPS): deployed inside your Microsoft 365 or SharePoint Server, licensed per organisation, consultant-deployed and maintained. Sovereignty of open source without the self-hosting burden, structure of SaaS without the vendor. Read more about self-hosted and on-premises GRC.
Where SECORA fits
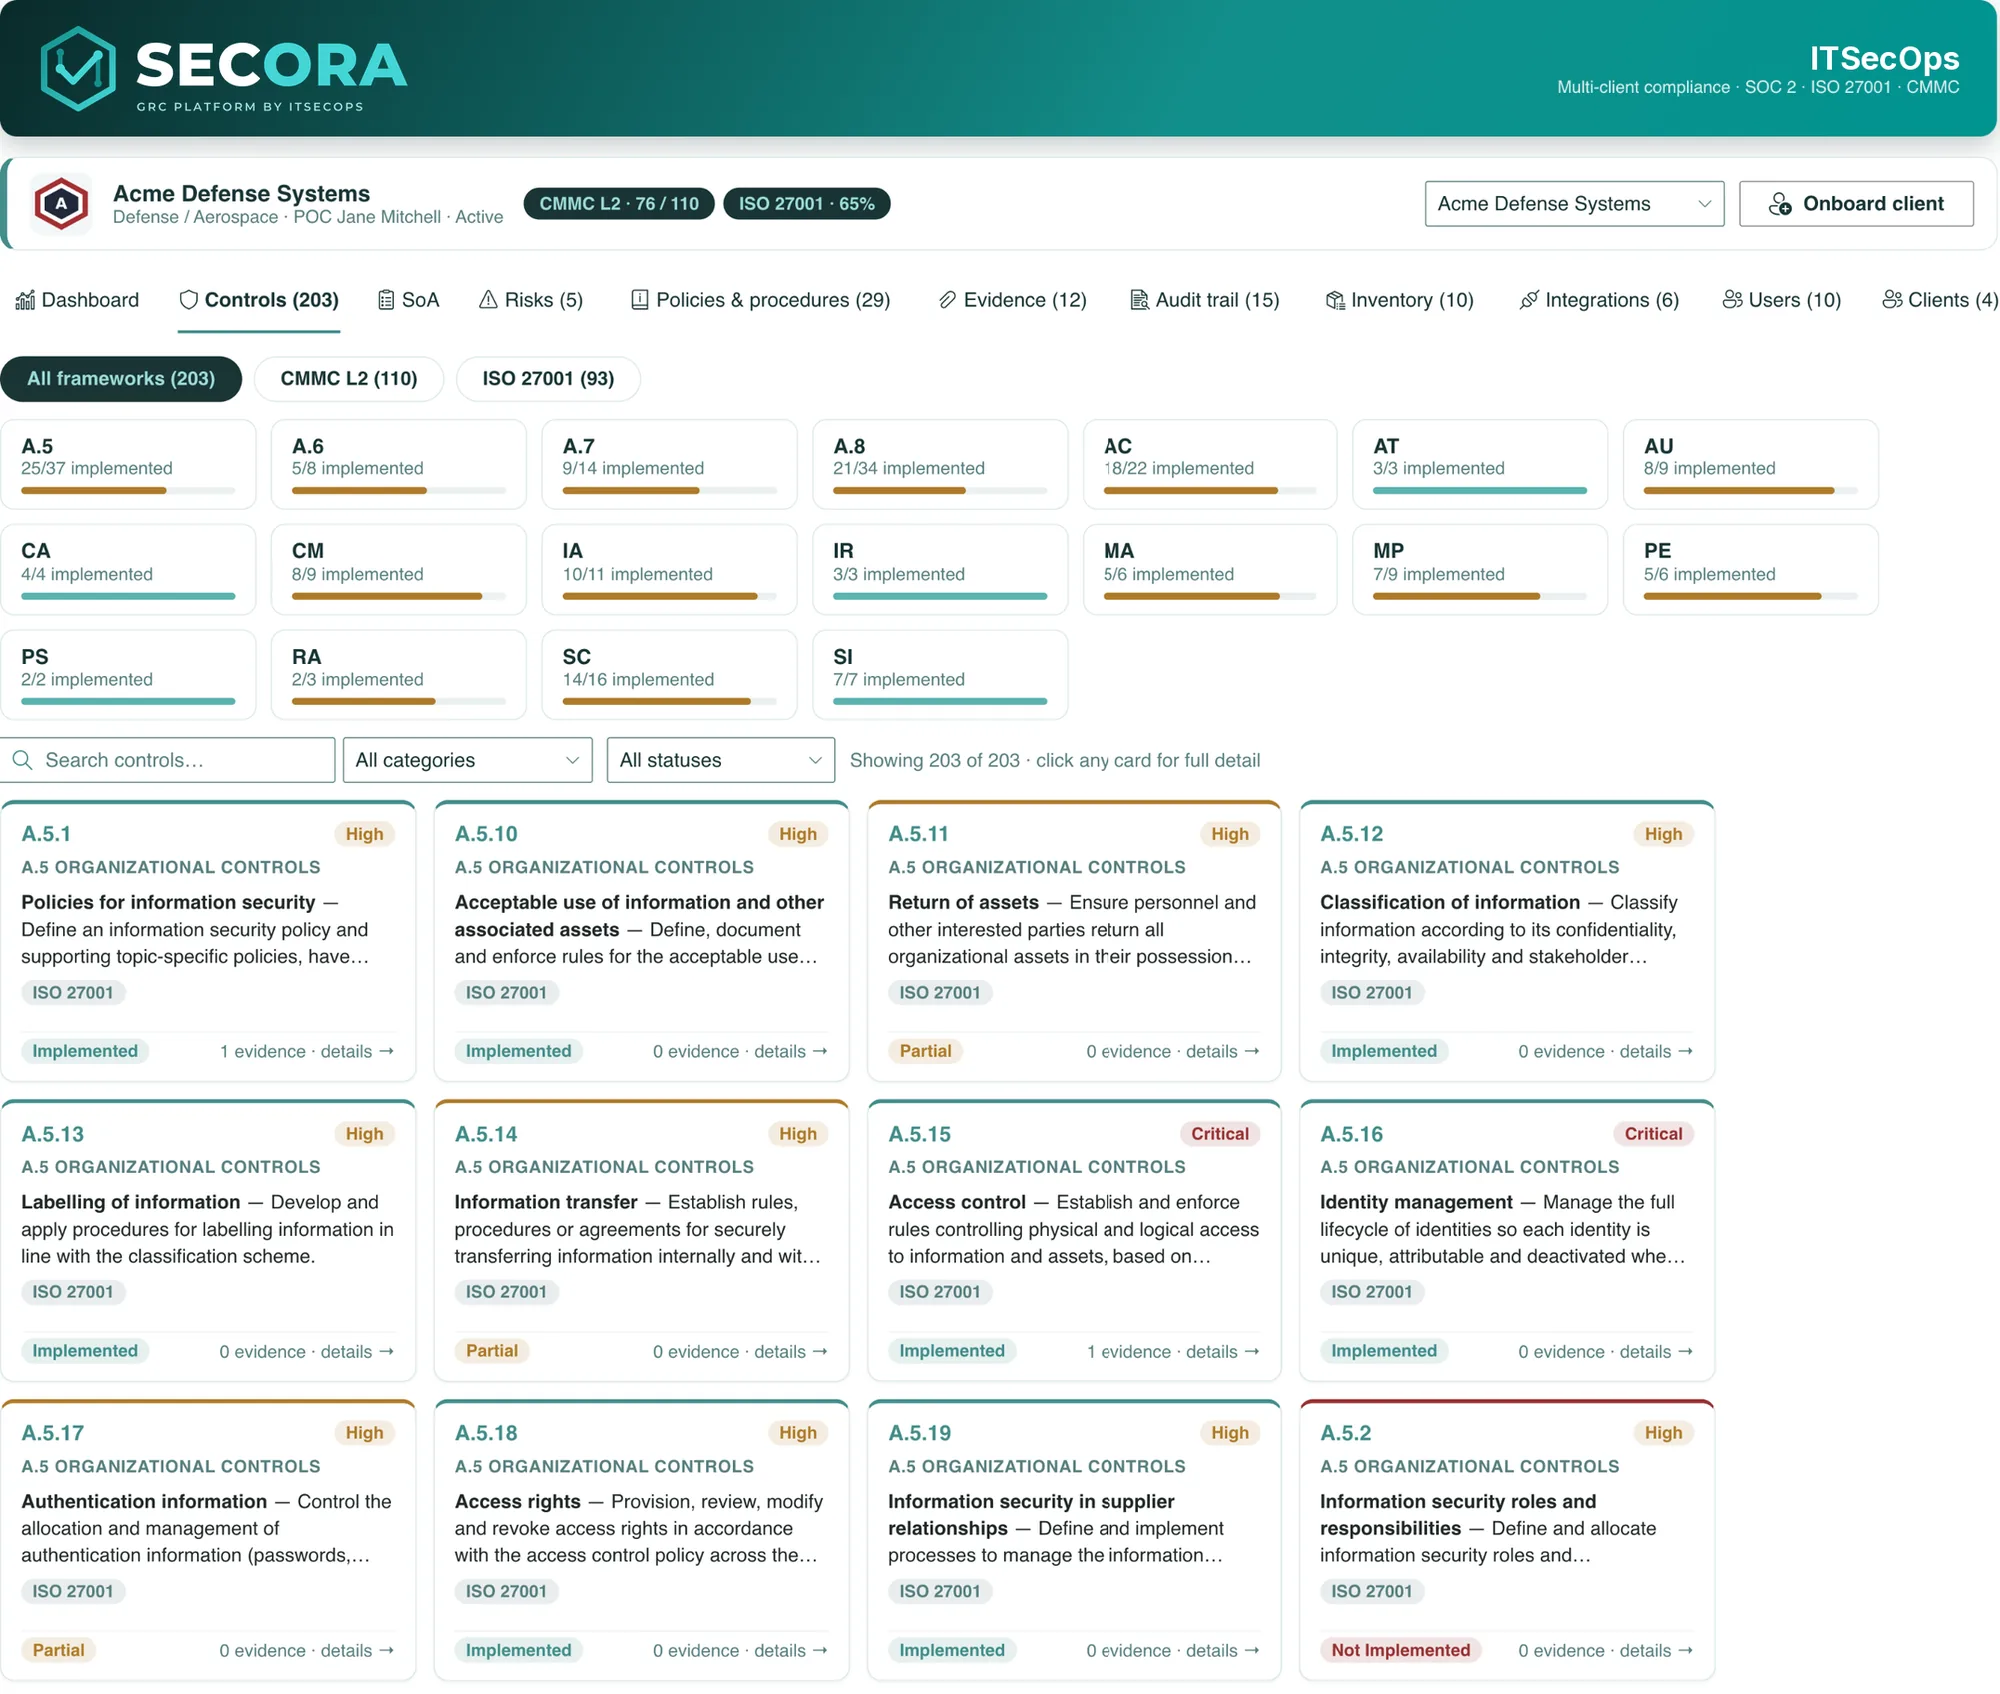
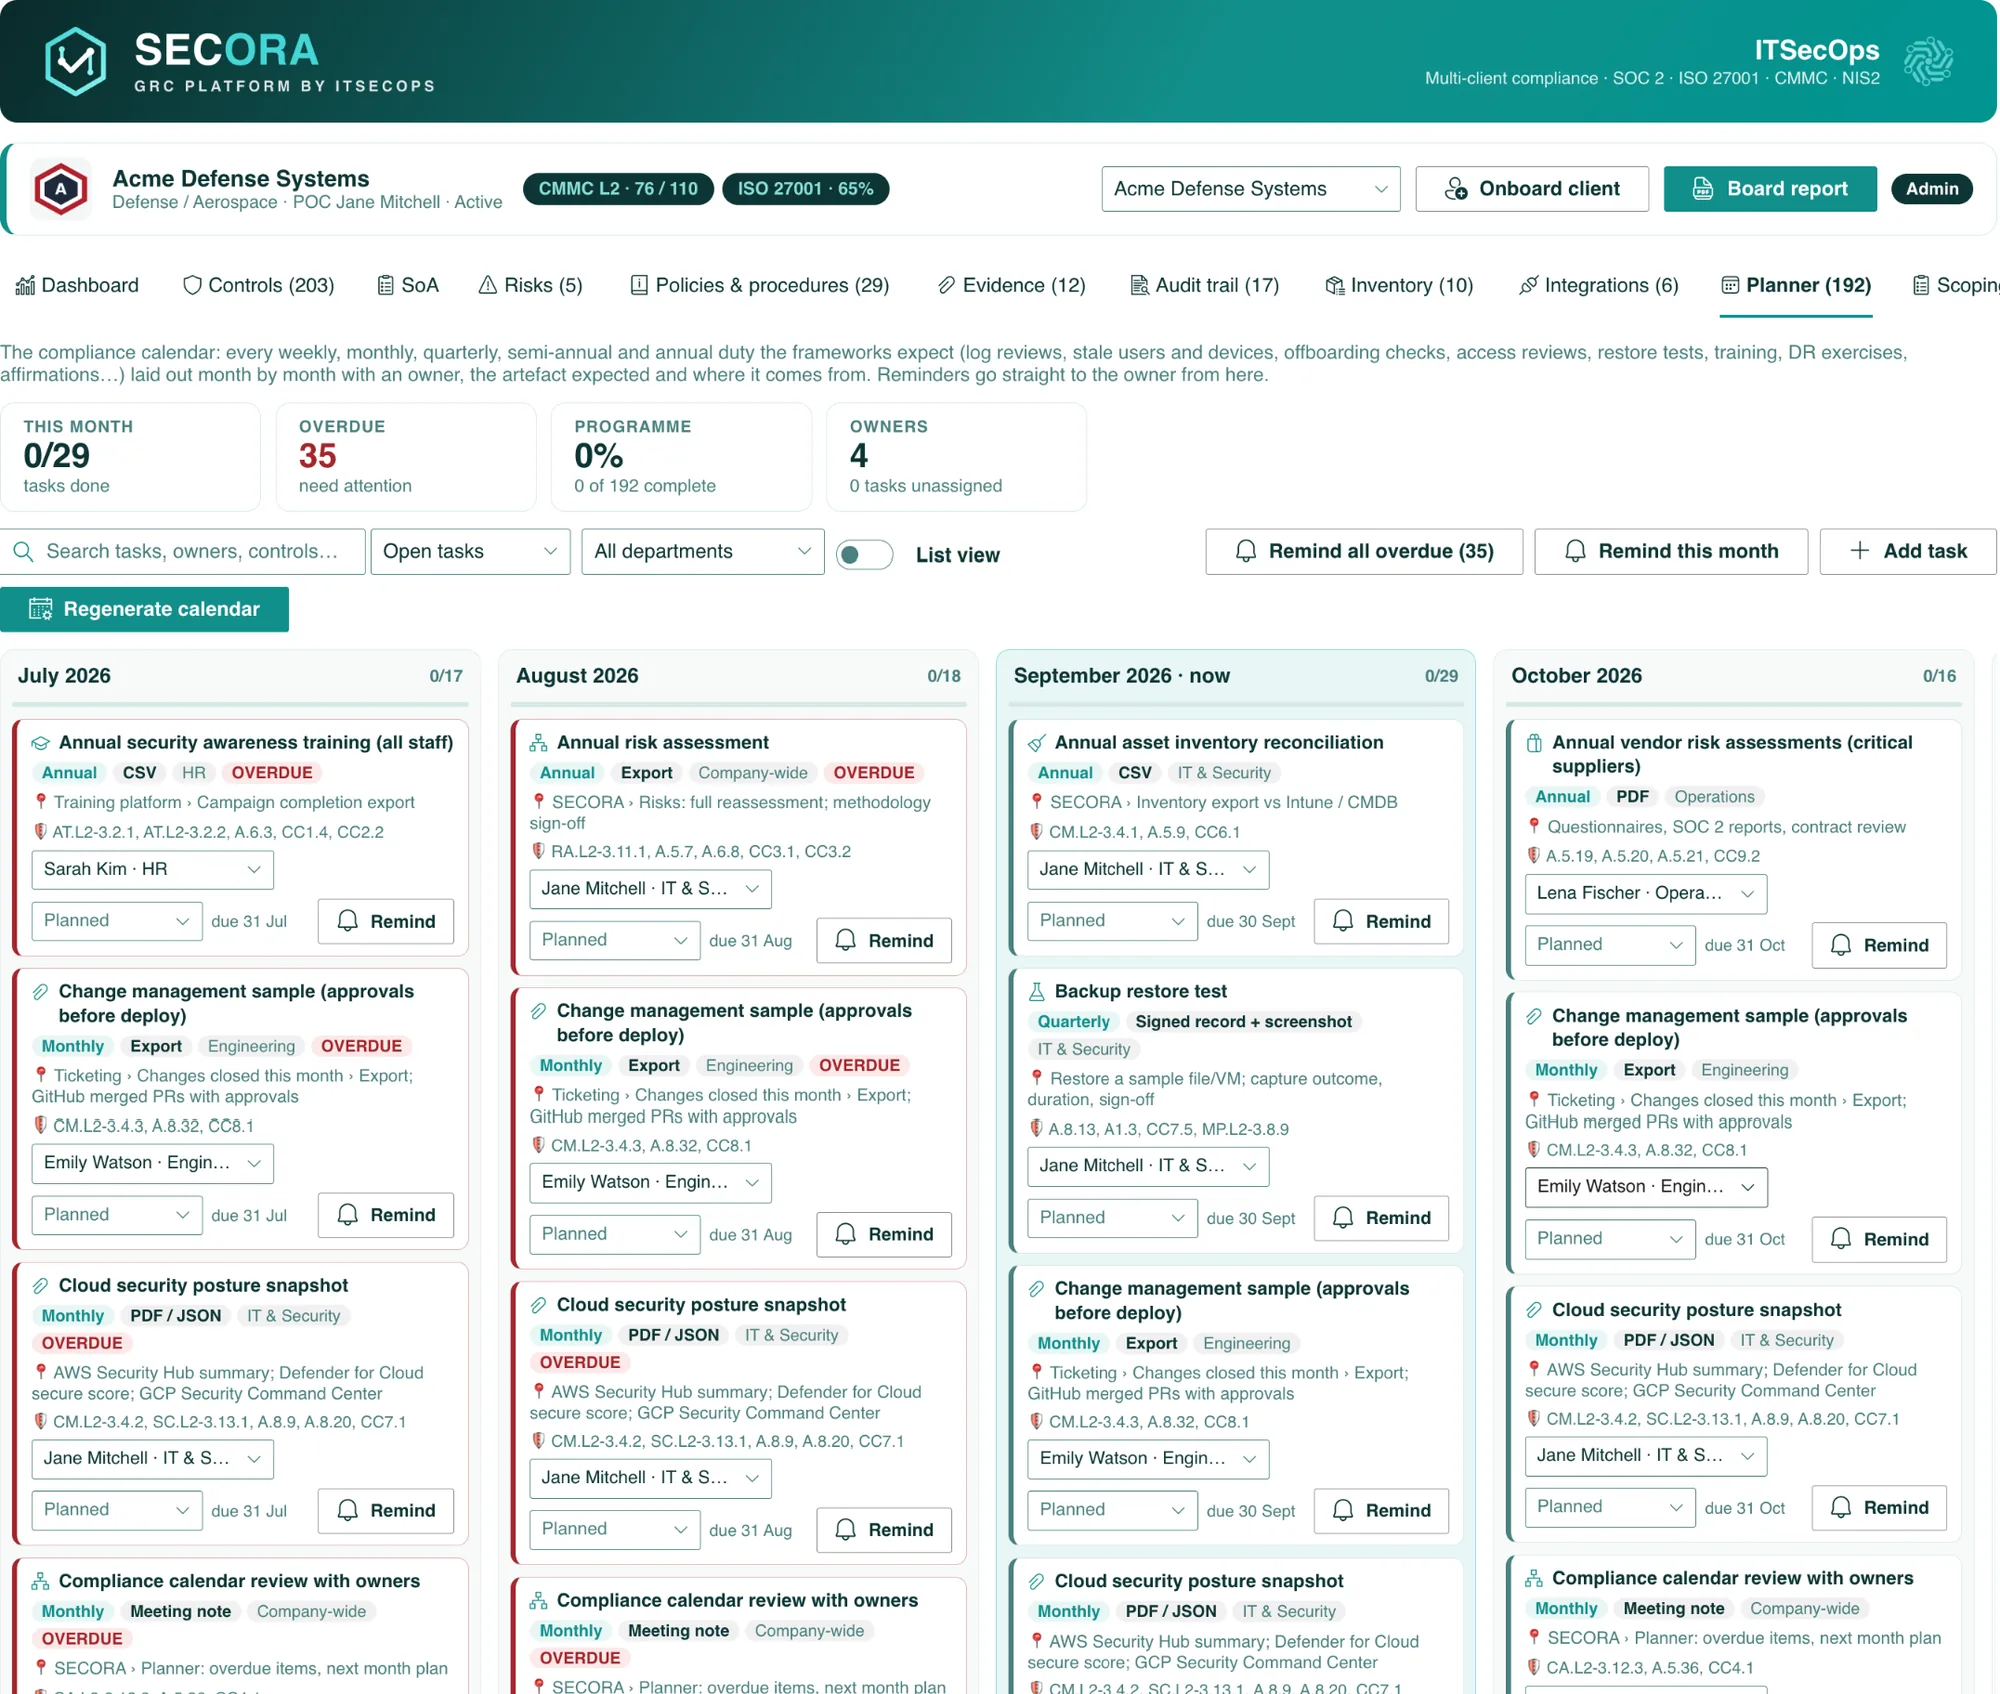
SECORA was built by ITSECOPS, a consultancy that runs CMMC, ISO 27001, SOC 2 and NIS2 programmes, after watching clients pay per seat for tools that became another vendor to assess. It seeds 203 controls for a CMMC Level 2 plus ISO 27001 client, generates 29 client-branded policies from your scoping answers, schedules 45 recurring duties with owners and reminders, and produces a one-click board report, all inside your tenant. See the full product overview, the Vanta, Drata, Secureframe and Sprinto comparisons, or book a walkthrough in your own tenant.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Frequently asked
It depends on your estate. Cloud-native startups on AWS or GCP usually pick Vanta, Drata, Secureframe or Sprinto. Microsoft 365 organisations, defense suppliers with CMMC obligations, NIS2 entities in Europe and MSPs are better served by a tenant-resident platform such as SECORA, licensed once per organisation with no per-user fees.
Observed 2026 contract medians: Vanta $20,000, Drata $25,000, Secureframe $20,000, Hyperproof $41,400, AuditBoard $45,947, OneTrust $12,000, Thoropass $25,000, LogicGate $53,783 a year (Vendr). Sprinto and Scytale start lower, at $7,500 to $10,000. SECORA is a one-time deployment fee per organisation with twelve months of maintenance included; the quote depends on frameworks and estate.
Yes: Eramba, CISO Assistant, SimpleRisk, GovReady and VerifyWise. They give full data sovereignty but you host, patch and build framework content yourself. SECORA offers the same sovereignty inside your Microsoft tenant with the content, deployment and maintenance done by ITSECOPS.
They automate evidence collection, control status and reporting; the audit itself is still performed by an independent assessor or C3PAO. SECORA produces a one-click board report and gives auditors a read-only role with the power to mark evidence verified, so verification replaces reconstruction.
Hyperproof states Azure US and EU hosting; Vanta offers Frankfurt on request at onboarding; Drata had no publicly documented EU option as of September 2026. SECORA stores everything in your own tenant, so residency follows your Microsoft geography automatically.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.