 SEC
 by ITSECOPS
Use the framework overlap tool to model your own combination, or read ISO 27001 vs SOC 2 and NIST 800-171 vs CMMC for the framework-level differences.
CMMC compliance software that keeps CUI evidence inside your own tenant
Consulting and readiness services for this framework: CMMC services by ITSECOPS.
Defense suppliers have two problems a per-seat SaaS GRC tool makes worse: the evidence for 110 practices is itself sensitive, and the assessor scores you with a specific method. SECORA runs inside your Microsoft 365 GCC or commercial tenant, seeds every practice with its 800-171A objectives, scores SPRS the way the DoD does, and schedules the recurring duties an assessor samples.
On 13 July 2026 the Pentagon suspended CMMC Phase 2 (the third-party C3PAO assessments due to hit contracts from November 2026) and opened a 60-day review. Phase 1 self-assessments, SPRS scores, DFARS 252.204-7012 and NIST SP 800-171 remain mandatory for roughly 80,000 companies in the Defense Industrial Base. That is the worst possible moment to sign a multi-year per-seat GRC contract for a deadline that moved, and the best moment to put your SSP, POA&M and evidence somewhere you own. What still applies after the suspension.
What SECORA seeds for CMMC Level 1 and Level 2
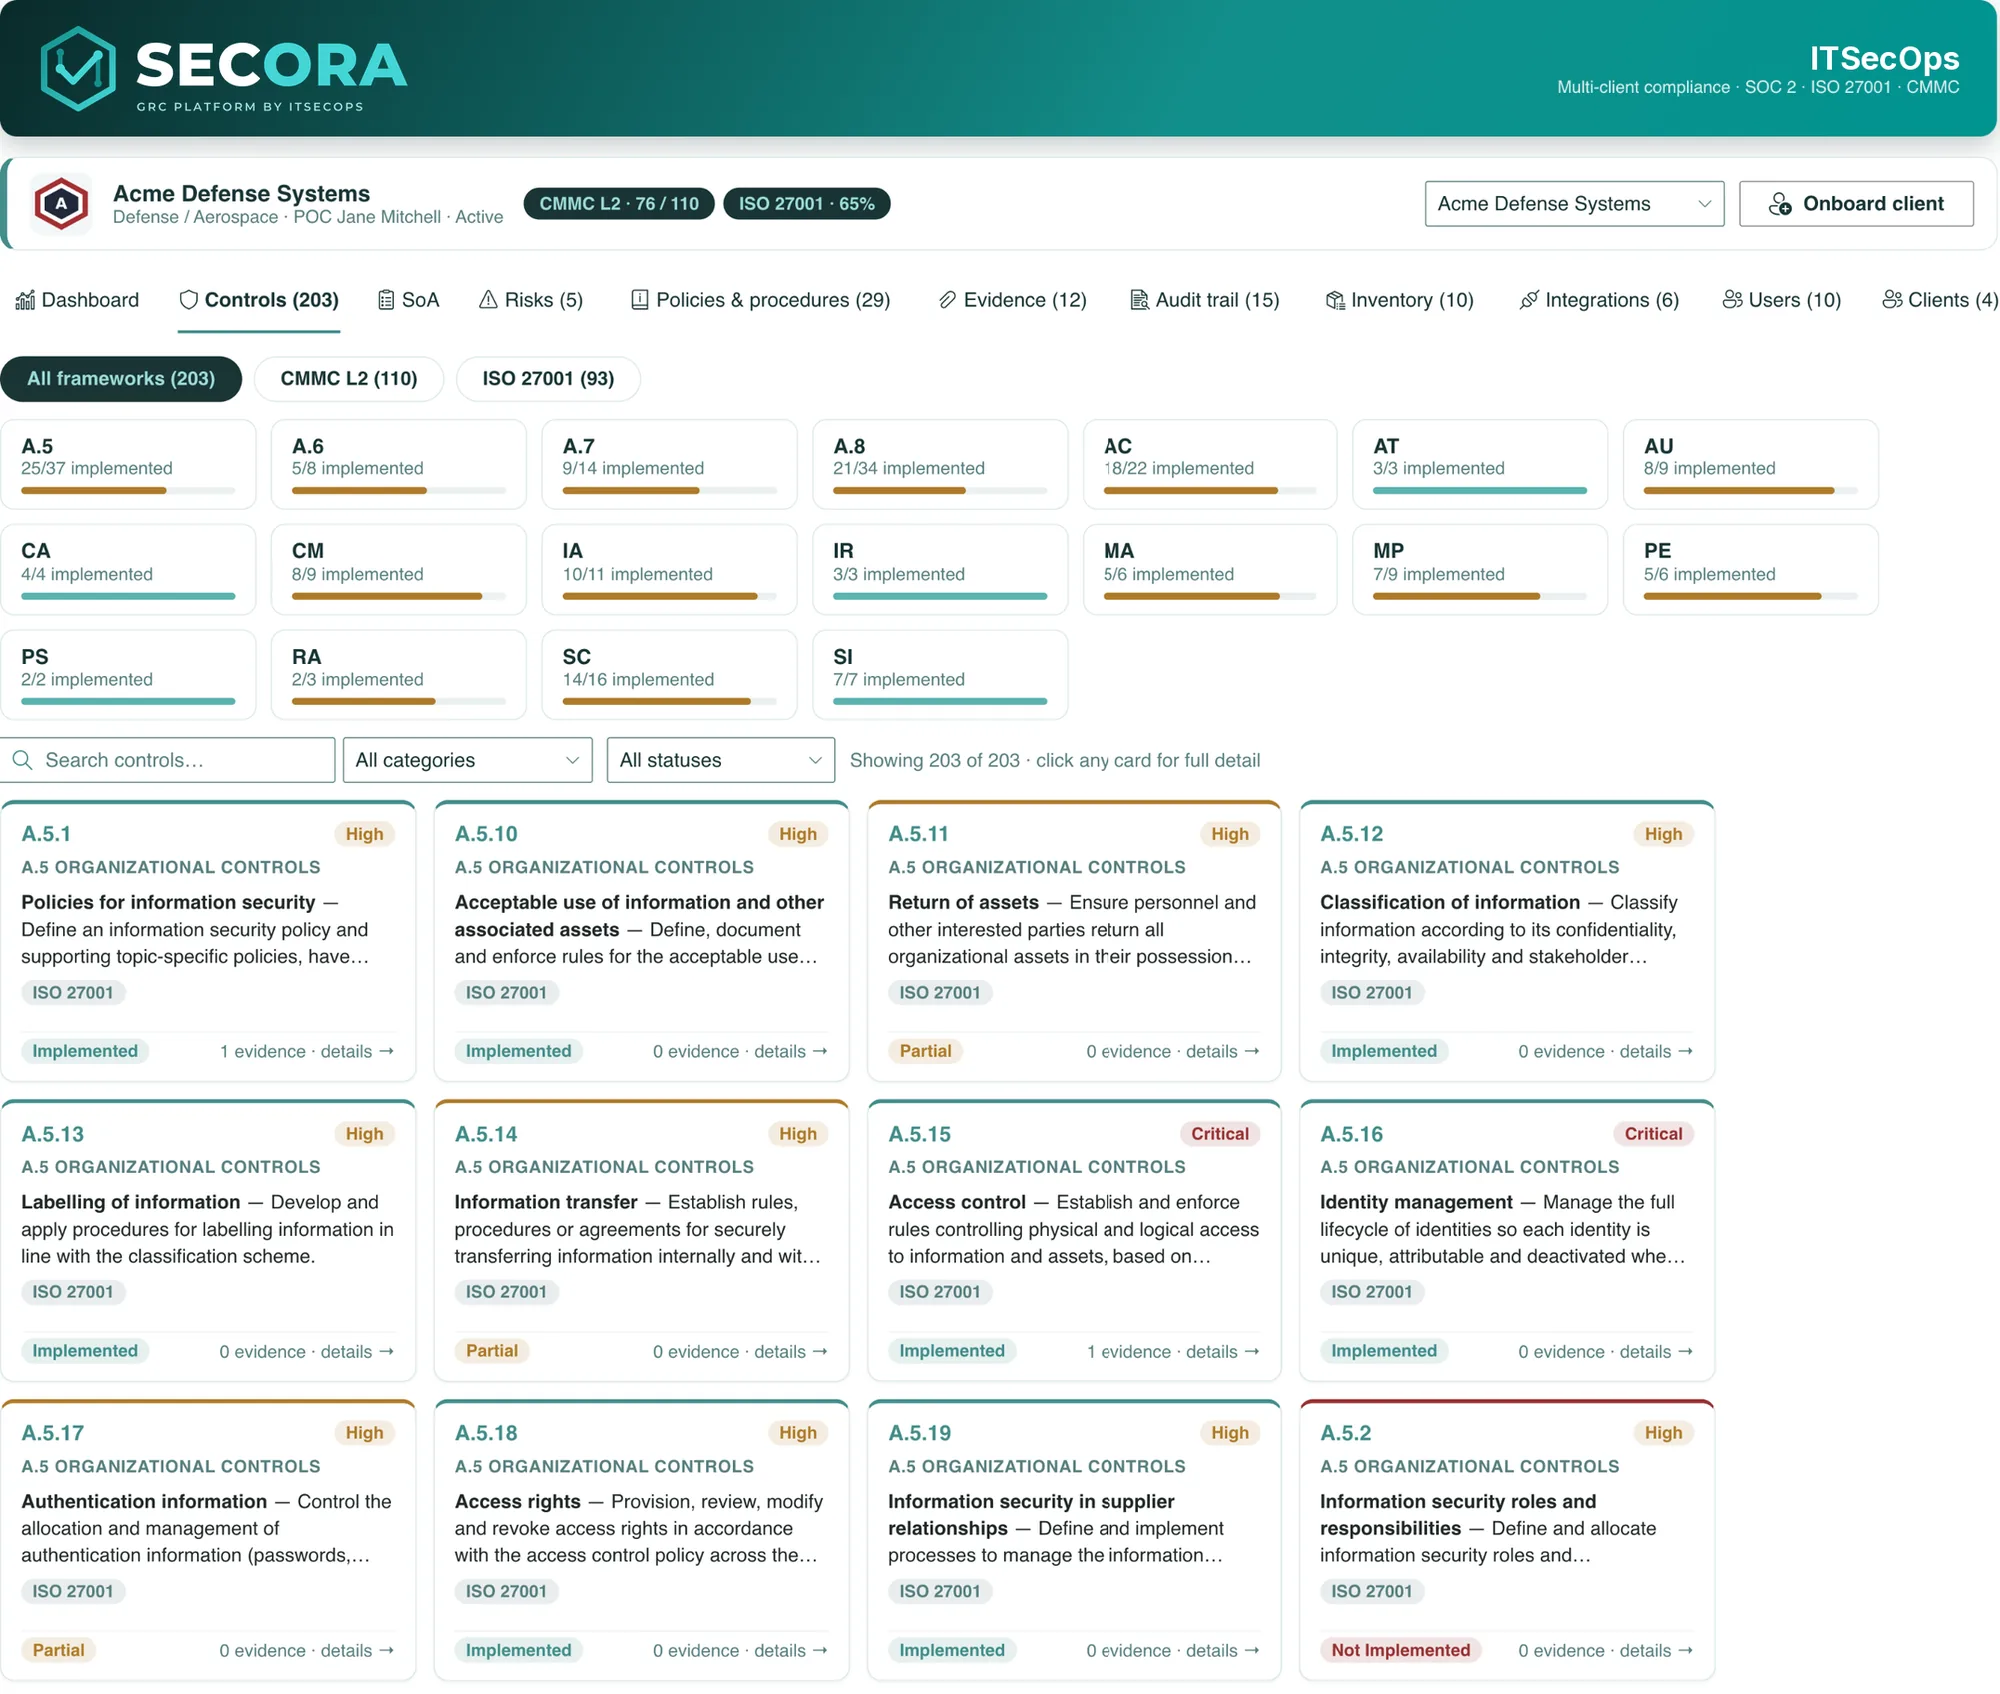
- 17 Level 1 and 110 Level 2 practices as control cards with family, priority, SPRS weight, owner, linked policies, evidence count and status.
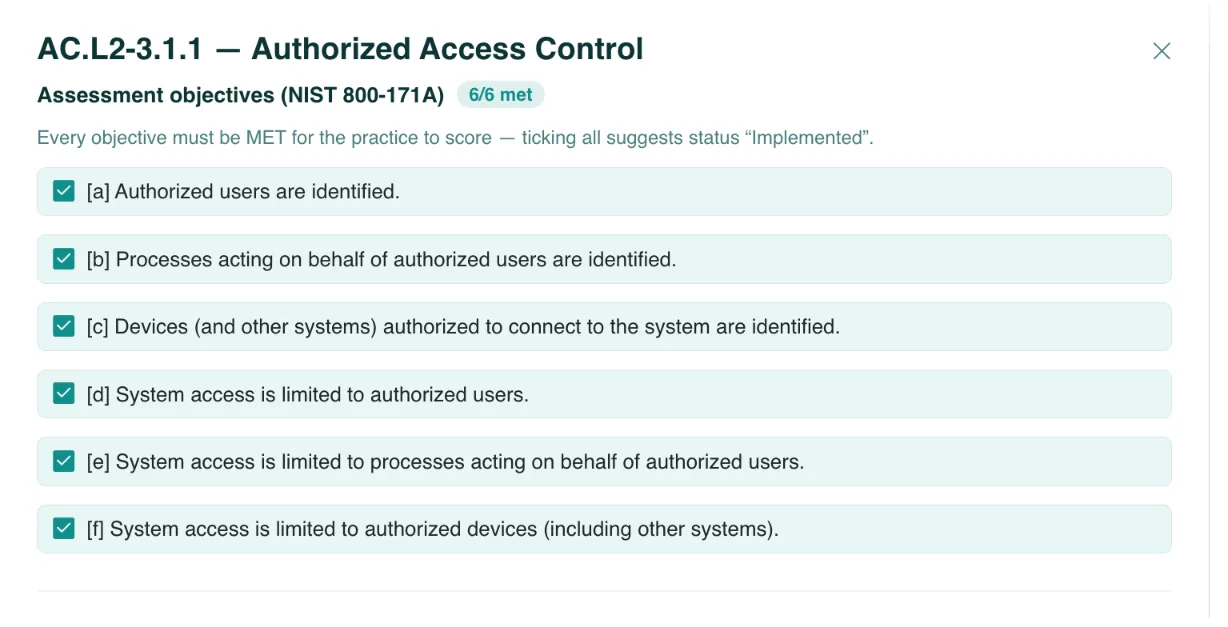
- NIST SP 800-171A assessment objectives per practice: tick [a] to [f] and the status suggests itself; every objective must be met for the practice to score.
- Official SPRS scoring: 5, 3 and 1 point deductions from 110, with 3.12.4 (the SSP) handled correctly so your number matches the DoD’s, plus the annual affirmation in the calendar.
- SSP and POA&M phases on the roadmap Gantt, with CUI scoping and enclave boundary review as recurring duties.
- Policies for every family generated from the template library and your scoping answers, including estate-specific hardening SOPs (FortiGate, Cisco, Ubiquiti, Dell) from your inventory.
- Evidence recipes for Microsoft 365 GCC, Entra ID, Intune and Sentinel: the exact report, format and menu path, with a freshness clock that flips a control amber after 90 days.
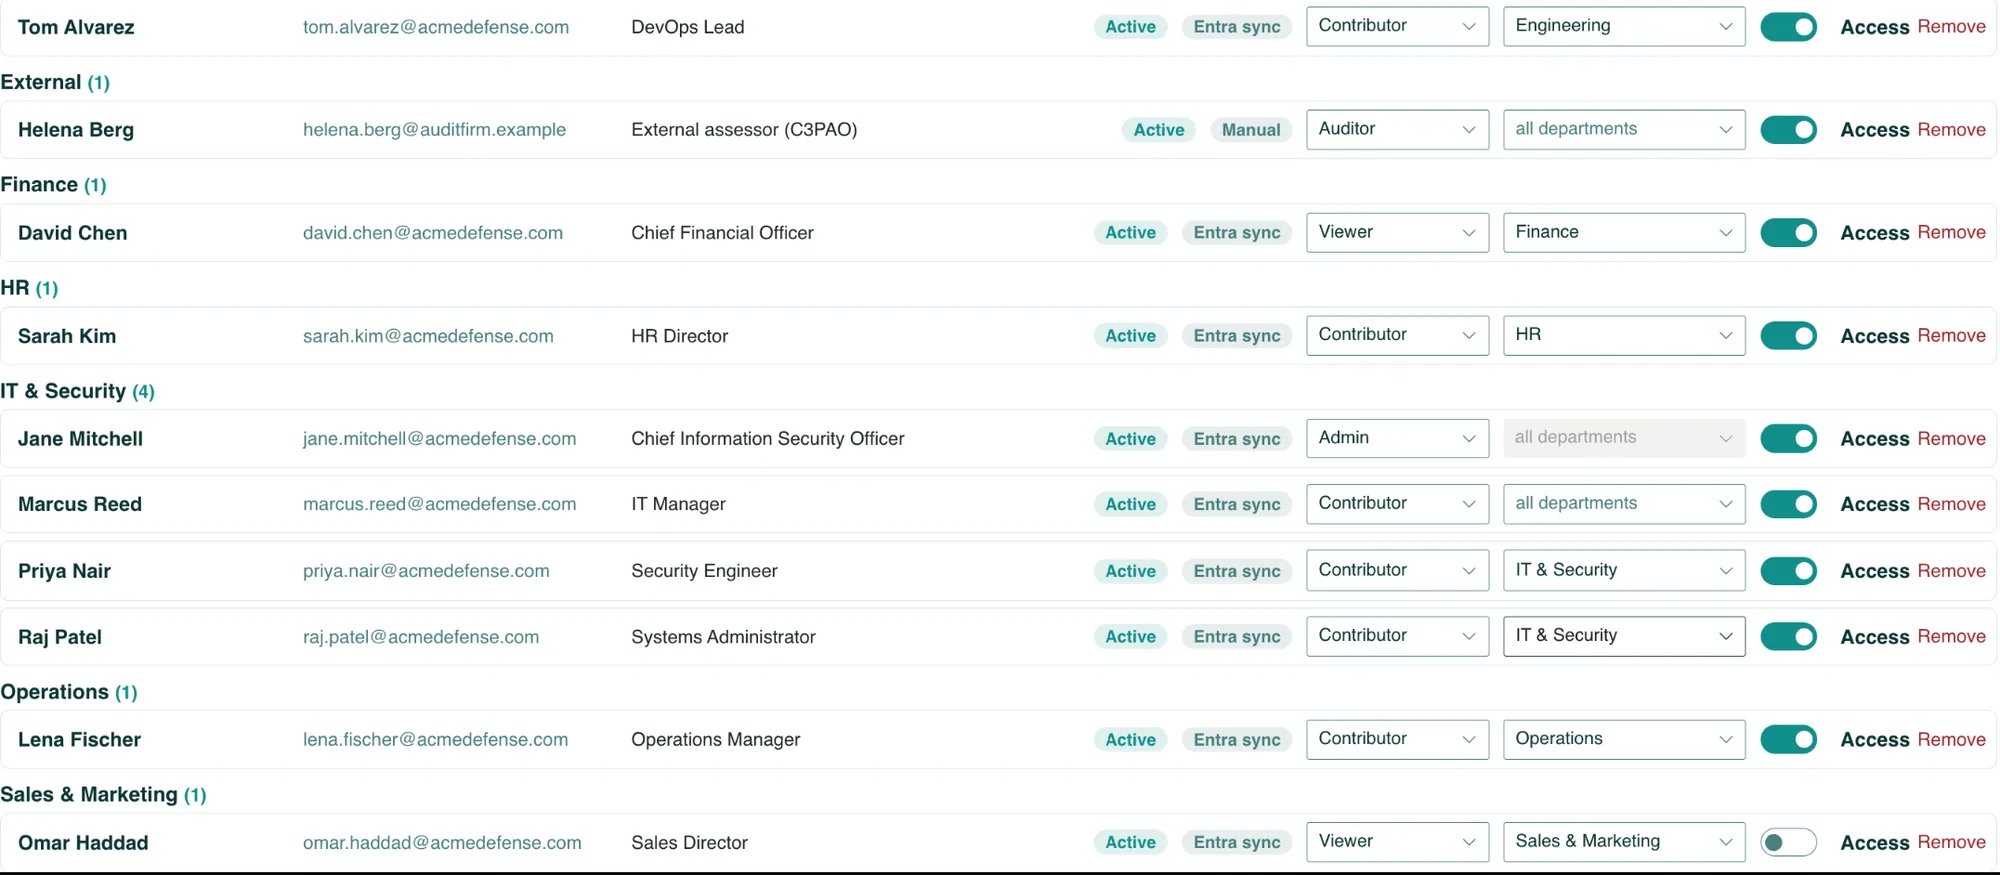
- Auditor role for your C3PAO or internal assessor: read-only, evidence-centric, may mark evidence Verified, cannot write even through the REST API.
- Cross-framework reuse with ISO 27001, SOC 2 and NIST CSF: 83% of the document workstream is shared in the demo workspace.
GCC, GCC High and commercial tenants
SECORA is a SharePoint Framework package, so it deploys wherever SPFx is supported: Microsoft 365 commercial, GCC, GCC High and SharePoint Server on-premises. Evidence, SSP and POA&M stay in the same tenant boundary as your CUI enclave, which simplifies the data-flow diagram your assessor will ask for.
CMMC consulting plus the platform
ITSECOPS runs CMMC gap assessments, remediation and readiness coaching for defense suppliers and their MSPs. SECORA is the portal those programmes run in: the same consultants who deploy it can run your gap assessment, write the SSP and coach the POA&M to closure. CMMC consulting services · Free SPRS score calculator.
ISO 27001 software with a live Statement of Applicability, inside your own Microsoft 365 tenant
Consulting and readiness services for this framework: ISO 27001 services by ITSECOPS.
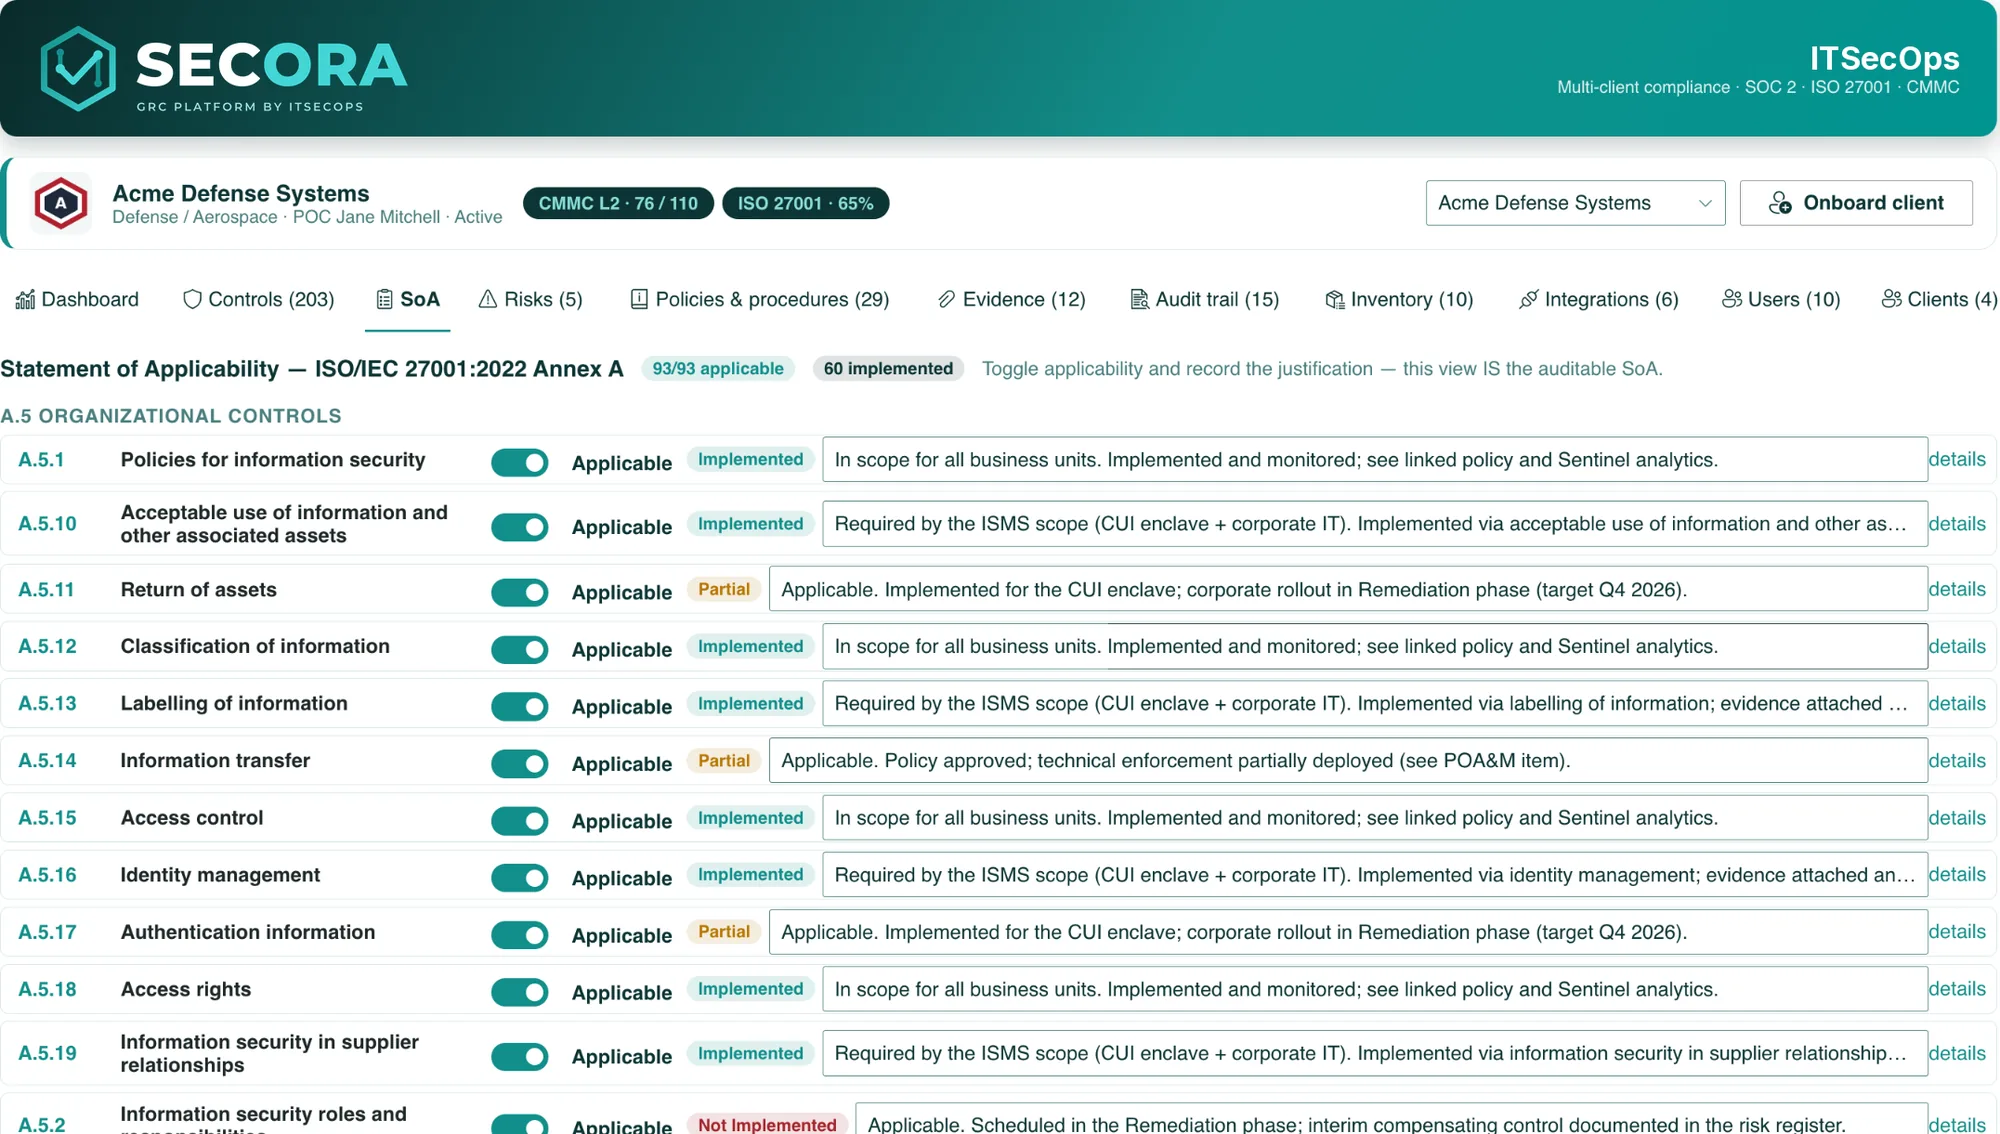
ISO 27001 is a management system, not a checklist, and certification bodies want to see it operating: a maintained SoA, risk treatment linked to controls, approved policies with versions, internal audit and management review on a cadence. SECORA runs all of it in your tenant, seeds the 93 Annex A controls and turns the SoA from a spreadsheet export into a live view.
ISO 27001:2022 restructured Annex A into 93 controls across organisational, people, physical and technological themes and added eleven new controls (threat intelligence, cloud services security, ICT readiness for business continuity, configuration management, information deletion, data masking, DLP, monitoring, web filtering, secure coding). Most organisations already do most of it; what the auditor tests is whether you can show the SoA, the risk treatment and the evidence trail, consistently, twelve months a year.
What SECORA seeds for ISO/IEC 27001:2022
- 93 Annex A controls as cards with theme roll-ups (A.5 to A.8), owner, linked policies, evidence and status, scored as percentage of Annex A implemented.
- Live Statement of Applicability: applicability toggle, status and justification per control in one view that is the auditable SoA, not an export.
- ISMS roadmap as a Gantt: context and scope, risk assessment and SoA, implement Annex A, operate and measure, internal audit and management review, certification audit.
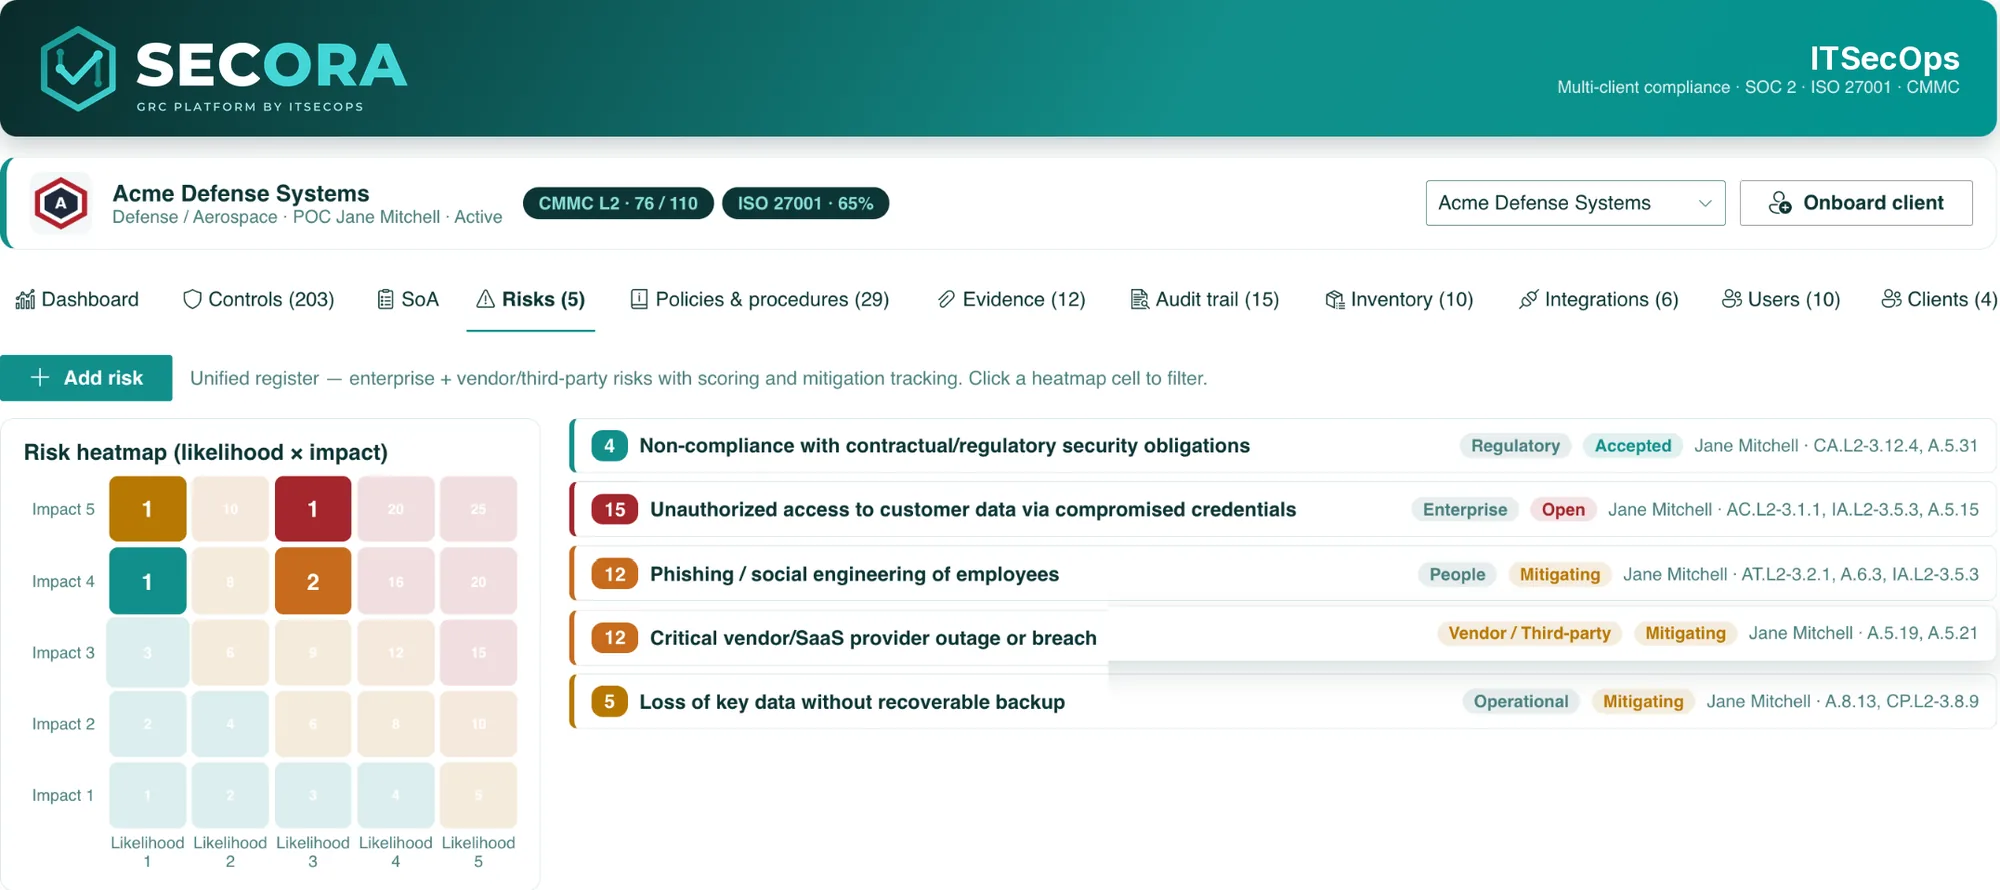
- Risk register with 5×5 heatmap, treatment plans, owners and mapped controls, so risk treatment demonstrably drives the SoA.
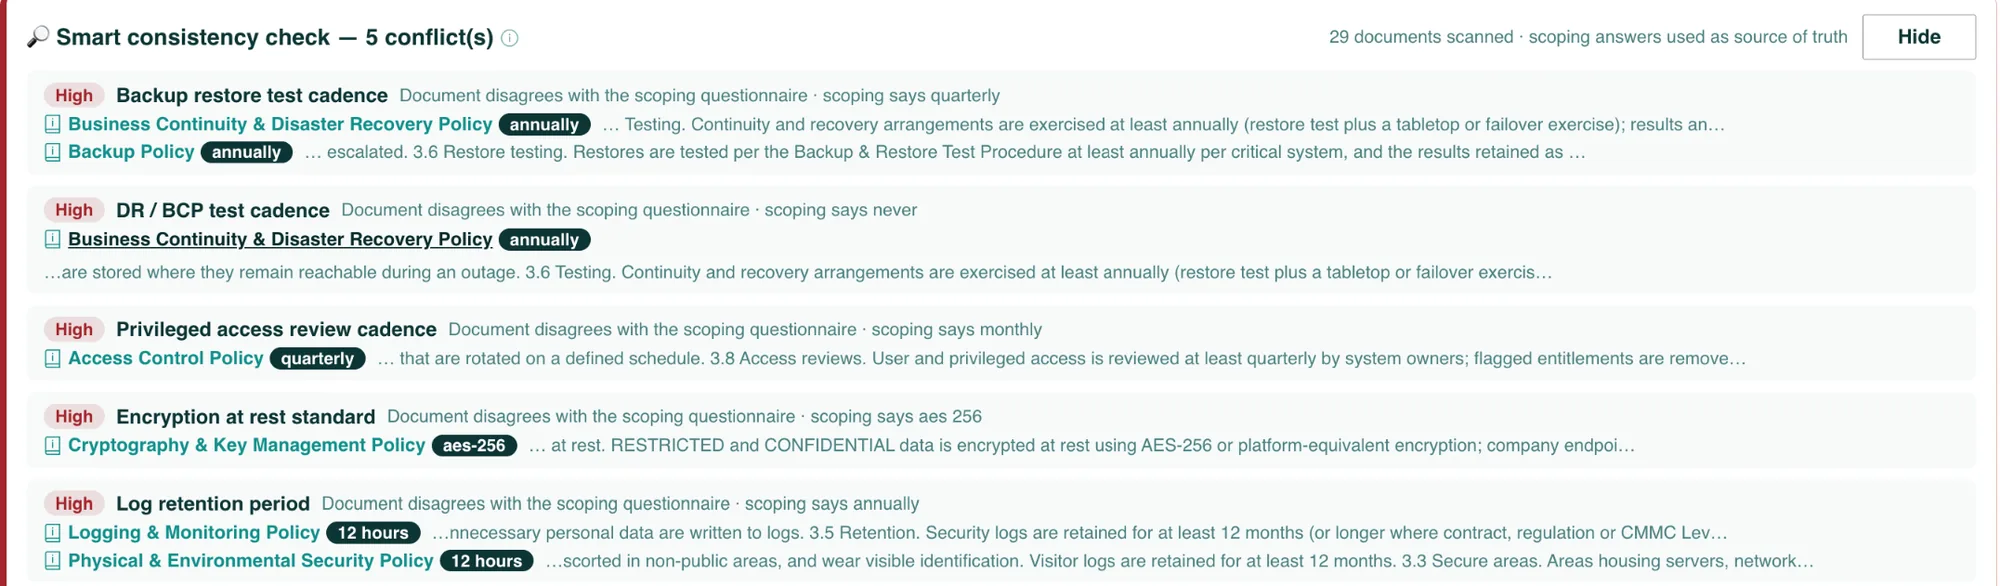
- Policy library: 29 templates merged with your scoping answers, approved by email, versioned, exported as branded PDFs, with the consistency check catching a policy that says annually while the procedure says quarterly.
- Compliance calendar with internal audit, management review, policy re-approval, risk assessment refresh, access reviews and awareness training scheduled with owners and reminders.
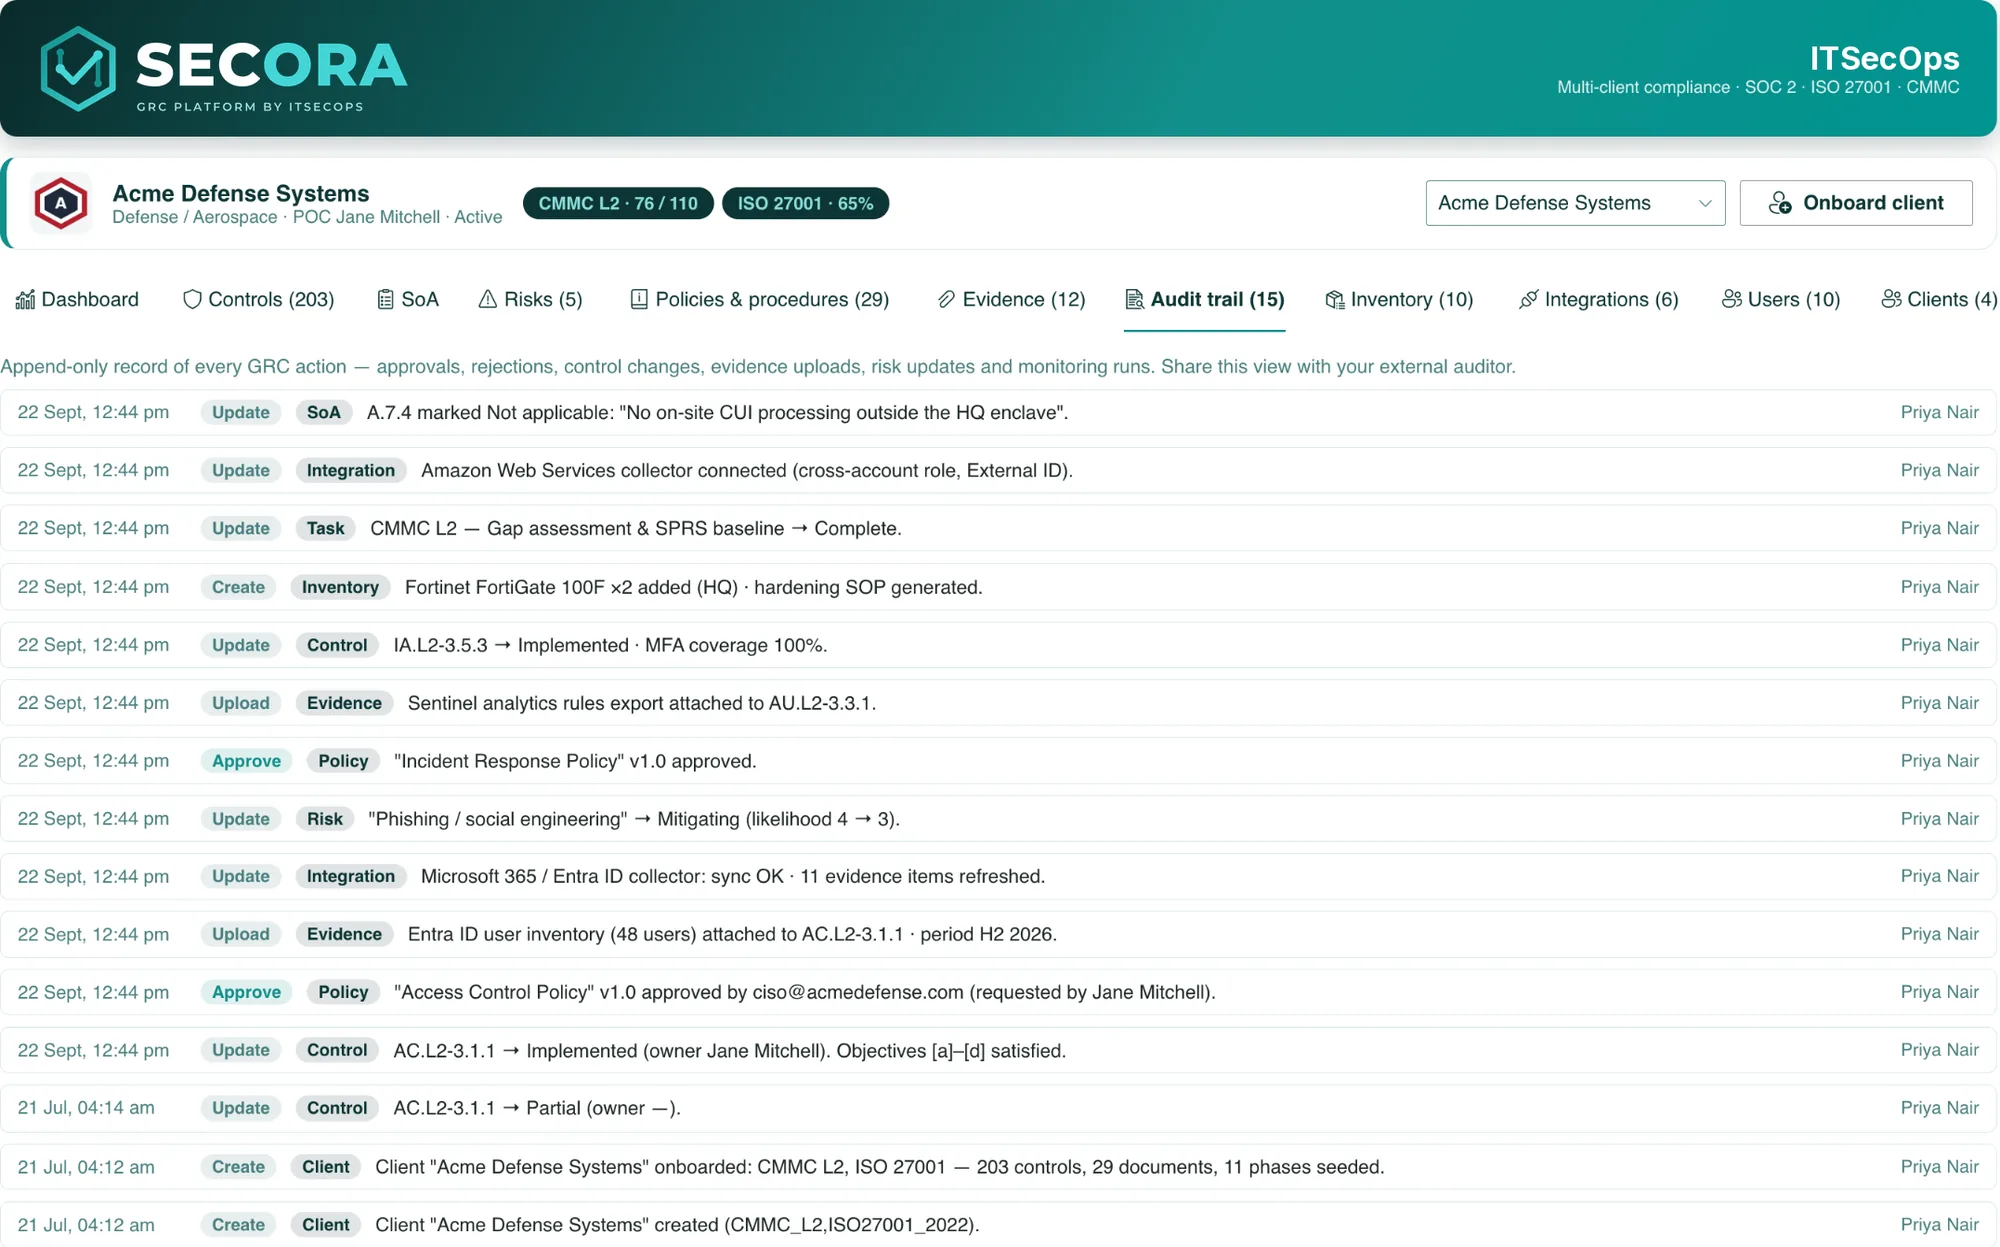
- Auditor role for your certification body: read-only, may mark evidence Verified, shareable audit trail.
ISO 27001 together with SOC 2, NIS2 or CMMC
An ISO ISMS is the natural backbone for other frameworks. In SECORA, adding SOC 2 reveals the observation-window criteria, adding NIS2 reveals the Article 21 reporting and management duties, adding CMMC reveals CUI scoping and SPRS. Shared controls collect evidence once. See the overlap for your combination.
Readiness services
ITSECOPS runs ISO 27001 gap assessments, ISMS implementation and audit-readiness coaching for SMBs and MSPs across Europe, the Nordics, the Gulf and North America. SECORA is the portal those engagements run in. ISO 27001 readiness services.
SOC 2 compliance software that does not add another vendor to the SOC 2
Consulting and readiness services for this framework: SOC 2 services by ITSECOPS.
SOC 2 Type II is about operating effectiveness over a window, which is why the automation platforms exist. It is also why the platform you choose becomes part of the system your auditor looks at. SECORA gives you the Trust Services Criteria, continuous checks, an evidence library with a freshness clock and a compliance calendar, inside your own tenant, licensed once.
Sixty to seventy percent of first-time SOC 2 organisations use a compliance platform, and the first-year all-in cost sits between $85,000 and $110,000 once the audit and remediation are included. The platform slice of that is a subscription in almost every case: Vanta, Drata and Secureframe medians of $20,000 to $25,000 a year, priced by headcount and framework, with 5 to 10% uplifts at renewal. SECORA changes the shape of that line.
What SECORA seeds for SOC 2 Type II
- Trust Services Criteria (CC1 to CC9 Common Criteria, A1 Availability, C1 Confidentiality, PI1 Processing Integrity) seeded as controls with owners, linked policies, evidence and status.
- Observation-window roadmap: readiness, remediation, Type I point in time, the Type II window, audit, on a Gantt with a today marker.
- Continuous checks for your Microsoft estate with an immutable run history: MFA coverage, Conditional Access, stale accounts, device compliance, Sentinel analytics.
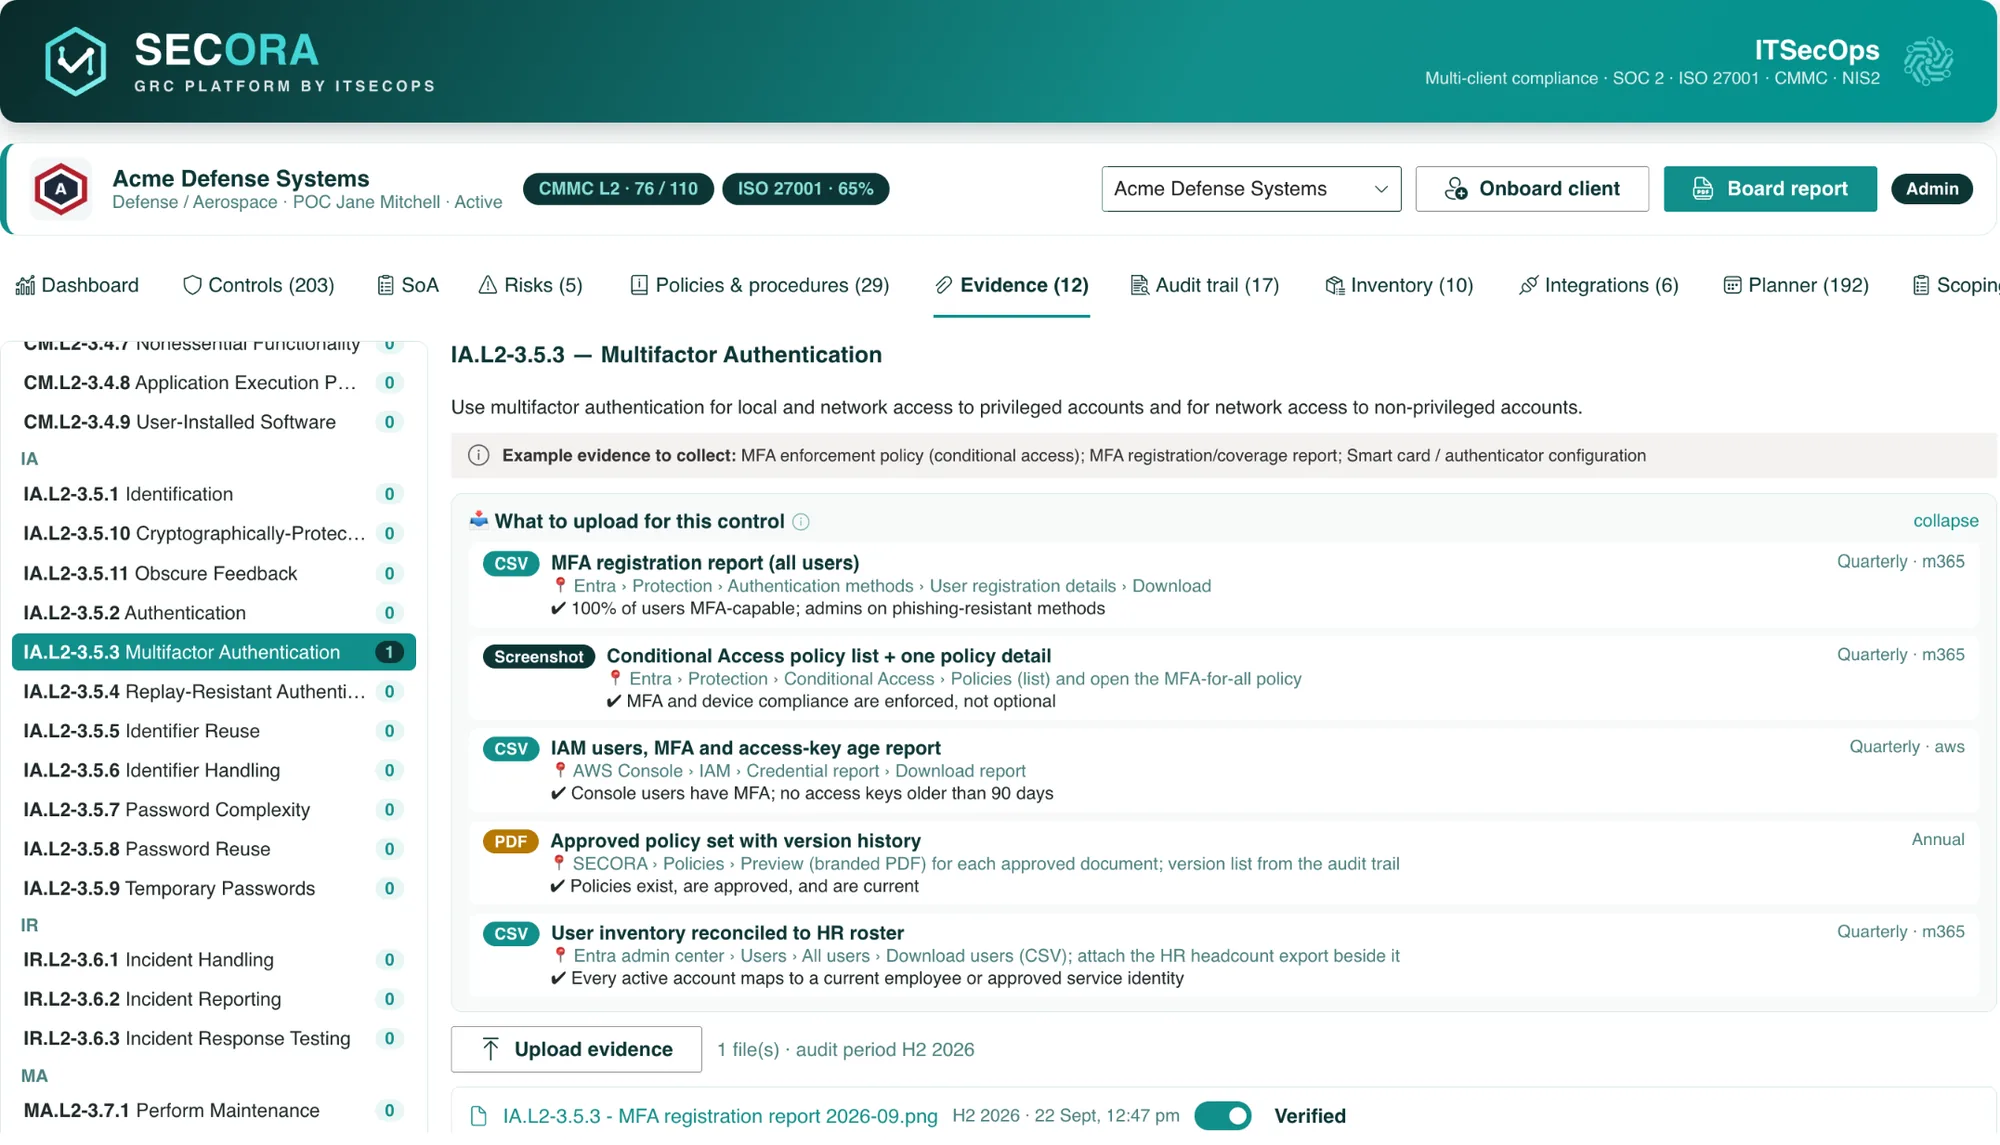
- Evidence library with per-control recipes (the exact export, format and menu path), an audit-period tag and a freshness clock that flips the control amber after 90 days.
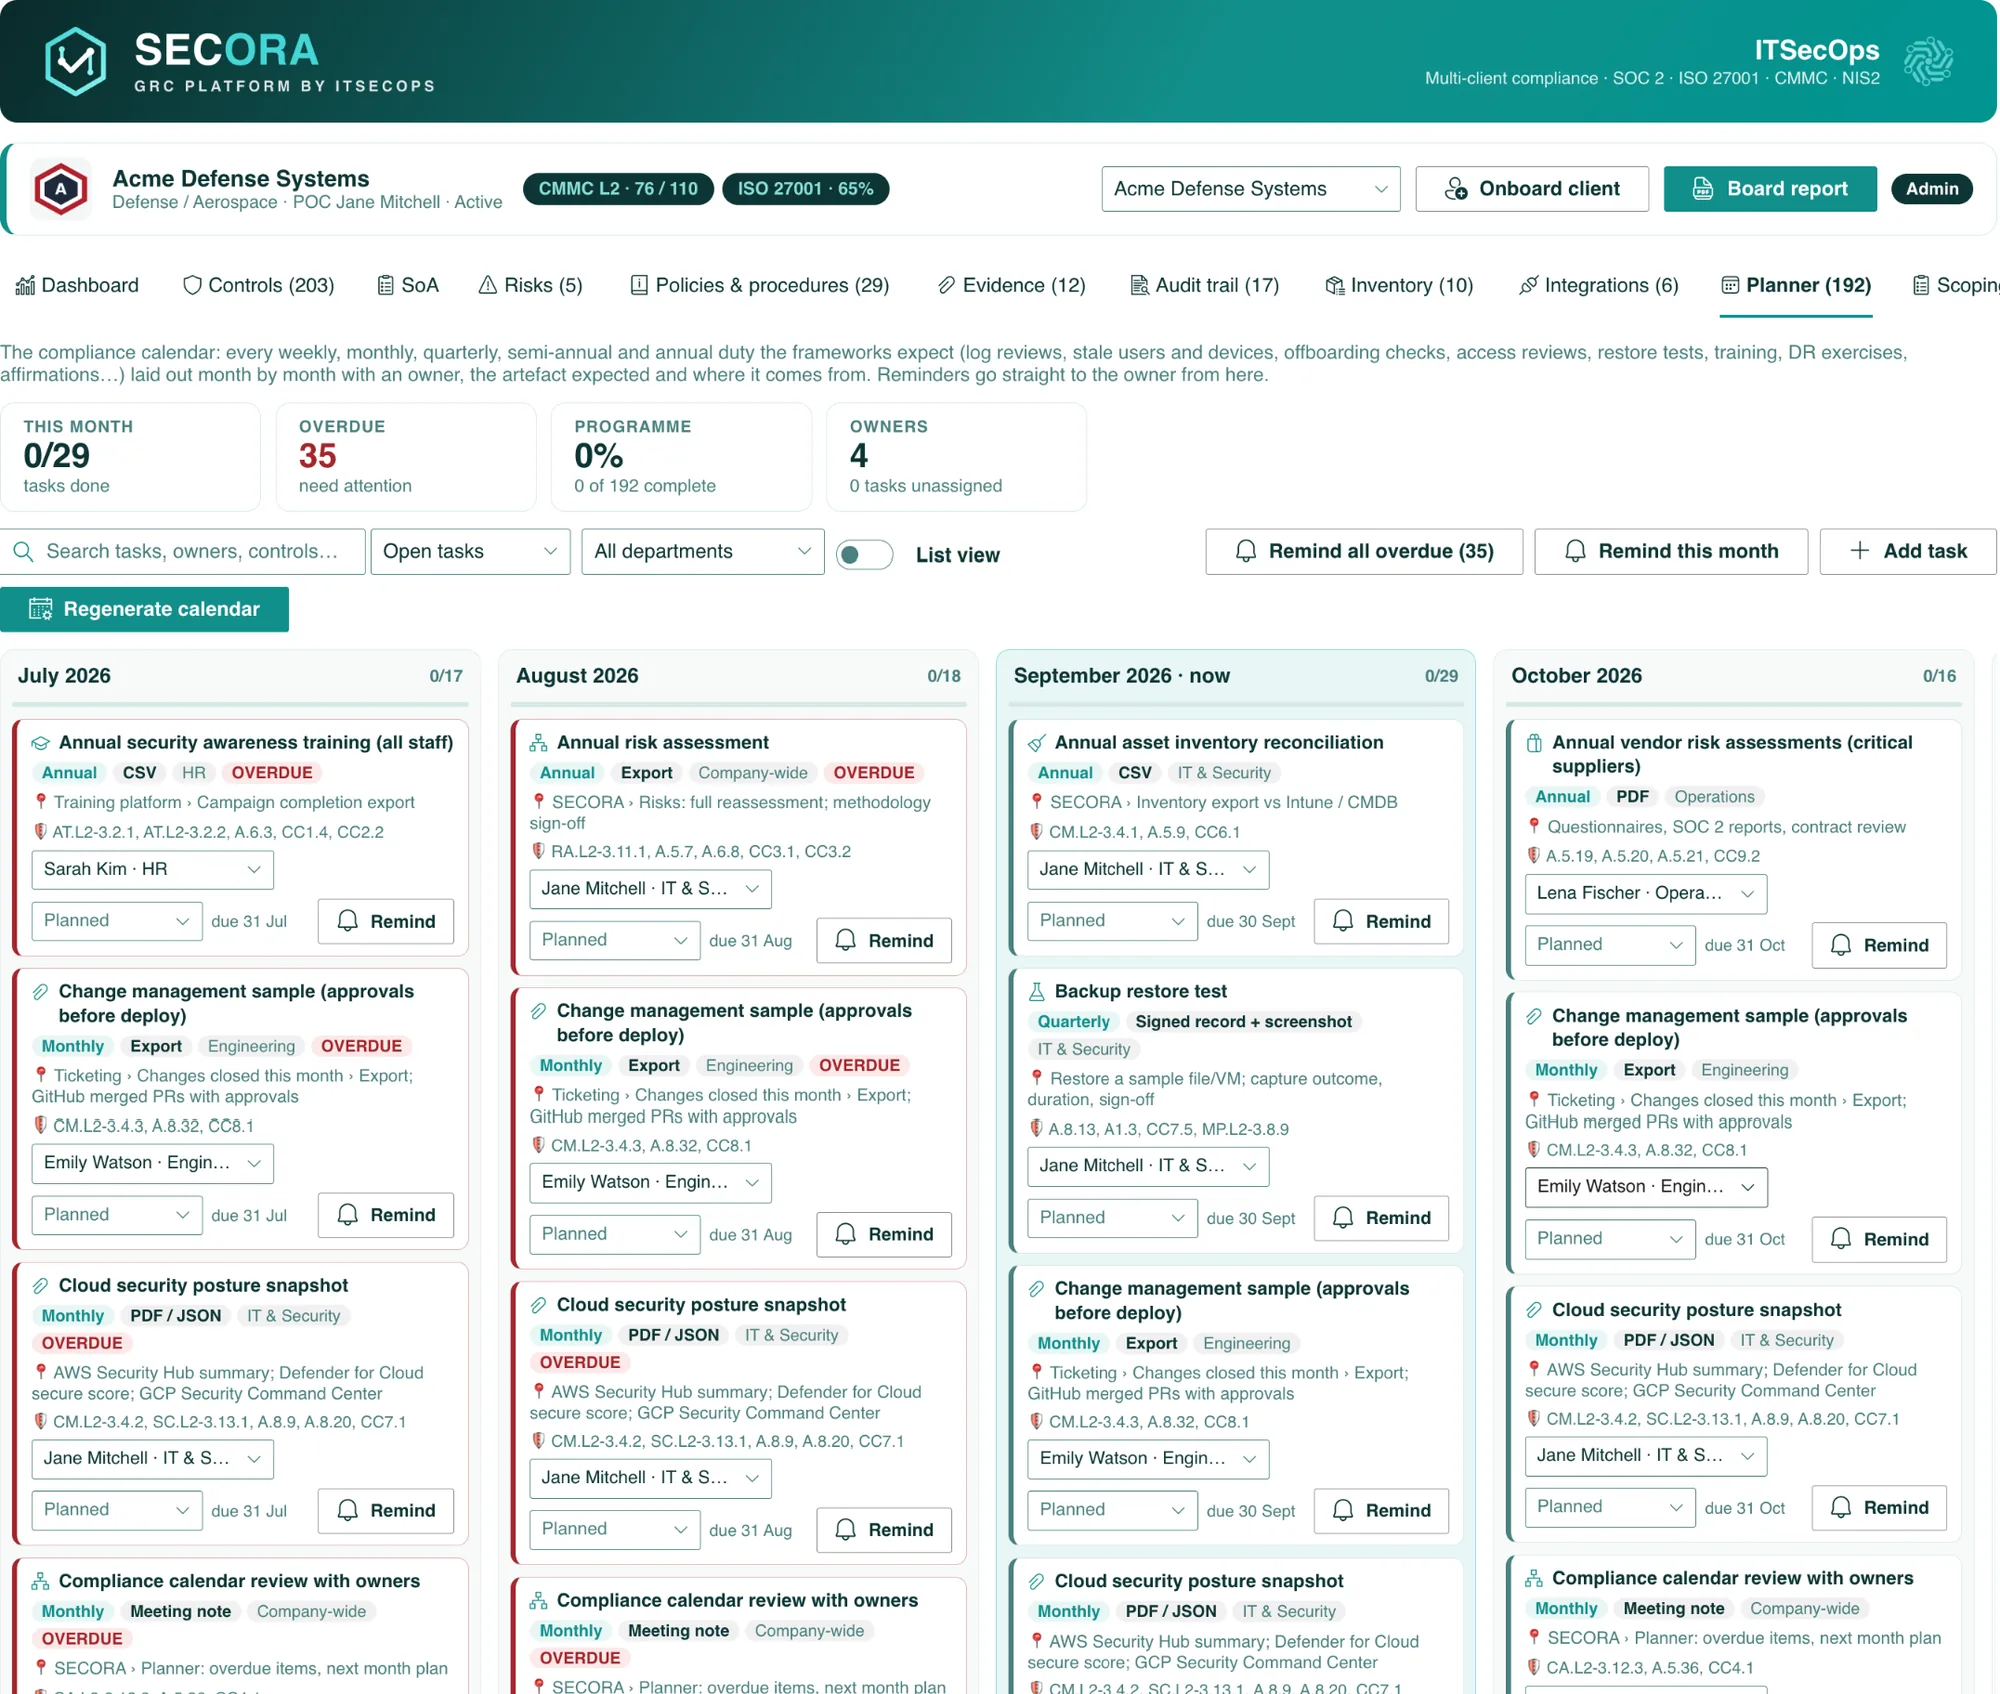
- Compliance calendar: access reviews, change management samples, restore tests, vulnerability reviews, vendor reviews, training and incident exercises scheduled with owners and reminders, so every month of the window has evidence.
- Risk register and vendor risk with control mapping (CC3, CC9).
- Auditor role for your CPA firm: read-only, evidence-centric, marks evidence Verified.
SOC 2 without Vanta or Drata
The automation platforms are excellent for cloud-native startups with hundreds of SaaS integrations. If you are a Microsoft 365 organisation, the evidence an auditor samples comes from Entra ID, Intune, Purview, Sentinel and your ticketing system, and SECORA collects it inside the tenant without a new vendor, new OAuth grants or per-seat fees. See the SECORA vs Vanta and SECORA vs Drata comparisons and the three-year cost calculator.
SOC 2 readiness services
ITSECOPS runs SOC 2 readiness, gap assessment and remediation for SMBs and MSPs; SECORA is the portal the programme runs in. SOC 2 readiness services.
NIS2 compliance tool that keeps the evidence in your own EU tenant
Consulting and readiness services for this framework: NIS2 services by ITSECOPS.
NIS2 asks essential and important entities to prove ten families of measures, report incidents within 24 and 72 hours and hold management personally accountable. Twenty-three of twenty-seven member states have transposed it, national audits have started and the Commission referred Ireland, Spain, France and the Netherlands to the CJEU in July 2026 for being late. A US-hosted SaaS holding your security documentation is a strange way to demonstrate resilience. SECORA runs inside your own Microsoft 365 tenant in your EU geography.
Enforcement is real: about 1,500 essential-entity audits in 2025 to 2026 and roughly €885,000 in national fines already issued, with the Netherlands (Cyberbeveiligingswet in force 15 August 2026), Germany (NIS2UmsuCG in force December 2025), Poland, Austria and Italy all on dated timelines. ITSECOPS maintains country guides for the Netherlands, Germany, Norway, Denmark, Belgium, Poland, Austria, Italy and France.
What SECORA seeds for NIS2
- Article 21 measures (risk analysis and information system security, incident handling, business continuity and crisis management, supply chain security, secure acquisition and development, effectiveness assessment, cyber hygiene and training, cryptography, HR security and access control, MFA and secure communications) mapped to the shared control library.
- Incident reporting readiness: the 24 hour early warning and 72 hour notification tracked as controls, an incident register review in the calendar and a tested IR procedure with a tabletop exercise scheduled annually.
- Supply chain risk: vendor and third-party risks in the unified register with 5×5 scoring, quarterly supplier check-ins and annual critical-supplier assessments.
- Management accountability evidence: quarterly board or management cybersecurity briefing with the one-click board report as the artefact, training records for management.
- ISO 27001 reuse: an existing or planned ISMS covers most Article 21 measures; add NIS2 and only the extra controls appear.
- Country-specific control sets (for example Belgium’s CyFun, Germany’s BSI expectations, Norway’s NSM grunnprinsipper) loaded by ITSECOPS during deployment.
Data residency by construction
SECORA stores every record in your tenant’s SharePoint lists and libraries, in your Microsoft geography, under Microsoft’s EU Data Boundary commitments. There is no transfer of security documentation to a US vendor to justify to your national authority, no new processor to add to your records, and no OAuth grant into your tenant from a third-party GRC cloud. Compare that with the hosting column of the mainstream platforms.
NIS2 readiness from Norway and the EU
ITSECOPS runs NIS2 gap assessments and readiness programmes from Norway and India for entities across the Nordics, Benelux, Germany, Poland, Austria, Italy and France, in local languages. NIS2 hub and country guides.
HIPAA compliance software that keeps the safeguards, and the evidence, in your tenant
Consulting and readiness services for this framework: HIPAA services by ITSECOPS.
Covered entities and business associates already run on Microsoft 365 with BAAs in place. Adding a separate SaaS to hold your HIPAA risk analysis, policies and audit evidence means another business associate, another BAA and another place PHI-adjacent data can leak. SECORA seeds the Security Rule safeguards as controls inside the tenant you already covered.
The HIPAA Security Rule expects a documented risk analysis, administrative, physical and technical safeguards, workforce training, business associate management and audit controls that are actually reviewed. Most enforcement actions cite a missing or stale risk analysis and unreviewed access logs, not exotic gaps. SECORA makes both recurring, owned and evidenced.
What SECORA seeds for HIPAA
- Administrative, physical and technical safeguards seeded as controls with owners, linked policies and evidence hints, mapped to the shared library so SOC 2 or ISO work is reused.
- Risk analysis and risk management in the 5×5 register with mitigation tracking and annual refresh in the calendar.
- Business associate inventory in the vendor risk register with annual BAA review.
- ePHI access audit log review scheduled monthly with the export as the artefact; Entra sign-in and Purview audit as evidence sources.
- Workforce training and sanctions policy with acknowledgement evidence per department.
- Contingency plan: backup restore tests quarterly, DR exercise annually, with signed records.
- Policies and procedures generated from templates and your scoping answers, approved by version.
HIPAA alongside SOC 2
Healthcare SaaS vendors usually carry both. In SECORA the SOC 2 security and confidentiality criteria and the HIPAA technical safeguards share controls and evidence; HIPAA adds the BAA inventory, ePHI log reviews and breach notification procedure. Model the overlap.
GDPR compliance software that does not add a processor to your records of processing
Consulting and readiness services for this framework: GDPR services by ITSECOPS.
The irony of most GDPR tooling is that it adds a processor: your records of processing, DPIAs and security evidence go to a SaaS vendor’s cloud, often outside the EU. SECORA runs inside your own Microsoft 365 tenant in your geography, reuses the ISO 27001 control base for Article 32 and keeps the registers where your DPO can see them.
Supervisory authorities have issued more than €5 billion in GDPR fines to date, and the pattern of recent decisions is consistent: missing records of processing, weak security measures under Article 32, late breach notification and unmanaged processors. Each of those is a register, a control or a recurring duty SECORA seeds.
What SECORA seeds for GDPR
- Article 30 records of processing as a register with annual review in the calendar.
- Article 32 security measures mapped to the ISO 27001 control base: encryption, access control, MFA, logging, backup and restore, business continuity, testing.
- Data subject request log with response-time tracking reviewed quarterly.
- DPIA register with annual review and links to risks.
- Processors and sub-processors in the vendor risk register with contract and transfer notes.
- 72 hour breach notification procedure tested in the annual tabletop, with the incident register reviewed quarterly.
- Policies: privacy, retention and deletion, data classification and handling, generated from templates and your scoping answers.
GDPR alongside ISO 27001 and NIS2
Article 32 and NIS2 Article 21 both point at the same technical measures an ISO 27001 ISMS already implements. In SECORA the three share the control base; GDPR adds the registers and DSR duties, NIS2 adds reporting and management accountability. Model your combination.
NIST CSF 2.0 software for organisations that report to a profile
Consulting and readiness services for this framework: NIST CSF 2.0 services by ITSECOPS.
NIST CSF 2.0 added Govern as a sixth function and is increasingly the language boards, insurers and US state regulators ask for. SECORA maps the 106 subcategories onto the same controls that already satisfy ISO 27001, SOC 2 or CMMC, so a CSF profile is a view of work you are doing anyway, reported the way the board wants it.
CSF is an outcomes framework: it does not tell you which control to implement, it tells you which outcome to achieve and lets you set a target profile and tier. That makes it perfect for reporting and hard to evidence without a control library underneath. SECORA supplies the library.
What SECORA seeds for NIST CSF 2.0
- Six functions and 106 subcategories (Govern, Identify, Protect, Detect, Respond, Recover) mapped to the shared control library.
- Current and target profile per subcategory with owner and evidence, and the gap as a roadmap.
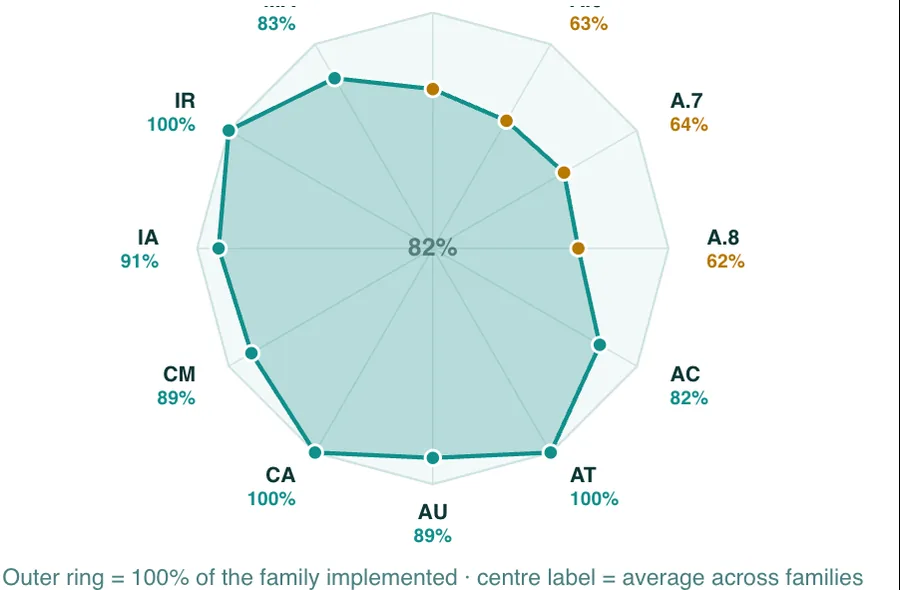
- Board report with the CSF spider web per function alongside readiness and risk posture.
- Reuse of ISO 27001, SOC 2, CMMC and NIS2 controls: one implemented control satisfies every equivalent subcategory.
- Detect and Respond evidence from Sentinel or your SIEM, incident register and tabletop exercises in the calendar.
- Govern evidence: policies, roles, supply chain risk and management review scheduled and recorded.
CSF as the reporting layer
Many organisations run ISO 27001 or SOC 2 for certification and report to the board in CSF terms. SECORA lets both be true: add CSF 2.0 and only the profile view appears, mapped to controls you already evidence. See the overlap.
How SECORA works in your tenant
SECORA is a signed SharePoint Framework (SPFx) package. ITSECOPS uploads it to your Microsoft 365 App Catalog (or a SharePoint Server you host), provisions a Compliance site with the GRC lists and an evidence library, applies permissions and seeds your frameworks. From then on your team signs in with Entra ID, under your MFA and Conditional Access, and every control, policy, risk, task and piece of evidence is a SharePoint record in your own Microsoft geography.
- Controls with family roll-ups, owners, priorities, SPRS weights, linked policies and evidence counts, mapped across every framework you select.
- Policies and procedures generated from 29 client-neutral templates, merged with your scoping answers, approved by email and exported as client-branded PDFs.
- Evidence library with a freshness clock per file, 55 evidence recipes that tell owners the exact report and menu path, and automated evidence from Microsoft 365, Entra ID and Sentinel.
- Risk register with a 5×5 heatmap, mitigation tracking and control mapping.
- Compliance calendar that turns 45 recurring duties into dated tasks with owners and reminders sent through Microsoft Graph.
- Scoping questionnaire, consistency check, roadmap, inventory, append-only audit trail and one-click board report.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Frequently asked
Yes. It applies the official NIST SP 800-171 DoD Assessment Methodology: 110 minus 5, 3 or 1 point deductions per unimplemented practice, with the SSP (3.12.4) handled per the methodology, so your number matches what you submit to SPRS.
Yes. SECORA is a SharePoint Framework package and deploys to Microsoft 365 commercial, GCC, GCC High and SharePoint Server on-premises. Deployment to a sovereign or GCC High environment is scoped during discovery.
Yes. The SoA is a live view in SECORA: every Annex A control has an applicability toggle, a status and a justification, and the view itself is what you show the certification body. Export to PDF is one click.
Yes. Add the auditor as an Auditor role: read-only across the portal, evidence-centric views, the ability to mark evidence Verified and a shareable append-only audit trail.
For Microsoft 365, Entra ID and Sentinel, yes, natively through read-only admin-consented Graph scopes with an immutable run history. For AWS, Azure, Google Cloud, GitHub and SIEMs a separate headless collector holds credentials outside SharePoint. Everything else has an evidence recipe with the exact export to upload.
Yes, as an Auditor: read-only across the portal, evidence-centric views, the ability to mark evidence Verified, and a shareable append-only audit trail. Enforced by SharePoint groups, not only by the screen.
It tracks them as controls with a tested procedure, an incident register reviewed quarterly and an annual tabletop exercise, and it evidences management notification. The actual notification is made by you to your CSIRT or competent authority.
It covers the Article 21 measure areas but NIS2 adds legal duties: incident reporting timelines, management accountability and training, supply chain obligations and national registration. SECORA seeds those as extra controls on top of the ISO library.
No. SECORA stores controls, policies, risks, tasks and evidence about your safeguards. Evidence exports should be de-identified where possible; because the library is in your own tenant, anything sensitive stays under your existing BAA with Microsoft.
SECORA is software running in your tenant; ITSECOPS deploys and maintains the package and does not host your data. Whether your deployment support engagement requires a BAA depends on the access you grant during deployment and is agreed in the statement of work.
For SMBs that need Article 30 records, DSR logging, DPIAs, processor management and Article 32 security evidence, yes, inside the tenant. Large enterprises with consent management across many web properties may still need a dedicated privacy suite for that part.
In SharePoint lists in your own Microsoft 365 tenant, in your Microsoft geography, with retention labels and Purview audit. SECORA is not a processor of that data.
Yes. Current and target profile per subcategory with tier notes, reported in the board report alongside framework readiness.
Yes. Insurers increasingly ask CSF-aligned questions; the profile view and the evidence library give you dated, owned answers instead of a spreadsheet filled from memory.
In your own Microsoft 365 tenant or SharePoint Server: SharePoint lists for controls, policies, risks, tasks, inventory and the audit trail, and a versioned document library for evidence. SECORA has no cloud of its own and no vendor database.
No. SECORA is licensed per organisation with a one-time deployment fee and twelve months of maintenance included. Invite every control owner, department head and external auditor without changing the bill.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.