 SEC
 by ITSECOPS
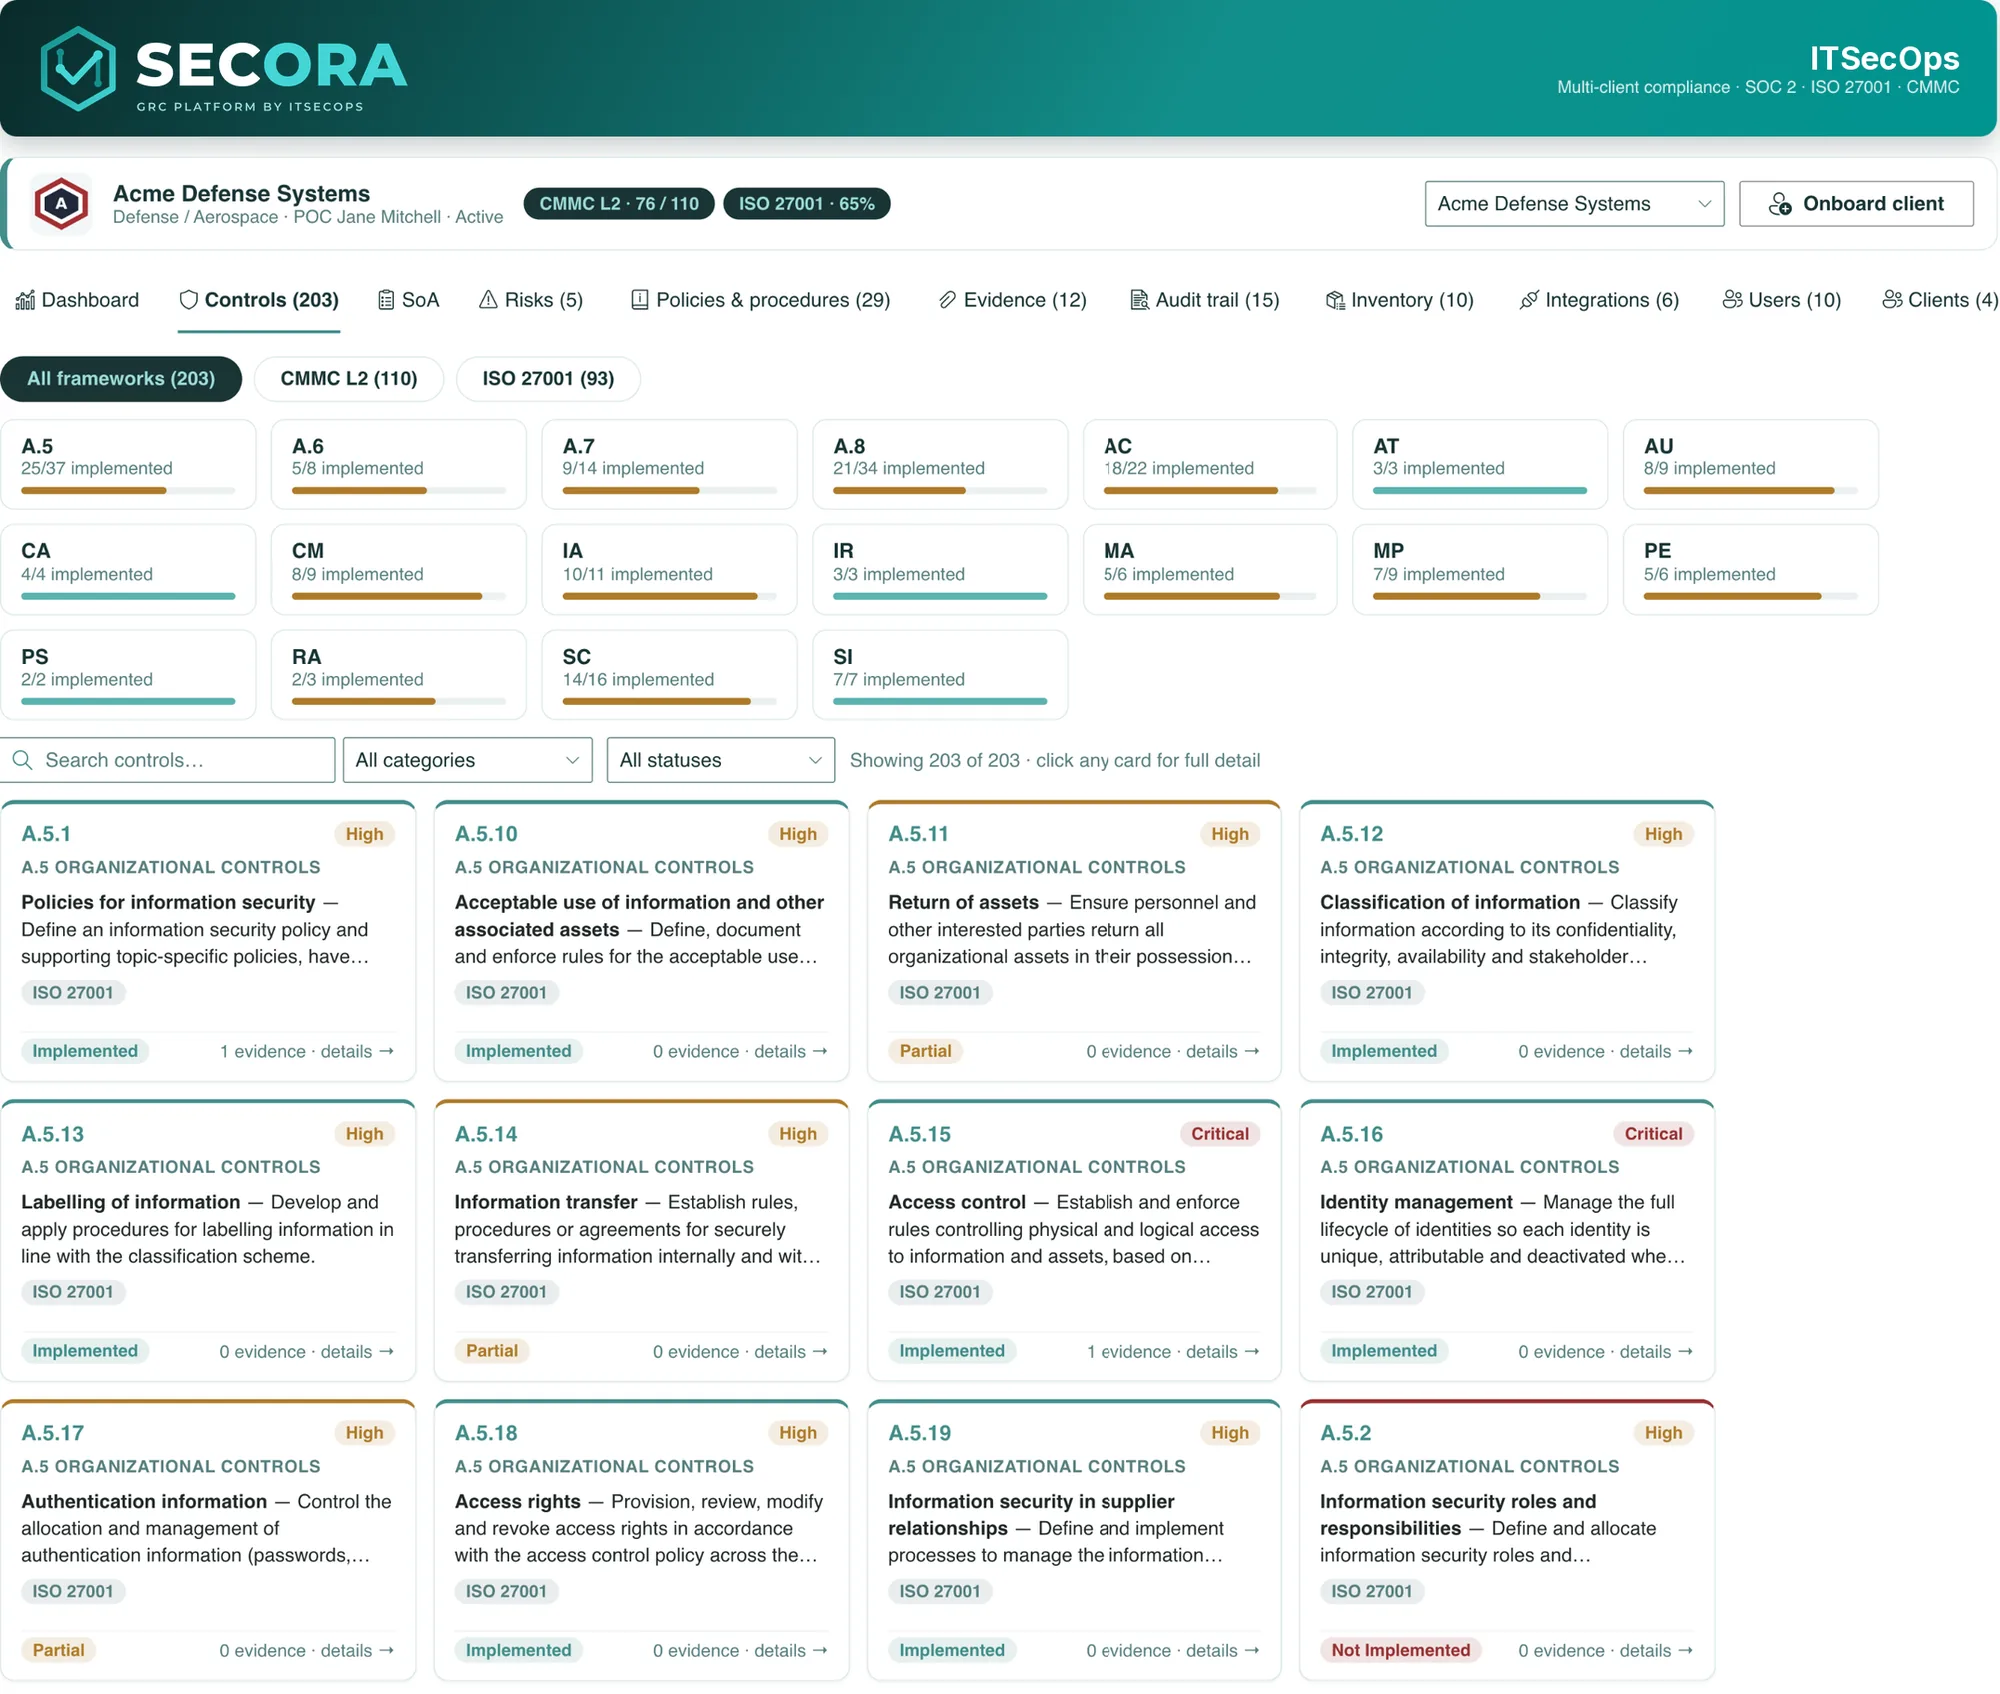
SECORA was built by a consultancy for consultancy work. The demo workspace on these pages is a multi-client instance: Acme Defense Systems is one of four clients, the switcher at the top re-scopes every tab, and every list row carries a client key. That design came from running CMMC, ISO 27001 and SOC 2 programmes for MSP partners in the US, the UK, the Nordics and the Gulf.
Two deployment models
Consultancy workspace
One SECORA instance in your Microsoft 365 tenant with a workspace per client. Every record (controls, policies, risks, evidence, tasks, audit trail) is partitioned by client key; the switcher re-scopes every tab instantly; isolation is verified both ways during deployment. Client POCs can be invited as guests scoped to their own workspace. Best for consultancies that own the programme and the evidence on behalf of the client.
Per-client tenant deployment
SECORA deployed into each client’s own Microsoft 365 tenant, with your consultants added as Contributors or Admins through B2B guest access. The client owns the data and the platform; you operate it. Best for MSPs whose clients (defense suppliers, regulated entities) must keep evidence in their own boundary.
Built for delivering compliance to many clients
- Client onboarding in one action: select frameworks and SECORA seeds controls, objectives, scoring, policy set and roadmap phases for that client.
- Branded output per client: policies and board reports carry the client’s name, logo and tagline; your consultancy appears as the preparer where you want it.
- Evidence recipes filtered by each client’s estate: a FortiGate client gets FortiGate SOPs, an AWS client gets CloudTrail recipes.
- Compliance calendar per client with owners from that client’s users register and reminders from your consultant’s mailbox or the client’s.
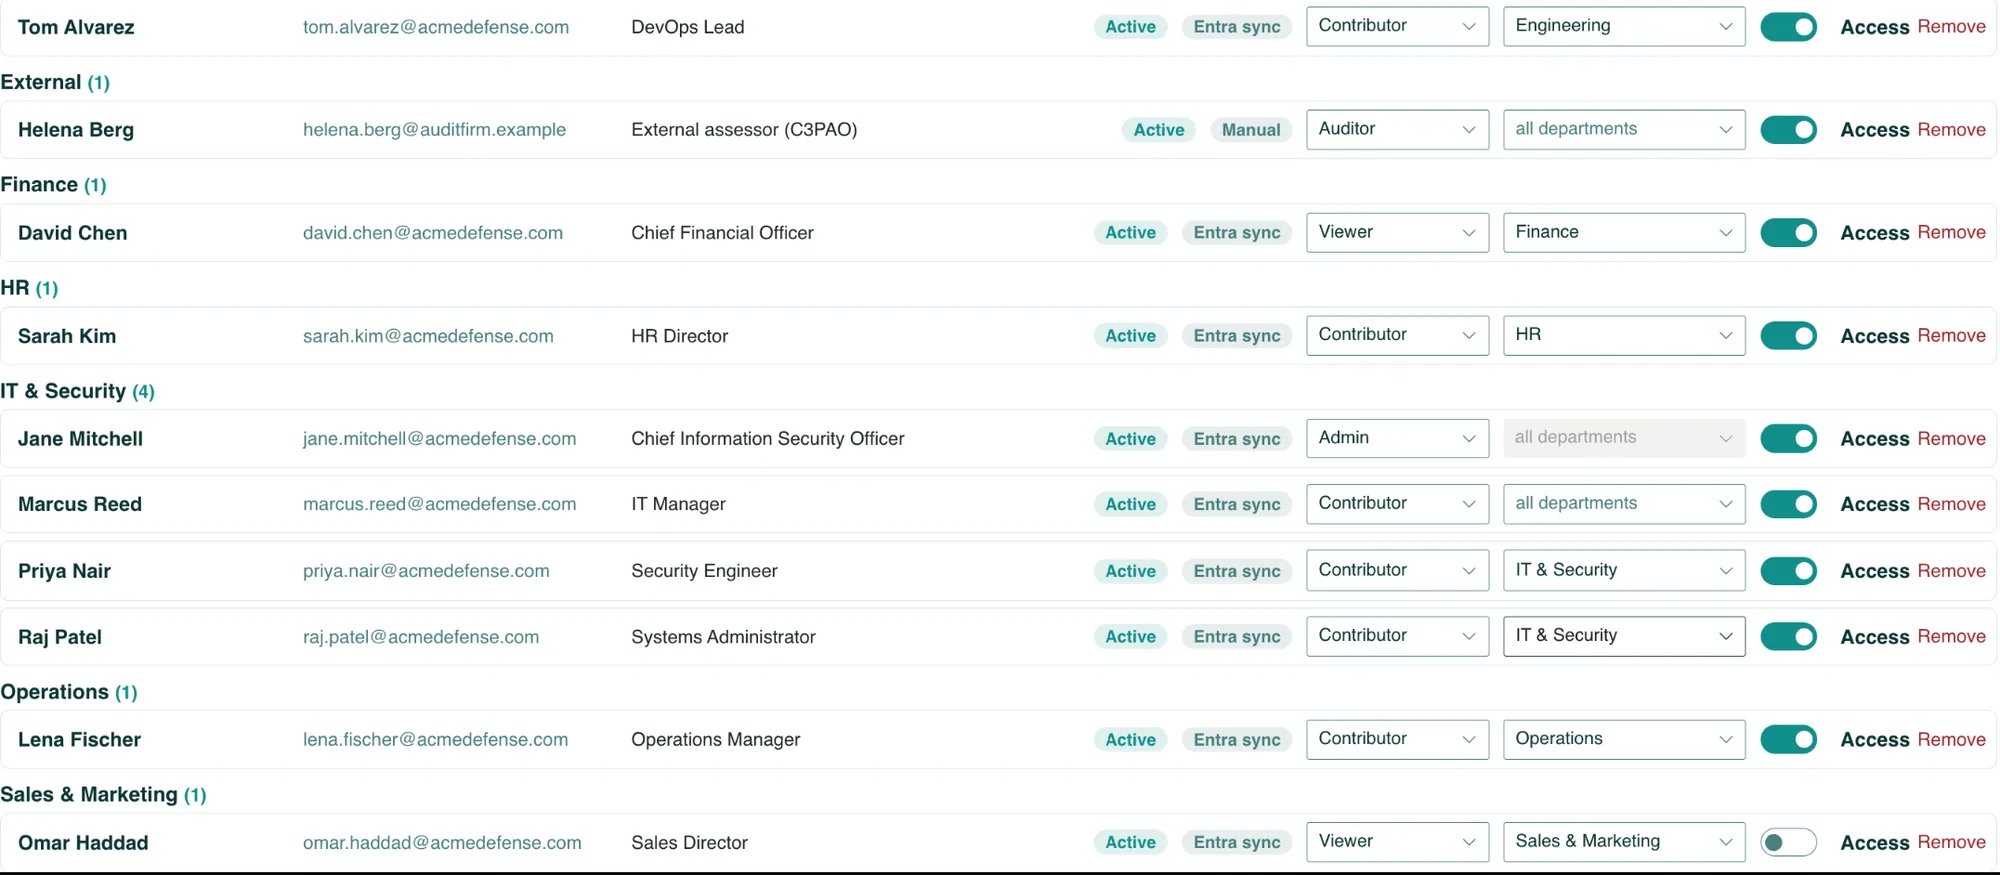
- Roles that match delivery: your consultants as Contributors across clients, client staff as department-scoped Contributors, assessors as Auditors.
- One audit trail per client, shareable with their assessor.
- No per-client SaaS invoice to reconcile against your own pricing; you set the margin.
CMMC for MSPs and their DIB clients
MSPs serving defense suppliers are themselves in scope where they touch CUI or provide security protection assets. SECORA supports both sides: your own CMMC Level 2 programme and each client’s, with 800-171A objectives and SPRS scoring that matches the DoD’s. After the July 2026 Phase 2 suspension, self-assessment evidence still has to live somewhere; SECORA gives each client its own boundary. CMMC consulting.
White-label and staff augmentation
ITSECOPS also delivers white-label SOC, NOC, helpdesk and compliance engineering to MSPs from its India delivery centre on US, UK and Australian hours. SECORA is the platform those engagements report into. White-label MSP support · Staff augmentation.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Frequently asked
Per organisation, one-time. The consultancy workspace model is one deployment in your tenant covering every client workspace; the per-client tenant model is a deployment per client tenant. Neither has per-seat or per-client SaaS fees. Volume terms for MSPs are quoted after discovery.
No. Every list row carries a client key, the client switcher re-scopes every tab and isolation is verified both ways at deployment. Client guests are scoped to their own workspace.
Policies, board reports and dashboards carry the client’s branding and your consultancy as preparer. The SECORA product name remains in the platform header; full re-branding is discussed case by case.
SECORA is a GRC portal, not an RMM. Evidence from your RMM, PSA or SIEM is attached through evidence recipes or the headless collector; tickets remain in your PSA.
In your own Microsoft 365 tenant or SharePoint Server: SharePoint lists for controls, policies, risks, tasks, inventory and the audit trail, and a versioned document library for evidence. SECORA has no cloud of its own and no vendor database.
No. SECORA is licensed per organisation with a one-time deployment fee and twelve months of maintenance included. Invite every control owner, department head and external auditor without changing the bill.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.