 SEC
 by ITSECOPS
Searching for a Vanta alternative usually starts with one of three frustrations: the renewal quote went up again, a second framework turned into a tier upgrade, or a customer or assessor asked where the evidence actually lives. This page answers all three with numbers.
Vanta in 2026: pricing model, hosting and what buyers report
Pricing model. Vanta prices per framework, by employee headcount band, with paid add-ons such as Vendor Risk Management (reported $5,000 to $15,000) and Trust Center (about $6,000). Single-framework SMB deals land between $12,000 and $28,000 a year; the observed median across 373 contracts is $20,000. Adding a framework mid-contract is reported to cost 15 to 30% more than at signing, and questionnaire volume caps push customers into higher tiers.
Hosting. Vanta runs in its own AWS environment, US region by default, with a Frankfurt option available on request at onboarding. Your policies, evidence and vendor data live in Vanta’s cloud, which means Vanta itself becomes a vendor in your third-party risk register and needs its own assessment.
AI. In March 2026 Vanta launched its AI Agent family (compliance, TPRM and Trust agents) that read evidence and suggest mappings. Useful for speed, but it means confidential evidence is processed by a third-party AI service, which some assessors and boards now ask about explicitly.
What Vanta does well. 400 plus integrations, a polished trust centre, a large auditor network and strong SOC 2 automation for cloud-native startups. If you are a SaaS company on AWS or GCP with no Microsoft estate and you need a public trust page this quarter, Vanta is a rational choice.
Where SECORA is different
Your tenant, not theirs. SECORA is deployed as a signed SharePoint Framework package into your Microsoft 365 tenant (or on-premises SharePoint Server). Controls, policies, risks, evidence and the audit trail are SharePoint lists and libraries under Microsoft’s encryption, retention labels, eDiscovery and DLP. Nothing leaves your estate and no new vendor enters your risk register.
One price, no seats, no per-framework charges. A one-time deployment fee per organisation with twelve months of ITSECOPS maintenance included. Invite every control owner, department head, internal auditor and external assessor. Add ISO 27001 to your SOC 2 programme later and only the extra controls appear; the shared 83% of documents is already done.
No AI black box. Mapping between frameworks is explicit and reviewable. Policies are generated deterministically from templates merged with your scoping answers, and a consistency engine reads 24 measurable parameters out of every document to catch conflicts before an assessor does.
Built for Microsoft estates and CMMC. Entra ID SSO, Conditional Access and PIM apply from day one. CMMC Level 2 ships with NIST SP 800-171A assessment objectives and official SPRS scoring, which matters more than a trust page to a defense supplier.
Side by side: SECORA vs Vanta
| Capability | SECORA | Vanta |
|---|---|---|
| Where your data lives | Your Microsoft 365 tenant or SharePoint Server | Vanta cloud (AWS, US default; Frankfurt on request) |
| Pricing model | One-time deployment per organisation, optional maintenance from year two | Per framework + headcount bands + add-ons; median $20,000 a year |
| Per-user or headcount fees | None | Yes, headcount bands |
| Adding a framework | Included; only extra controls appear | Additional cost, 15 to 30% more mid-contract |
| Annual price escalator | None on the platform | 5 to 10% reported |
| Sign-in | Entra ID with your Conditional Access and PIM | Vanta accounts or SSO |
| AI processing of evidence | No | Yes (AI agents, 2026) |
| CMMC: 800-171A objectives and SPRS scoring | Yes, official 5/3/1 scoring | CMMC framework available; SPRS calculation varies |
| Integrations | Microsoft 365, Entra, Sentinel, Azure, AWS, Google, GitHub, SIEMs via headless collector | 400 plus native integrations |
| Public trust centre | Not included (board report PDF instead) | Yes, add-on |
| Multi-client edition | Yes, row-level client isolation for MSPs and consultancies | Partner programme |
| New vendor in your risk register | No | Yes |
| Exit | Nothing to export; the lists are yours | Export and lose history |
Choose SECORA if you run on Microsoft 365, need CMMC, ISO 27001, SOC 2 or NIS2 without a new SaaS vendor, and want one price for unlimited users. Choose Vanta if you are a cloud-native startup that needs a public trust centre and hundreds of SaaS integrations this quarter.
Both remove spreadsheets. Only one keeps the evidence at home.
Three-year cost: Vanta against SECORA
Take the Vanta figure that matches your quote, set your headcount and frameworks, and the GRC cost calculator models three years of subscription with the usual renewal uplift against a one-time SECORA deployment plus optional maintenance. In the brochure scenario (one-time deployment at 1.2× the first-year subscription, 15% maintenance renewal from year two, 8% SaaS uplift with seat growth) the three-year total is roughly half. Your quote depends on scope, frameworks and estate size.
Moving from Vanta to SECORA
- Export from Vanta: controls with status, policies (PDF or DOCX), risk register CSV, vendor list and evidence files. Vanta allows export; history and audit trail stay in Vanta.
- Discovery workshop with ITSECOPS: frameworks, departments, estate inventory and branding. Your Vanta control statuses are mapped to the SECORA control library.
- Deploy in your tenant: signed package to the App Catalog, lists provisioned, roles applied.
- Seed and migrate: frameworks and policy library seeded; inventory imported by CSV; existing evidence re-uploaded into the versioned library and mapped once to every framework.
- Hand-over: owner onboarding, compliance calendar generated, first board report. Typical timeline is weeks, not quarters.
How SECORA works in your tenant
SECORA is a signed SharePoint Framework (SPFx) package. ITSECOPS uploads it to your Microsoft 365 App Catalog (or a SharePoint Server you host), provisions a Compliance site with the GRC lists and an evidence library, applies permissions and seeds your frameworks. From then on your team signs in with Entra ID, under your MFA and Conditional Access, and every control, policy, risk, task and piece of evidence is a SharePoint record in your own Microsoft geography.
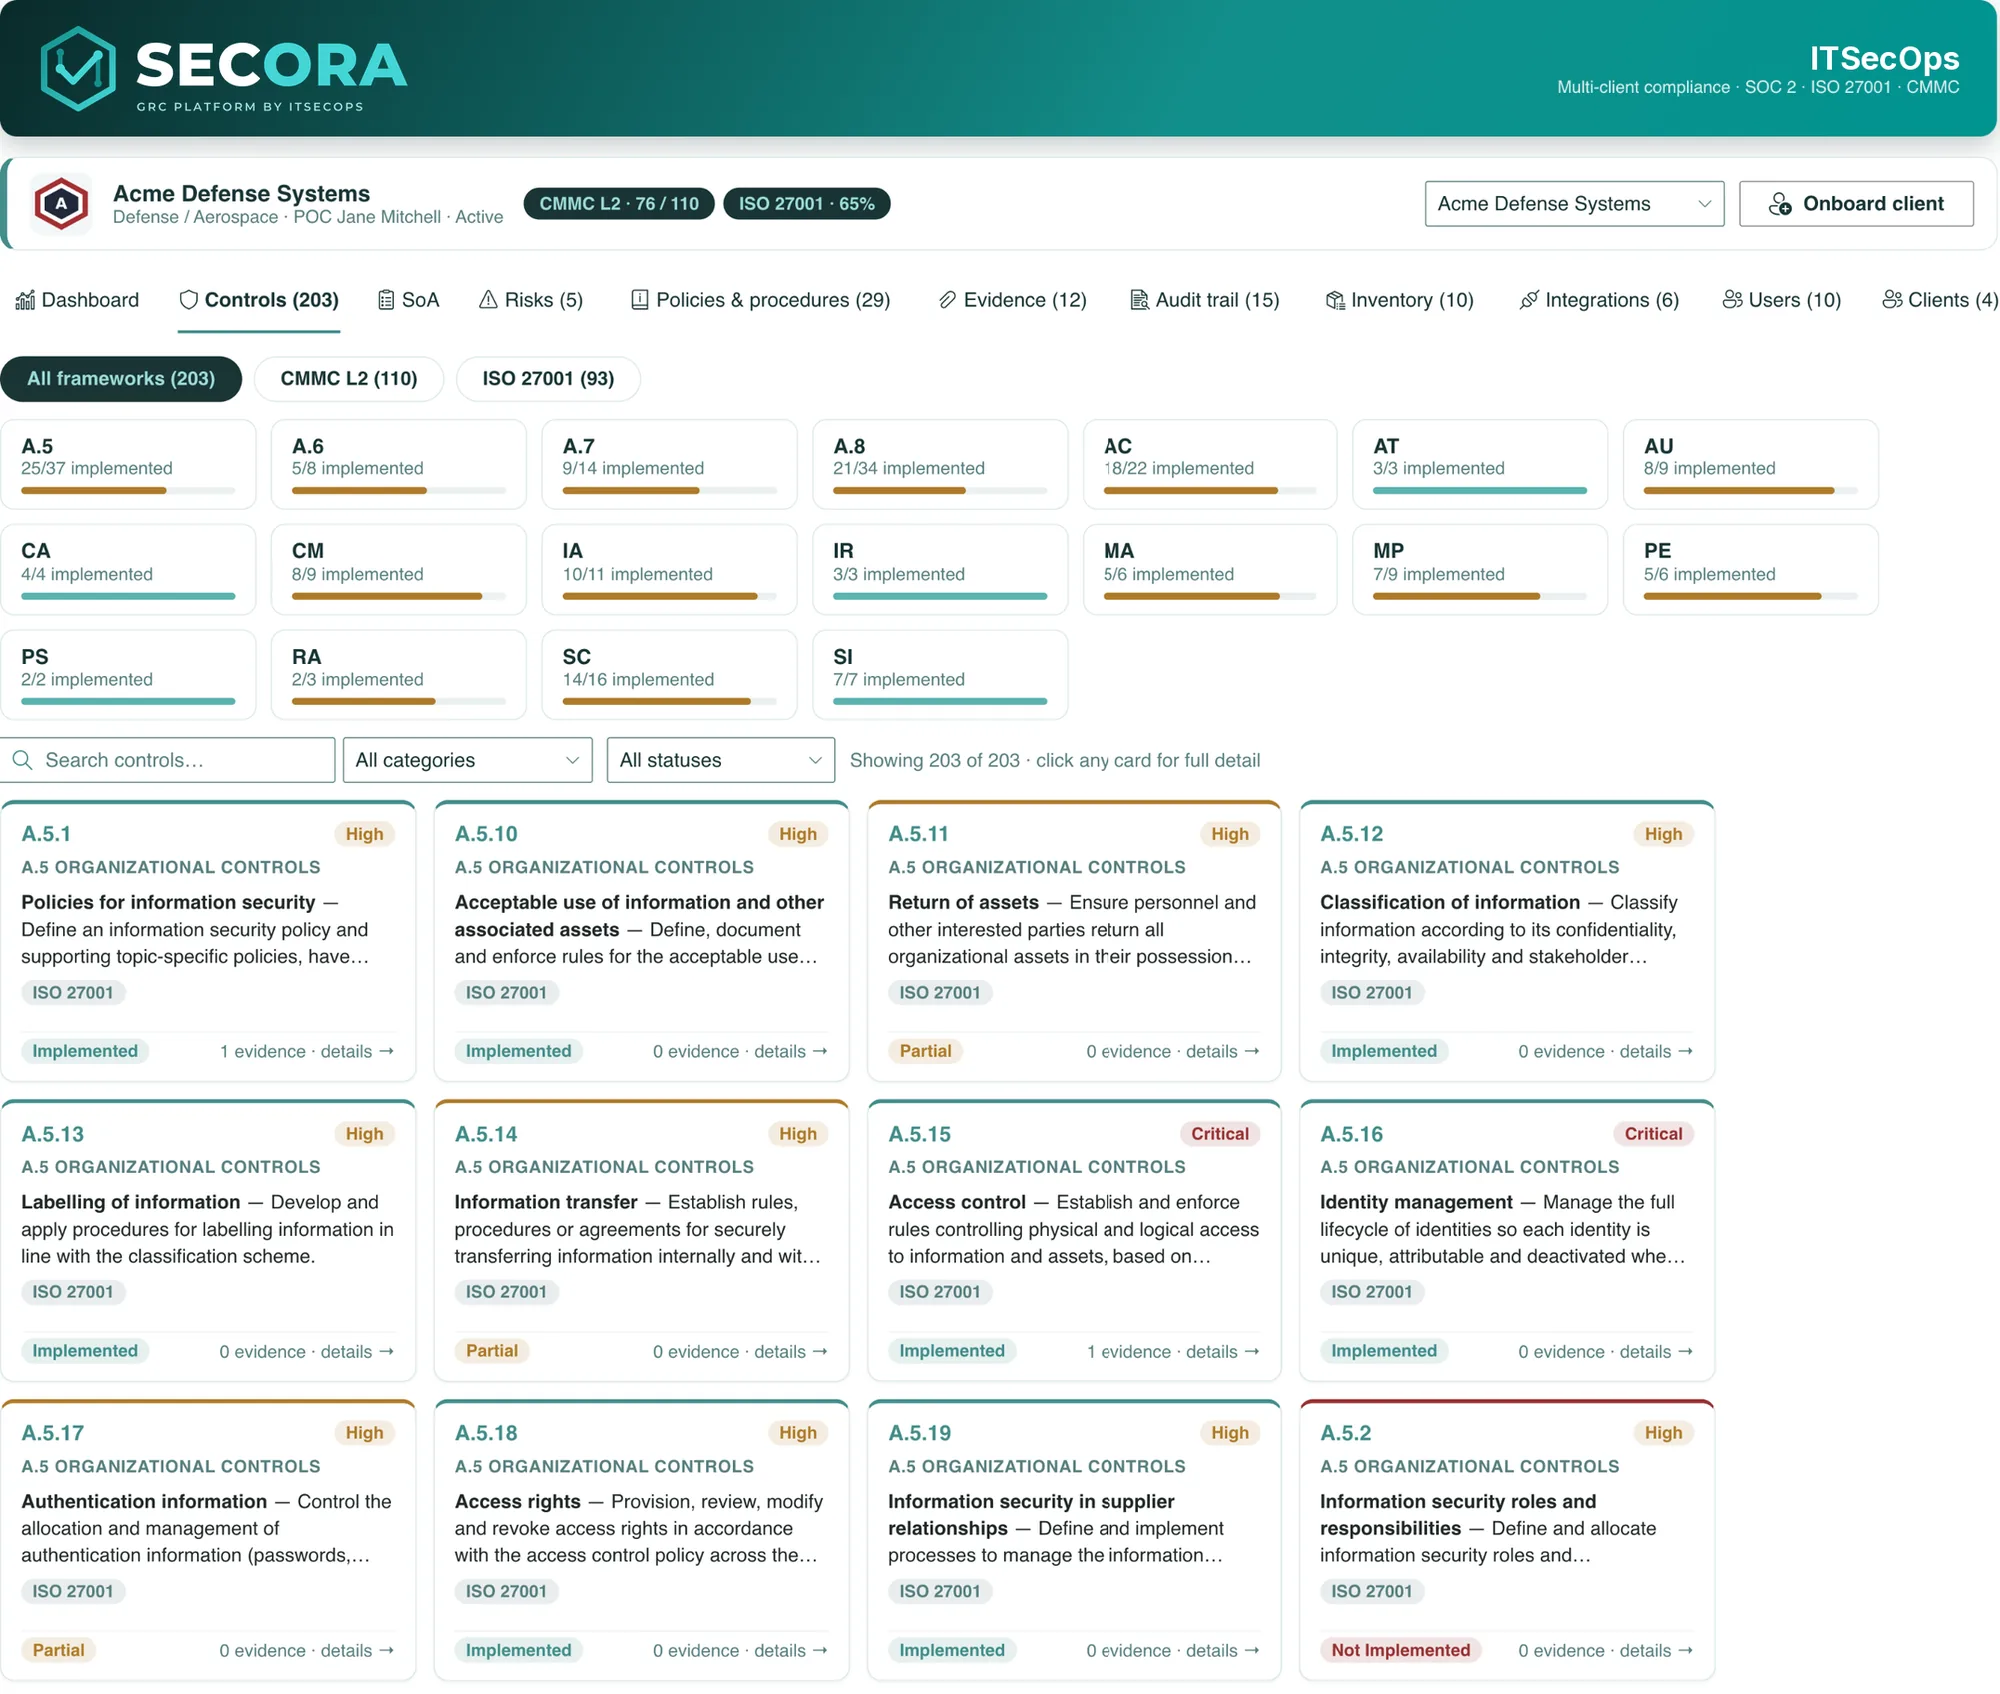
- Controls with family roll-ups, owners, priorities, SPRS weights, linked policies and evidence counts, mapped across every framework you select.
- Policies and procedures generated from 29 client-neutral templates, merged with your scoping answers, approved by email and exported as client-branded PDFs.
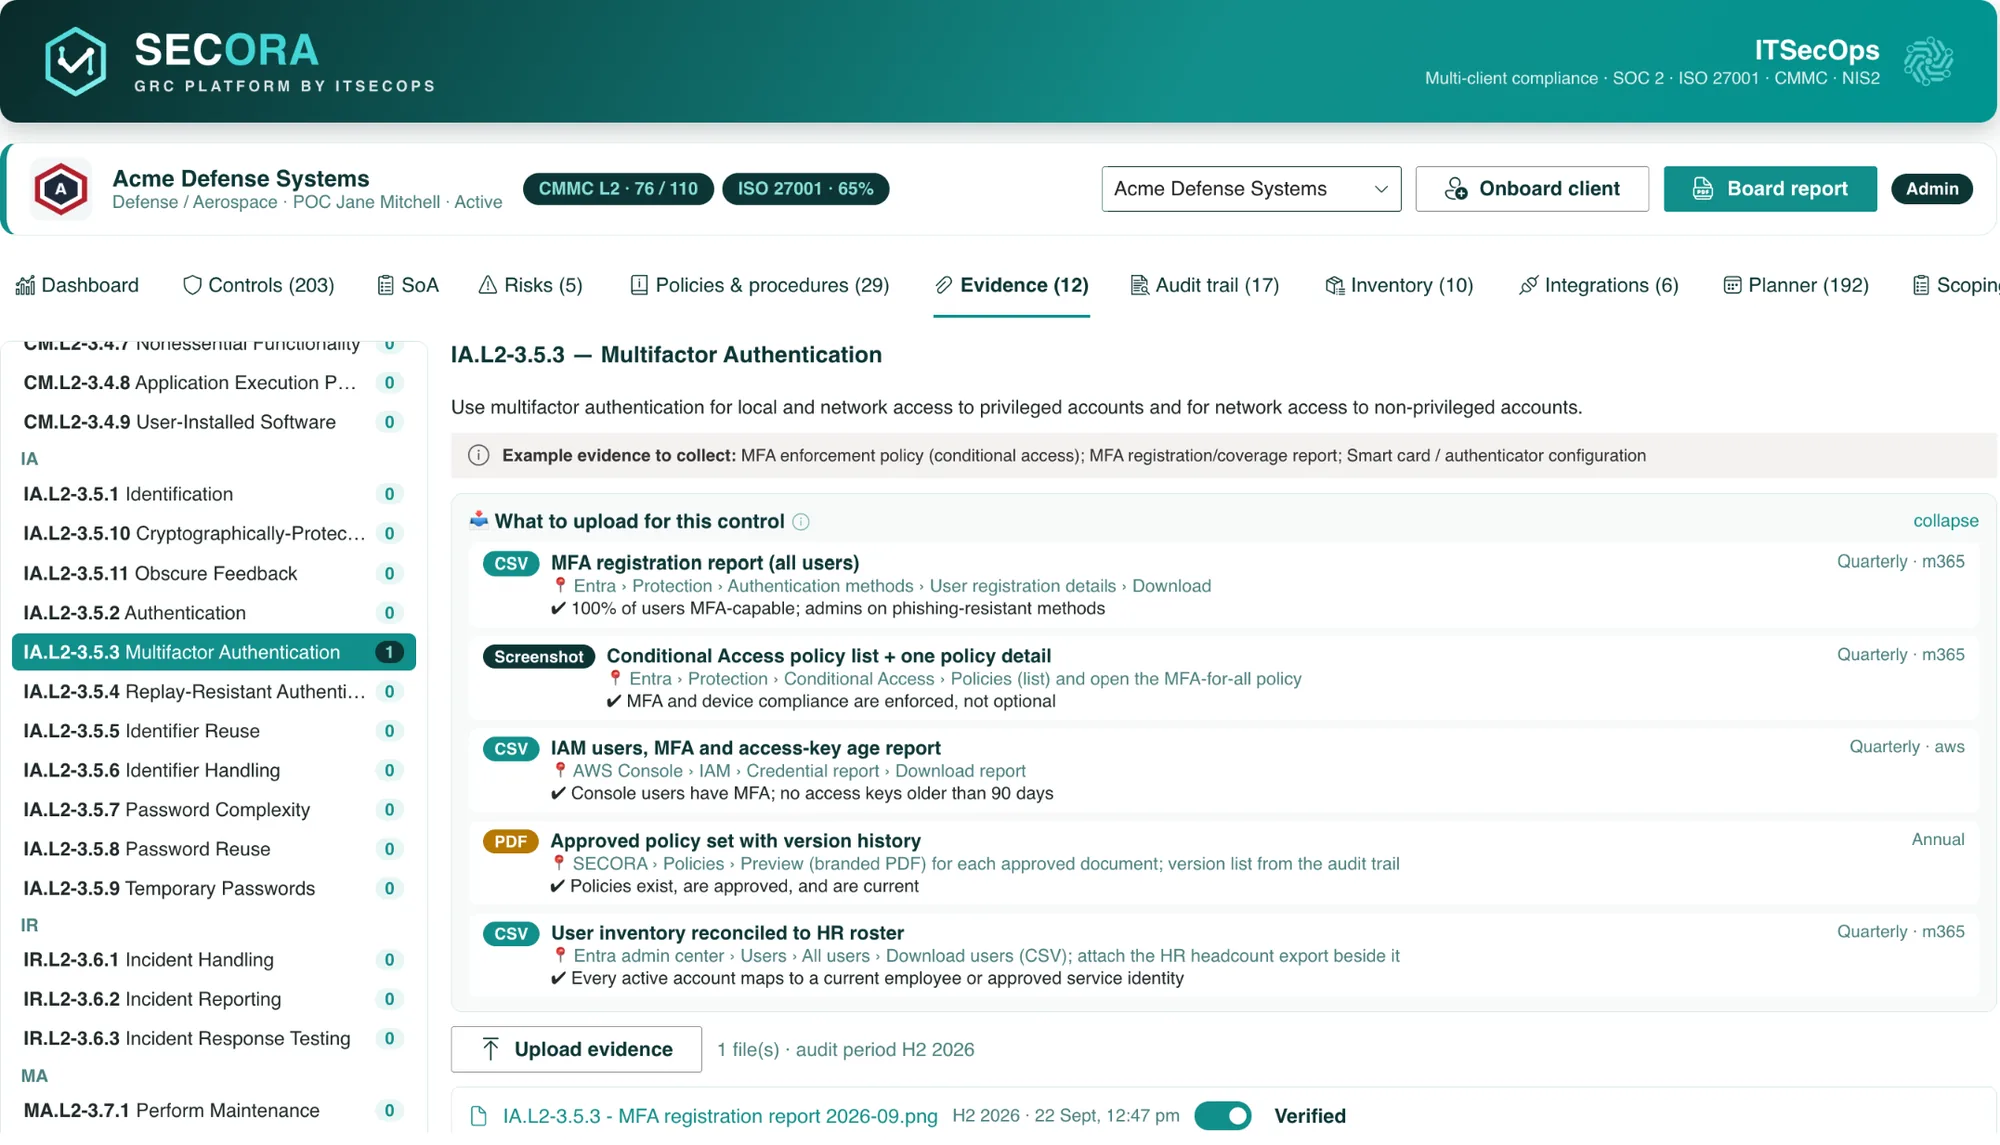
- Evidence library with a freshness clock per file, 55 evidence recipes that tell owners the exact report and menu path, and automated evidence from Microsoft 365, Entra ID and Sentinel.
- Risk register with a 5×5 heatmap, mitigation tracking and control mapping.
- Compliance calendar that turns 45 recurring duties into dated tasks with owners and reminders sent through Microsoft Graph.
- Scoping questionnaire, consistency check, roadmap, inventory, append-only audit trail and one-click board report.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Sources: Vendr: Vanta pricing data · SiliconANGLE: Vanta AI agents, Mar 2026 · Orbiq: Vanta vs Drata hosting · ComplyJet: Vanta reviews. Competitor figures are observed contract data or published estimates, not list prices; verify with the vendor.
Frequently asked
Yes. SECORA seeds the SOC 2 Trust Services Criteria (CC1 to CC9, A1, C1, PI1) with an observation-window roadmap, continuous checks for your Microsoft estate and an evidence library with a freshness clock. The difference is architecture: SECORA runs in your tenant and is licensed once per organisation.
No. Vanta lists 400 plus native integrations. SECORA covers Microsoft 365, Entra ID and Sentinel natively, plus Azure, AWS, Google Cloud and Workspace, GitHub, Wazuh, Splunk and Elastic through a headless collector, with manual evidence recipes for everything else. For Microsoft-centric organisations this covers the evidence an assessor actually samples.
Observed contracts range from $7,500 to $57,221 a year with a $20,000 median (Vendr, February 2026). Single-framework SMB deals typically land between $12,000 and $28,000, before audit fees of $8,000 to $40,000 and add-ons.
In your own Microsoft 365 tenant or SharePoint Server: SharePoint lists for controls, policies, risks, tasks, inventory and the audit trail, and a versioned document library for evidence. SECORA has no cloud of its own and no vendor database.
No. SECORA is licensed per organisation with a one-time deployment fee and twelve months of maintenance included. Invite every control owner, department head and external auditor without changing the bill.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.