SECORA · GRC platform by ITSECOPS · Product overview 2026

Compliance.
Finally at home.

SECORA is the multi-framework GRC platform that runs inside your own Microsoft 365 tenant. CMMC, ISO 27001, SOC 2, NIS2, HIPAA, GDPR and NIST CSF in one portal: your SharePoint, your Entra ID sign-in, your data. No third-party SaaS. No per-user fees. Nothing forgotten.

Runs in Microsoft 365 or SharePoint Server Entra ID SSO, MFA, Conditional Access One-time deployment, 12 months of care included 0 per-user licences, ever
acme.sharepoint.com/sites/Compliance · SECORA
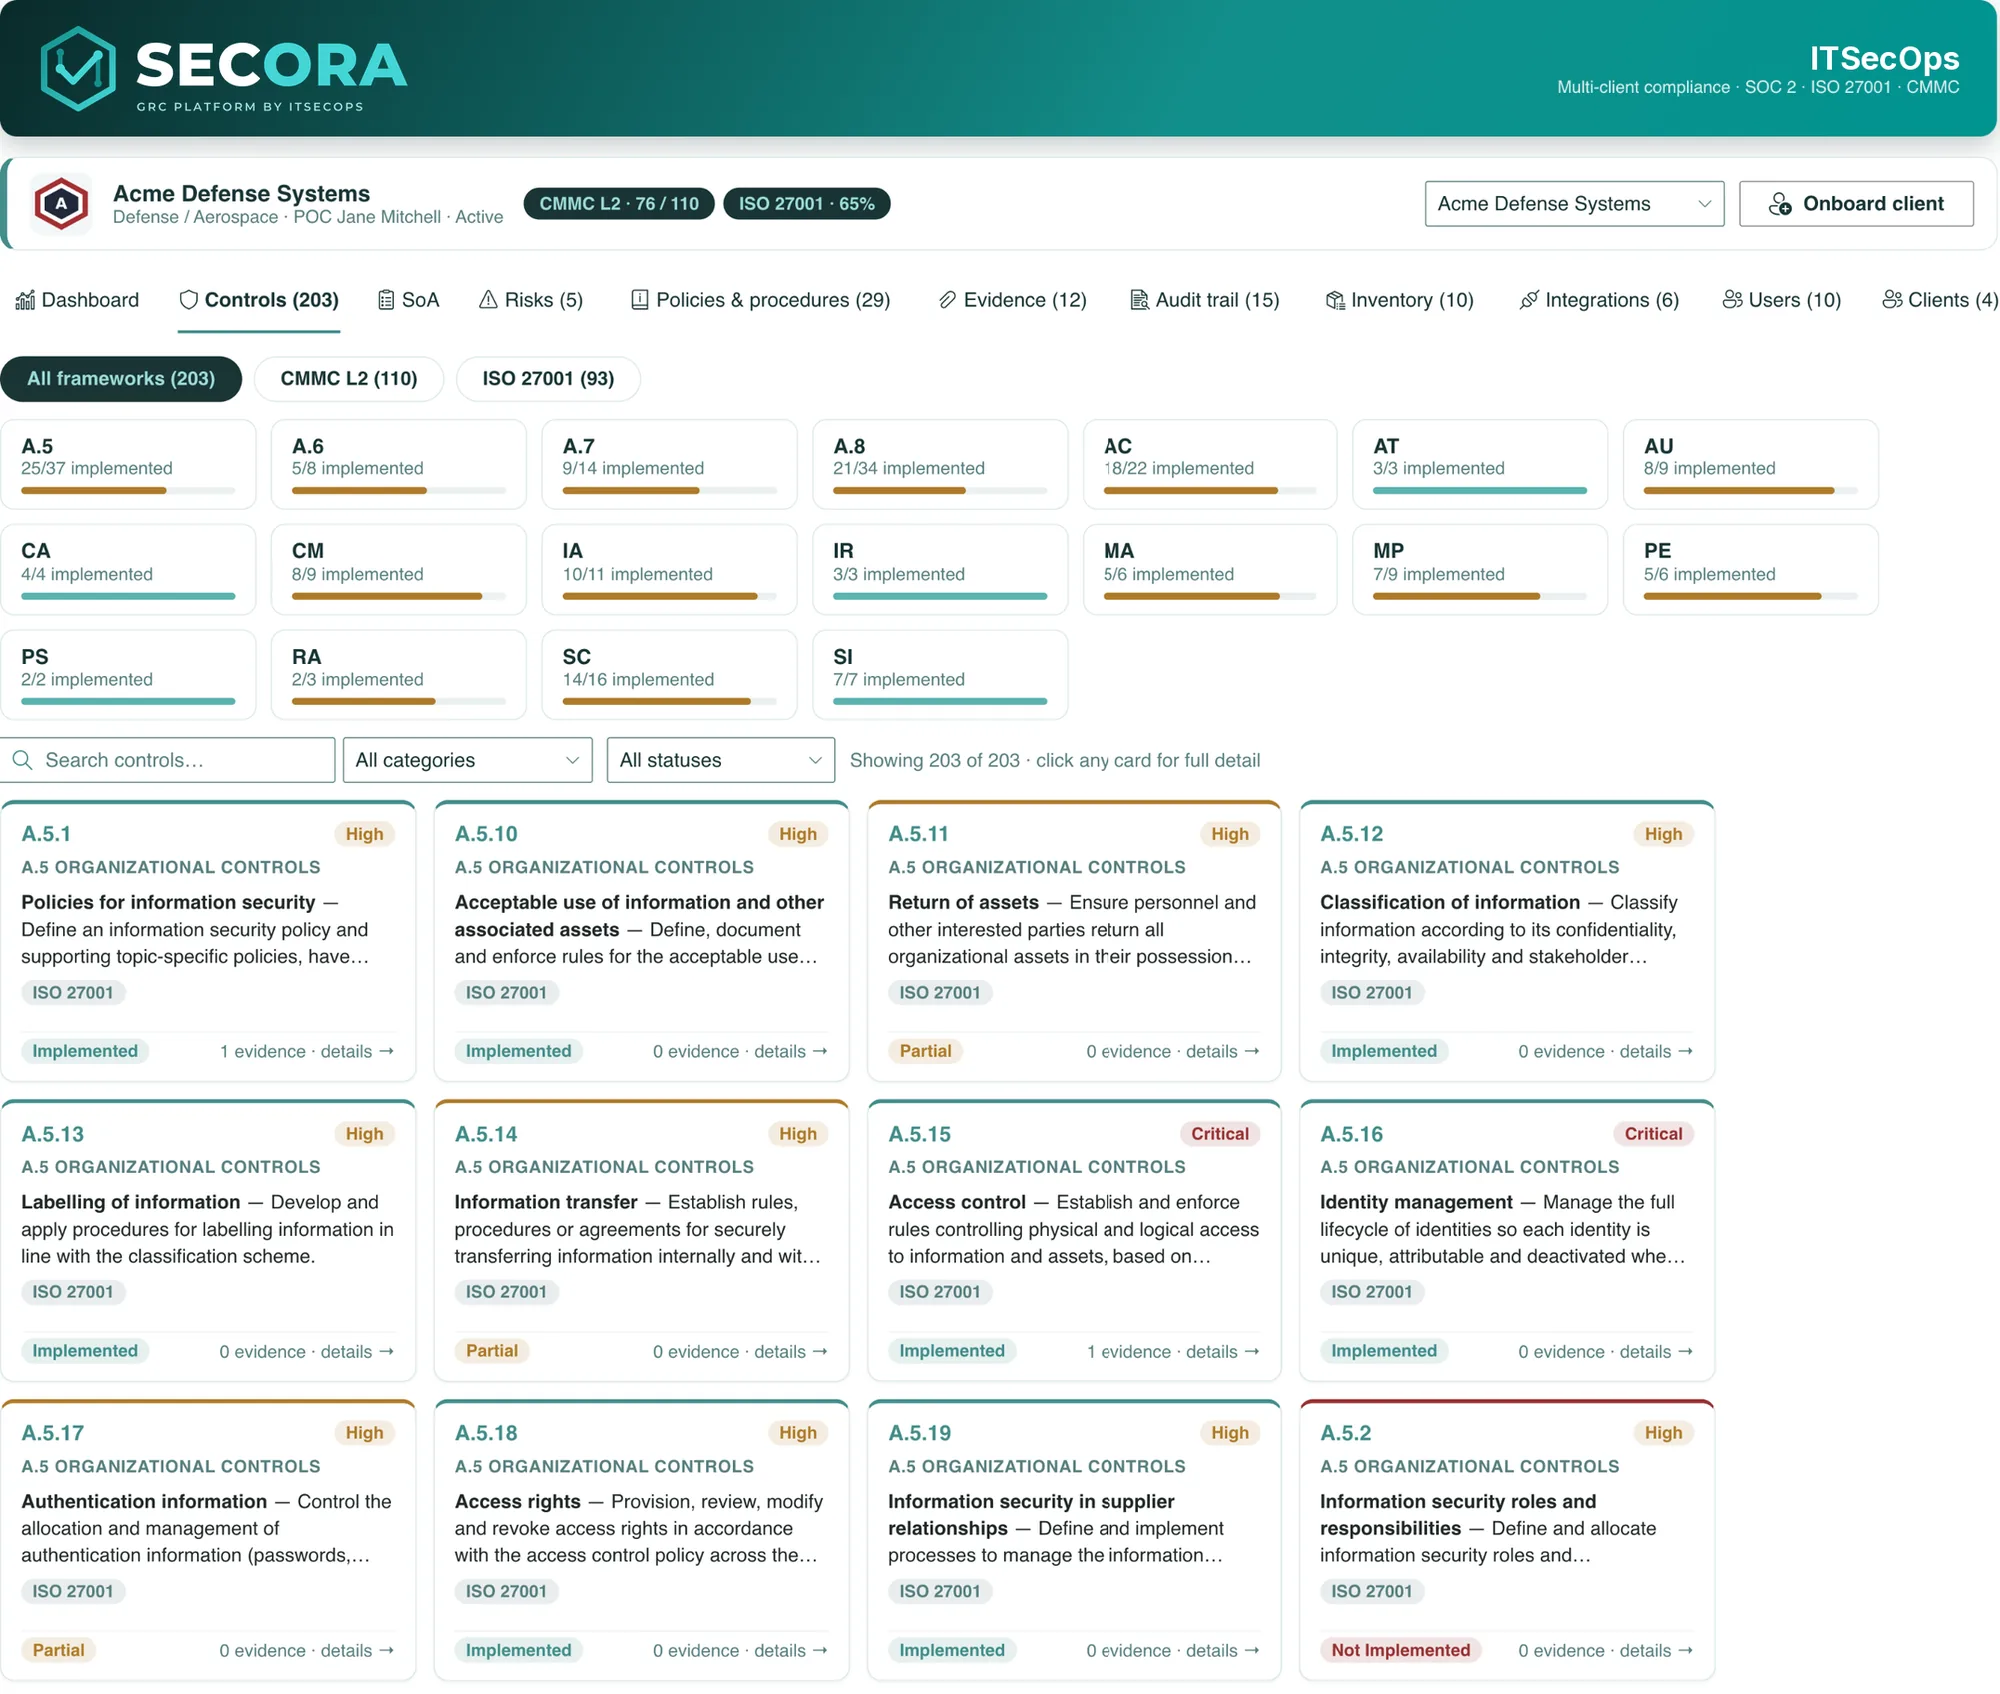
SECORA controls view: 203 controls across CMMC Level 2 and ISO 27001 with family roll-ups and control cards
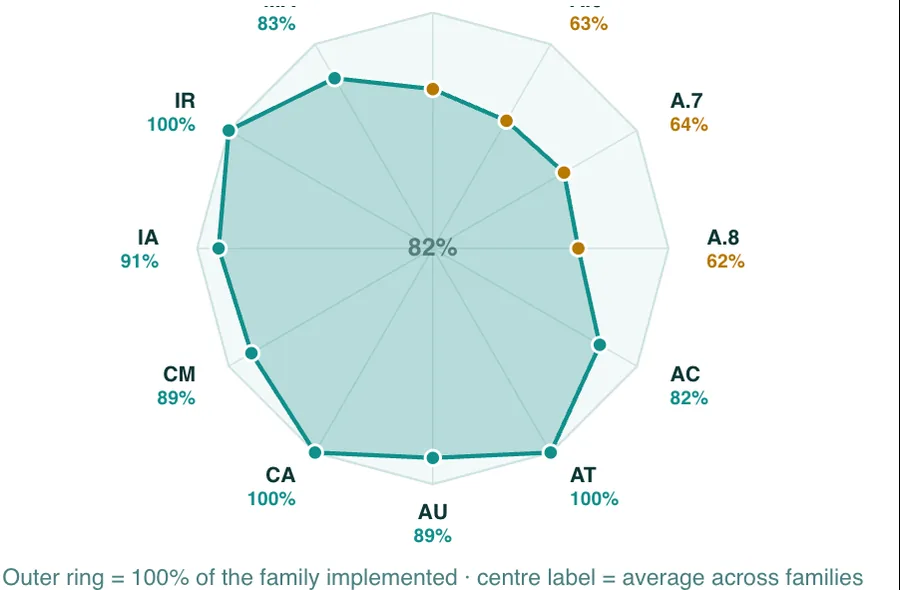
Control family coverage spider chart
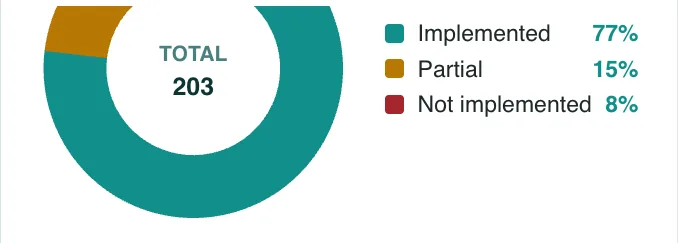
Implementation status donut: 77 percent implemented
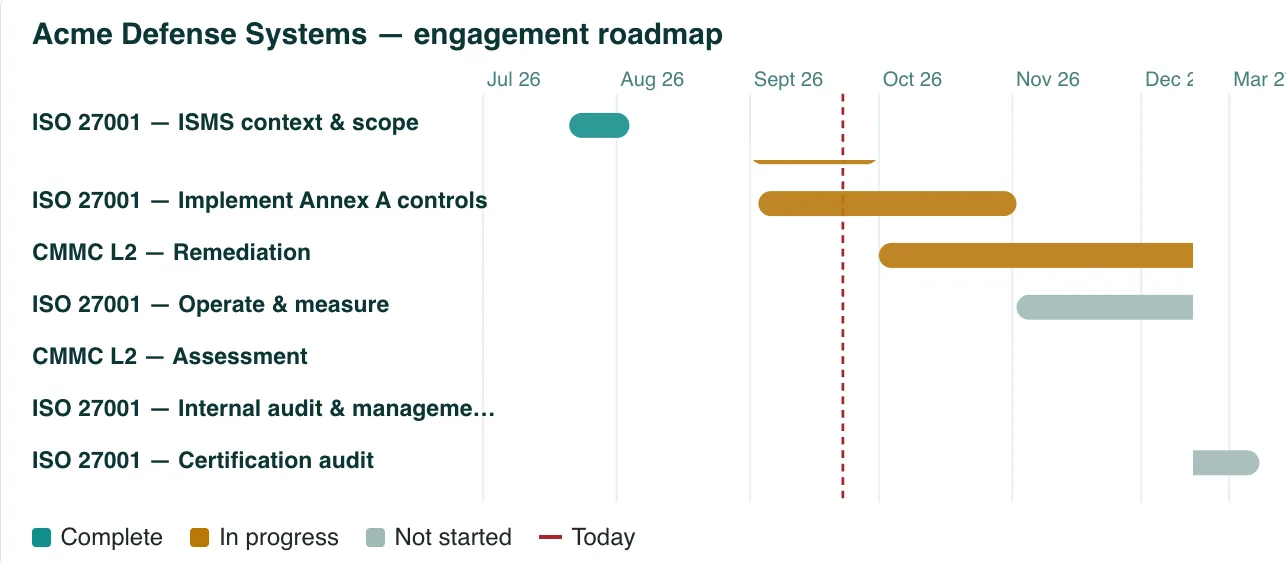
Engagement roadmap Gantt for ISO 27001 and CMMC Level 2
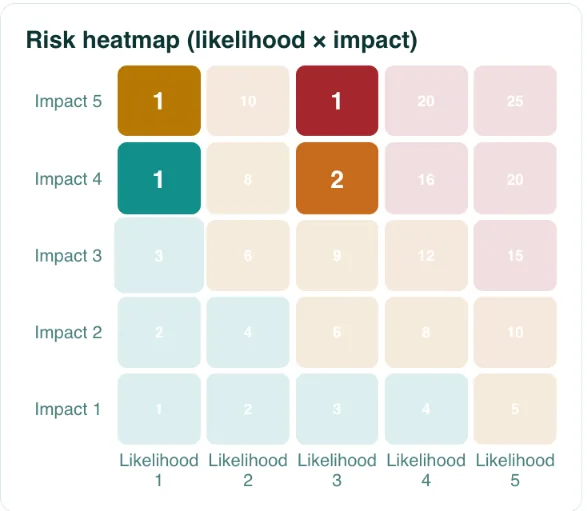
Risk heatmap, likelihood by impact

Why SECORA

Your tenant.Your data.Your rules.

Most organisations already know what CMMC, ISO 27001 or SOC 2 ask of them. What slows them down is the machinery: spreadsheets nobody trusts, evidence scattered across mailboxes, and SaaS tools that charge per seat while quietly becoming another vendor in the risk register. SECORA removes the machinery problem without adding a vendor.

Hosted where you already are

Deployed as a signed SharePoint Framework package into your Microsoft 365 tenant, or onto a SharePoint Server you run. Microsoft's own encryption, backup, retention labels, eDiscovery and DLP apply to every record.

Sign in with Microsoft. That's it.

Entra ID single sign-on. Whatever you enforce today, MFA, phishing-resistant authenticators, Conditional Access, device compliance, PIM for admins, protects SECORA on day one.

Say no to spreadsheets and AI black boxes

Every change is an auditable list transaction with an owner, a timestamp and an append-only trail. No evidence is shipped to a third-party AI service to be "auto-mapped". Mapping is explicit, reviewable and yours.

Why now · September 2026

Every SaaS GRC tool is one more OAuth grant into your Microsoft 365 and cloud. SECORA adds none.

Third-party involvement in breaches doubled in 2025, and 2026 has already produced a third SaaS OAuth supply-chain incident in twelve months. Compliance tooling that holds your policies, evidence and risk register is exactly the kind of vendor a regulator, an assessor or a board will ask about. SECORA has no cloud of its own, so there is nothing to ask about.

JUN 2026 · KLUE OAUTH BREACH

195 organisations, including a GRC vendor, lost Salesforce data through stolen OAuth tokens

A dormant 2022 test credential at Klue let attackers pull data from OneTrust, Huntress, Tanium and others, the third such incident after Salesloft Drift and Gainsight. CSA research note

JUL 2026 · CMMC PHASE 2 SUSPENDED

C3PAO assessments paused for review, self-assessment, SPRS and NIST 800-171 still mandatory

About 80,000 defense suppliers still need the evidence to live somewhere, without signing a multi-year per-seat contract for a deadline that moved. What still applies

Platform tour

Everything. One place.

Controls, policies, procedures, evidence, risks, inventory, Statement of Applicability, roadmap, compliance calendar, scoping and audit trail. Every tile drills through to the underlying record, and the record lives in your SharePoint lists.

01 · DASHBOARD

See the whole programme in one glance

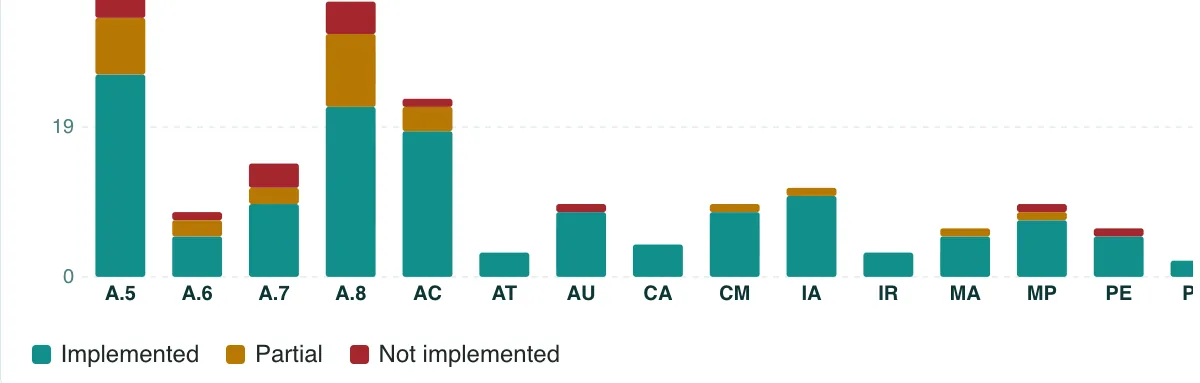
Readiness by framework, KPI tiles, multi-framework overlap, posture donuts and the control-family spider web. Every framework is scored the way its assessor scores it: SPRS points for CMMC, percentage of Annex A controls for ISO.

  • Framework cards with assessment-objective progress and the exact blocker, for example a missing SSP.
  • Spider-web coverage per control family (AC, IA, SC, A.5, A.8) so thin spots are visible at a glance.
  • Board report in one click: a four-page executive PDF, every export logged in the audit trail.

Dashboard · Acme Defense Systems
KPI tiles: pending tasks, due in 30 days, evidence freshness, inventory, compliance calendarMulti-framework overlap: 83 percent of the document workstream is shared
Implementation status per control familySpider web coverage chart
Engagement roadmap
02 · CONTROLS AND ASSESSMENT OBJECTIVES

Assess the way the assessor does

Every requirement is a control card with family, priority, SPRS weight, owner, linked policies, evidence count and status. Filters by framework, family and status keep 200 plus controls manageable.

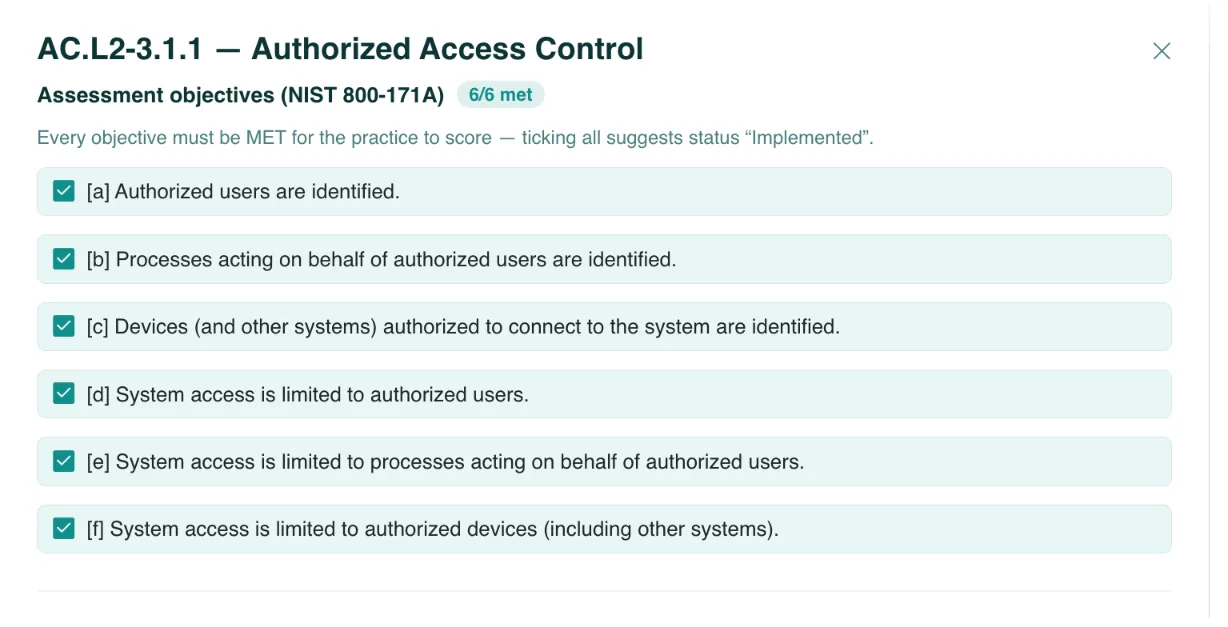
  • NIST SP 800-171A objectives per CMMC practice: tick [a] to [f] and the status suggests itself.
  • Official SPRS scoring (5, 3 and 1 point deductions, 3.12.4 handled correctly) so your number matches the DoD's.
  • Cross-framework reuse: one implemented control satisfies its ISO, SOC 2 and CMMC equivalents at once.
  • No silent edits: saving stamps the review date and writes the audit trail.
Controls · All frameworks (203)
Controls view with framework family roll-ups and control cards
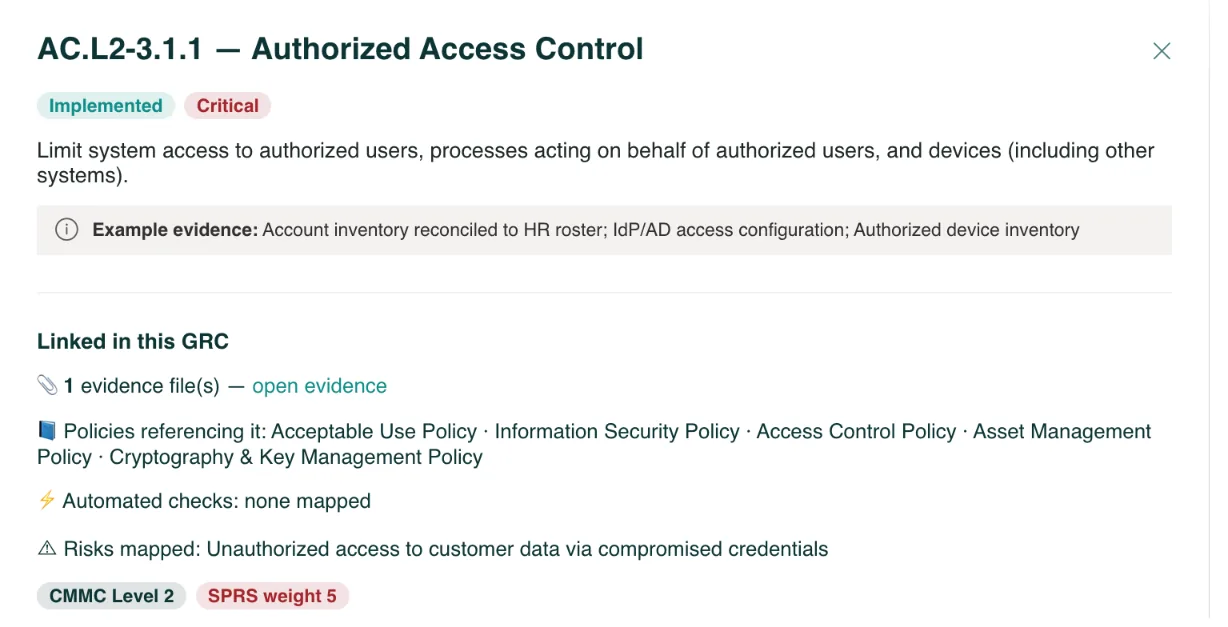
Assessment objectives for AC.L2-3.1.1, 6 of 6 met
03 · POLICIES, PROCEDURES AND THE SOA

Write once. Approve once. Branded PDF, every time.

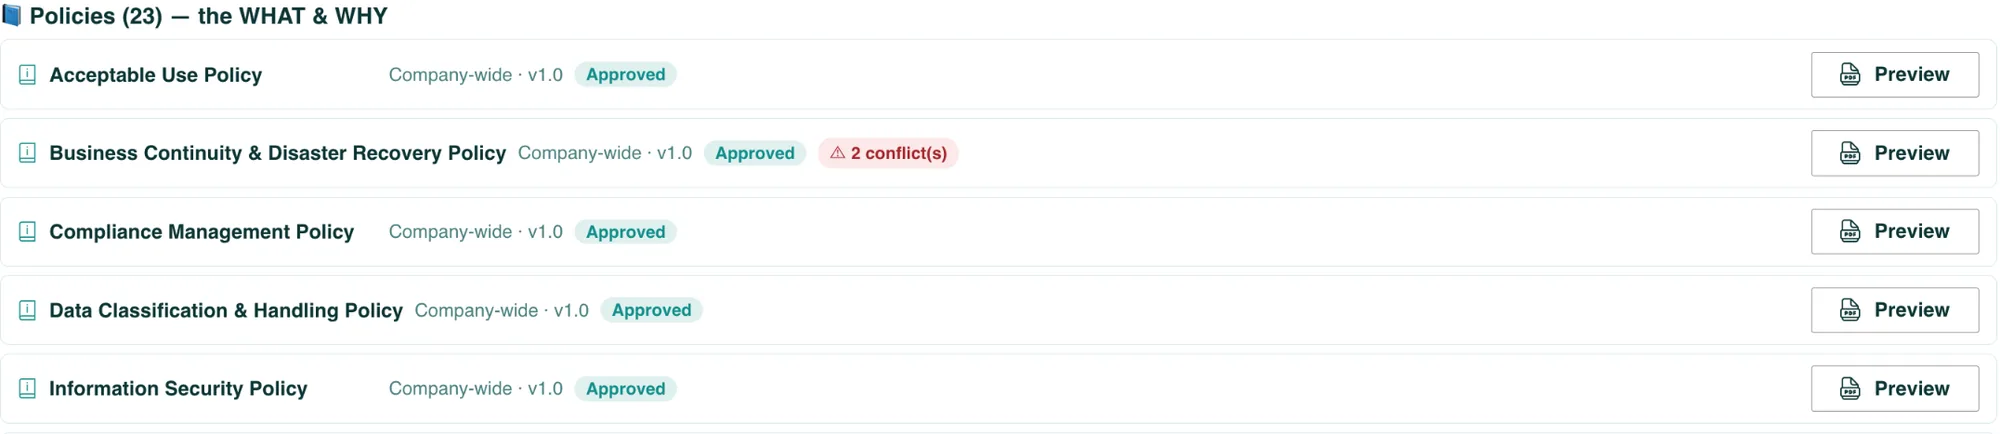
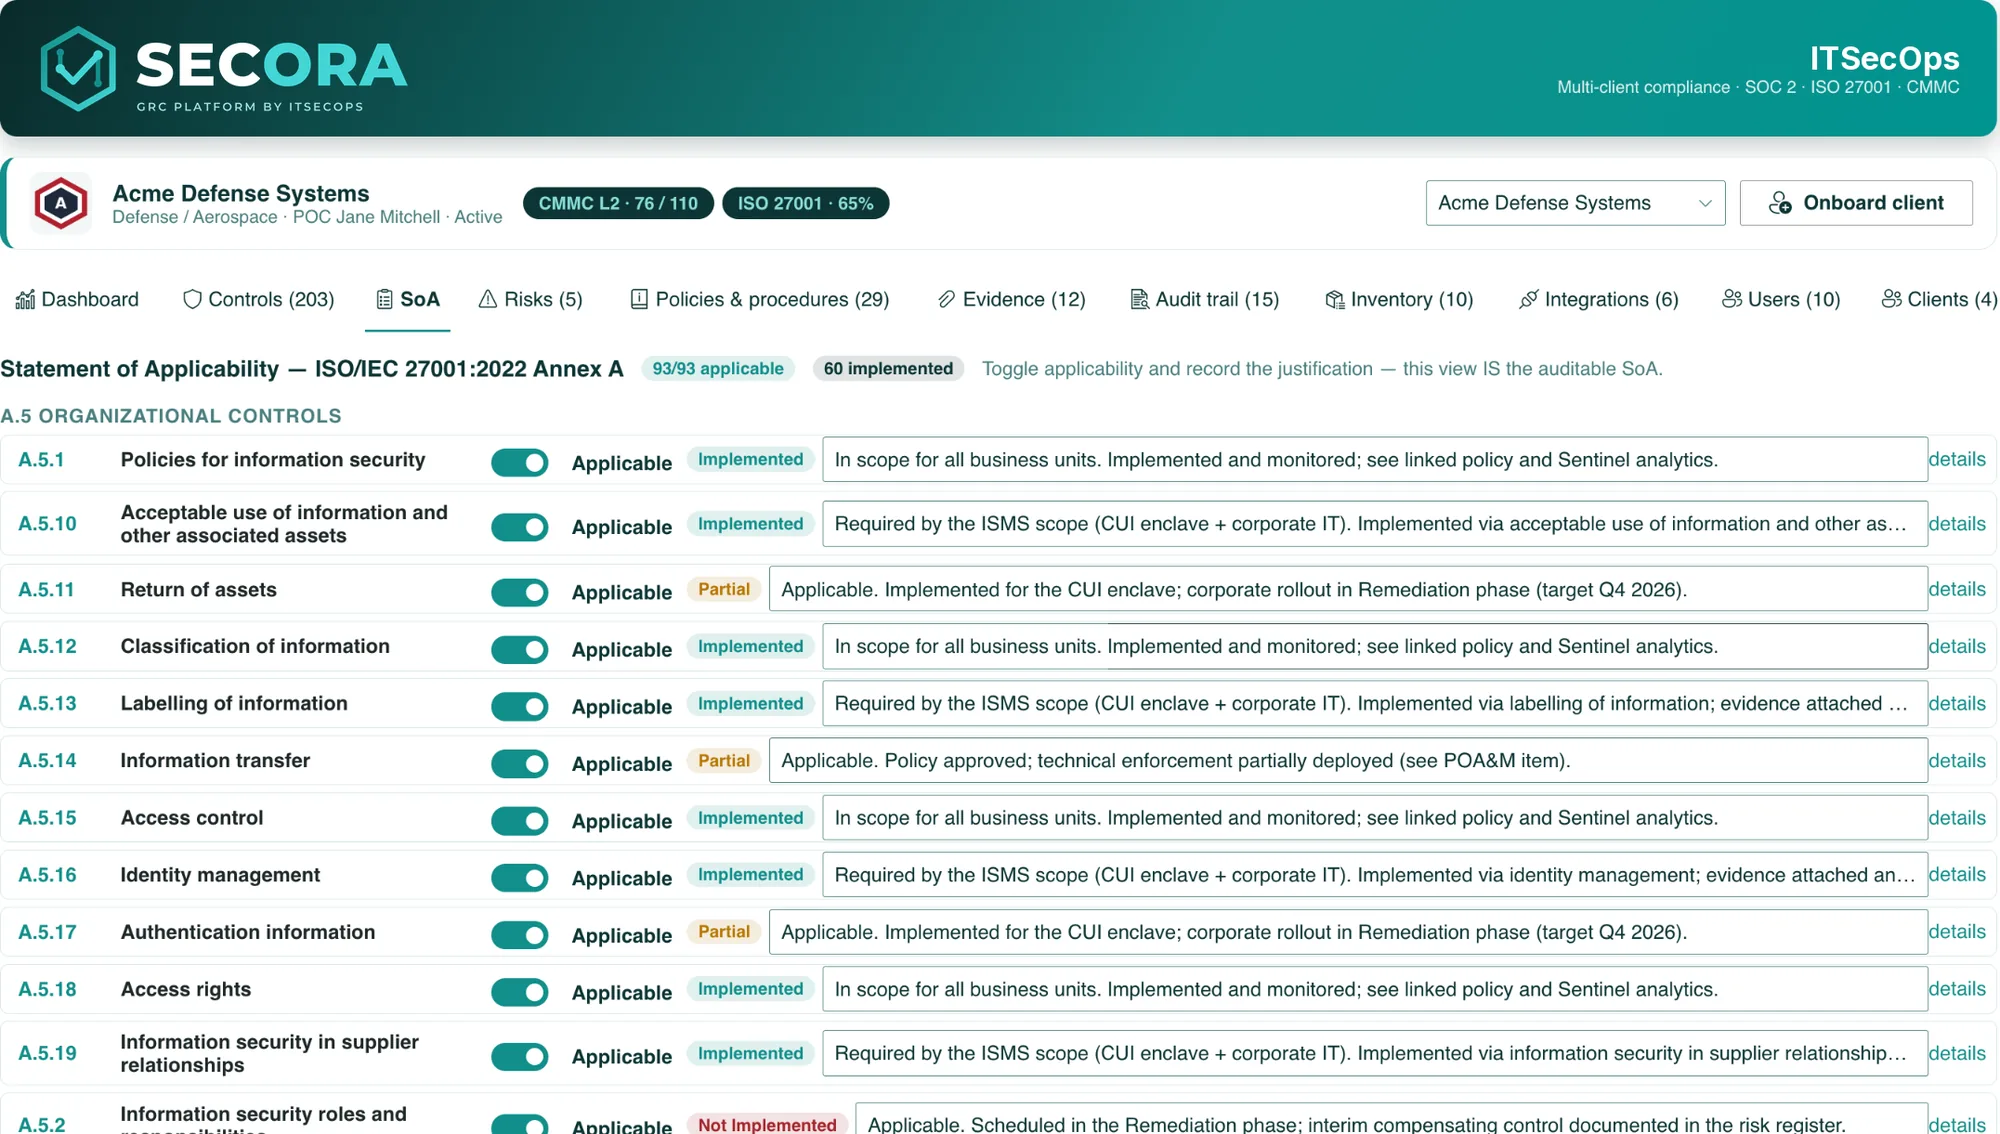
A department-wise structure, a generate-from-template library and an approval workflow that produces client-branded PDFs. For ISO clients the Statement of Applicability is a live view, not a spreadsheet export.

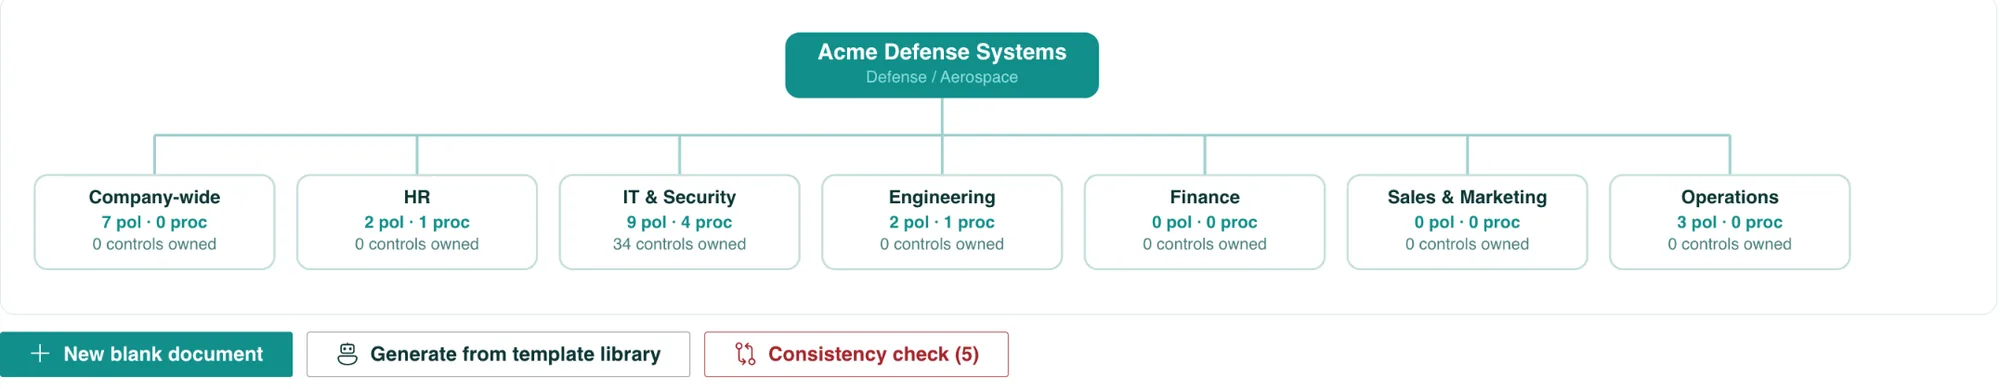
  • Org tree (Company-wide, HR, IT and Security, Engineering, Finance, Operations) filters documents and shows controls owned per department.
  • 29 client-neutral templates merged with your name, logo and tagline, plus estate-specific hardening SOPs generated from your inventory.
  • Write, preview, send, approve: the approver gets an email, the portal records who approved what, when, at which version.
Policies and procedures (29)
Approval queue: Incident Response Procedure and System Maintenance Policy awaiting approvalDepartment org tree with policies and procedures per departmentPolicies list with approval status
Statement of Applicability for ISO/IEC 27001:2022 Annex A
04 · RISKS AND EVIDENCE

Risk register and evidence, mapped to controls

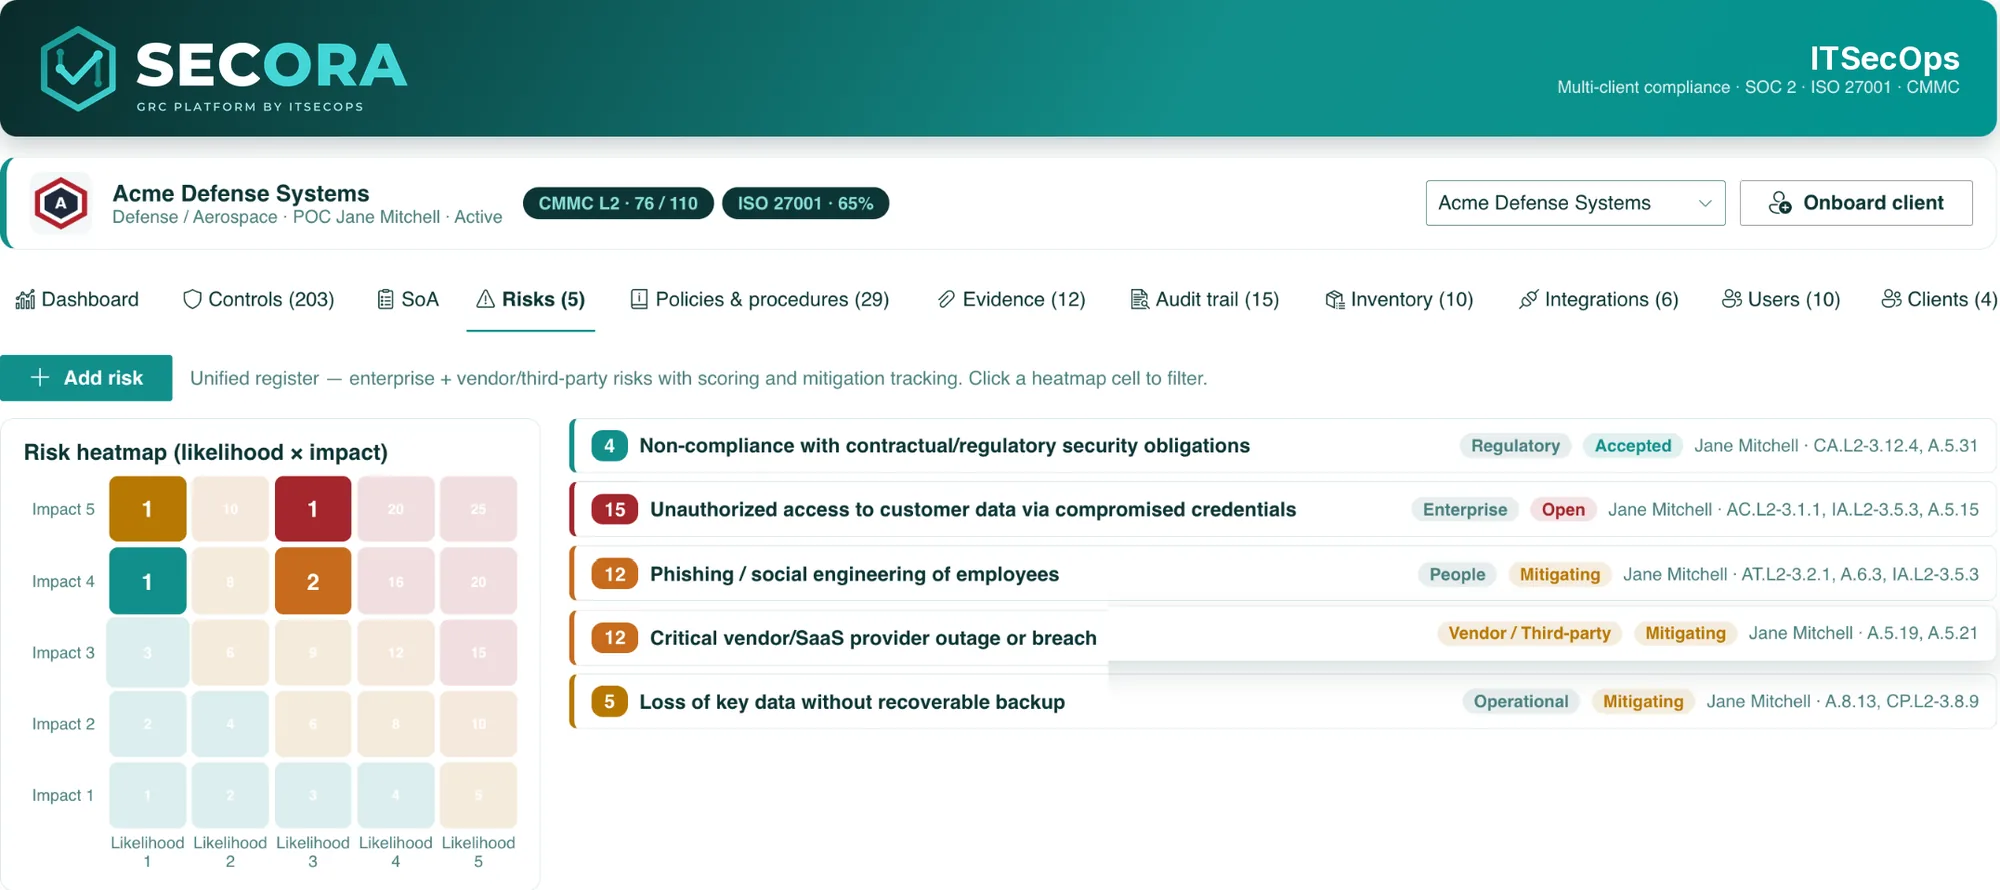
A unified register for enterprise, vendor and third-party risks with 5×5 scoring, mitigation tracking and control mapping. Evidence lives in a versioned document library with a freshness clock per file.

  • Clickable heatmap (likelihood × impact) that filters the register; high risks without a mitigation plan trip a continuous check.
  • Upload once, map to many: the same file satisfies every framework the control maps to.
  • Freshness clock: evidence older than 90 days flips the control amber on the dashboard, before an assessor notices.
  • Automated evidence from Microsoft 365, Entra ID and Sentinel lands in the same library with the same clock.
Risks (5) · Unified register
Risk register with heatmap and scored risks
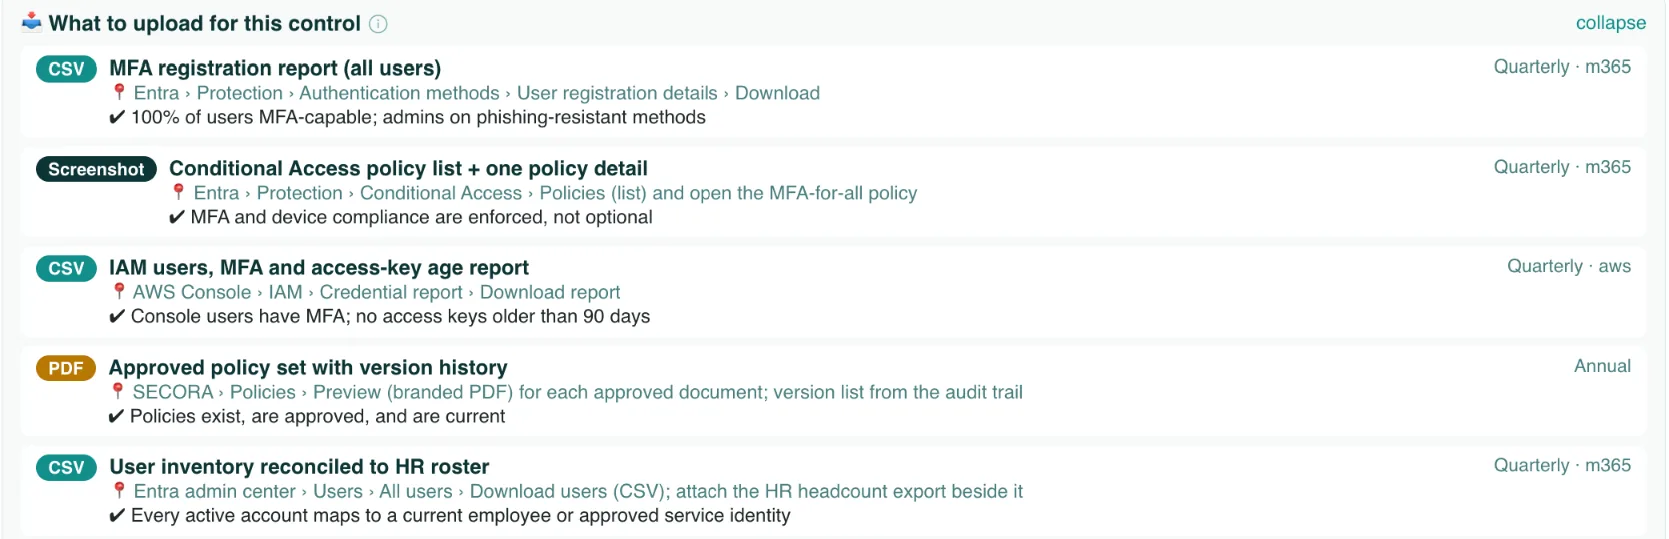
What to upload for this control: evidence recipes with exact menu paths
05 · COMPLIANCE CALENDAR

Nothing forgotten. What to do, when, by whom.

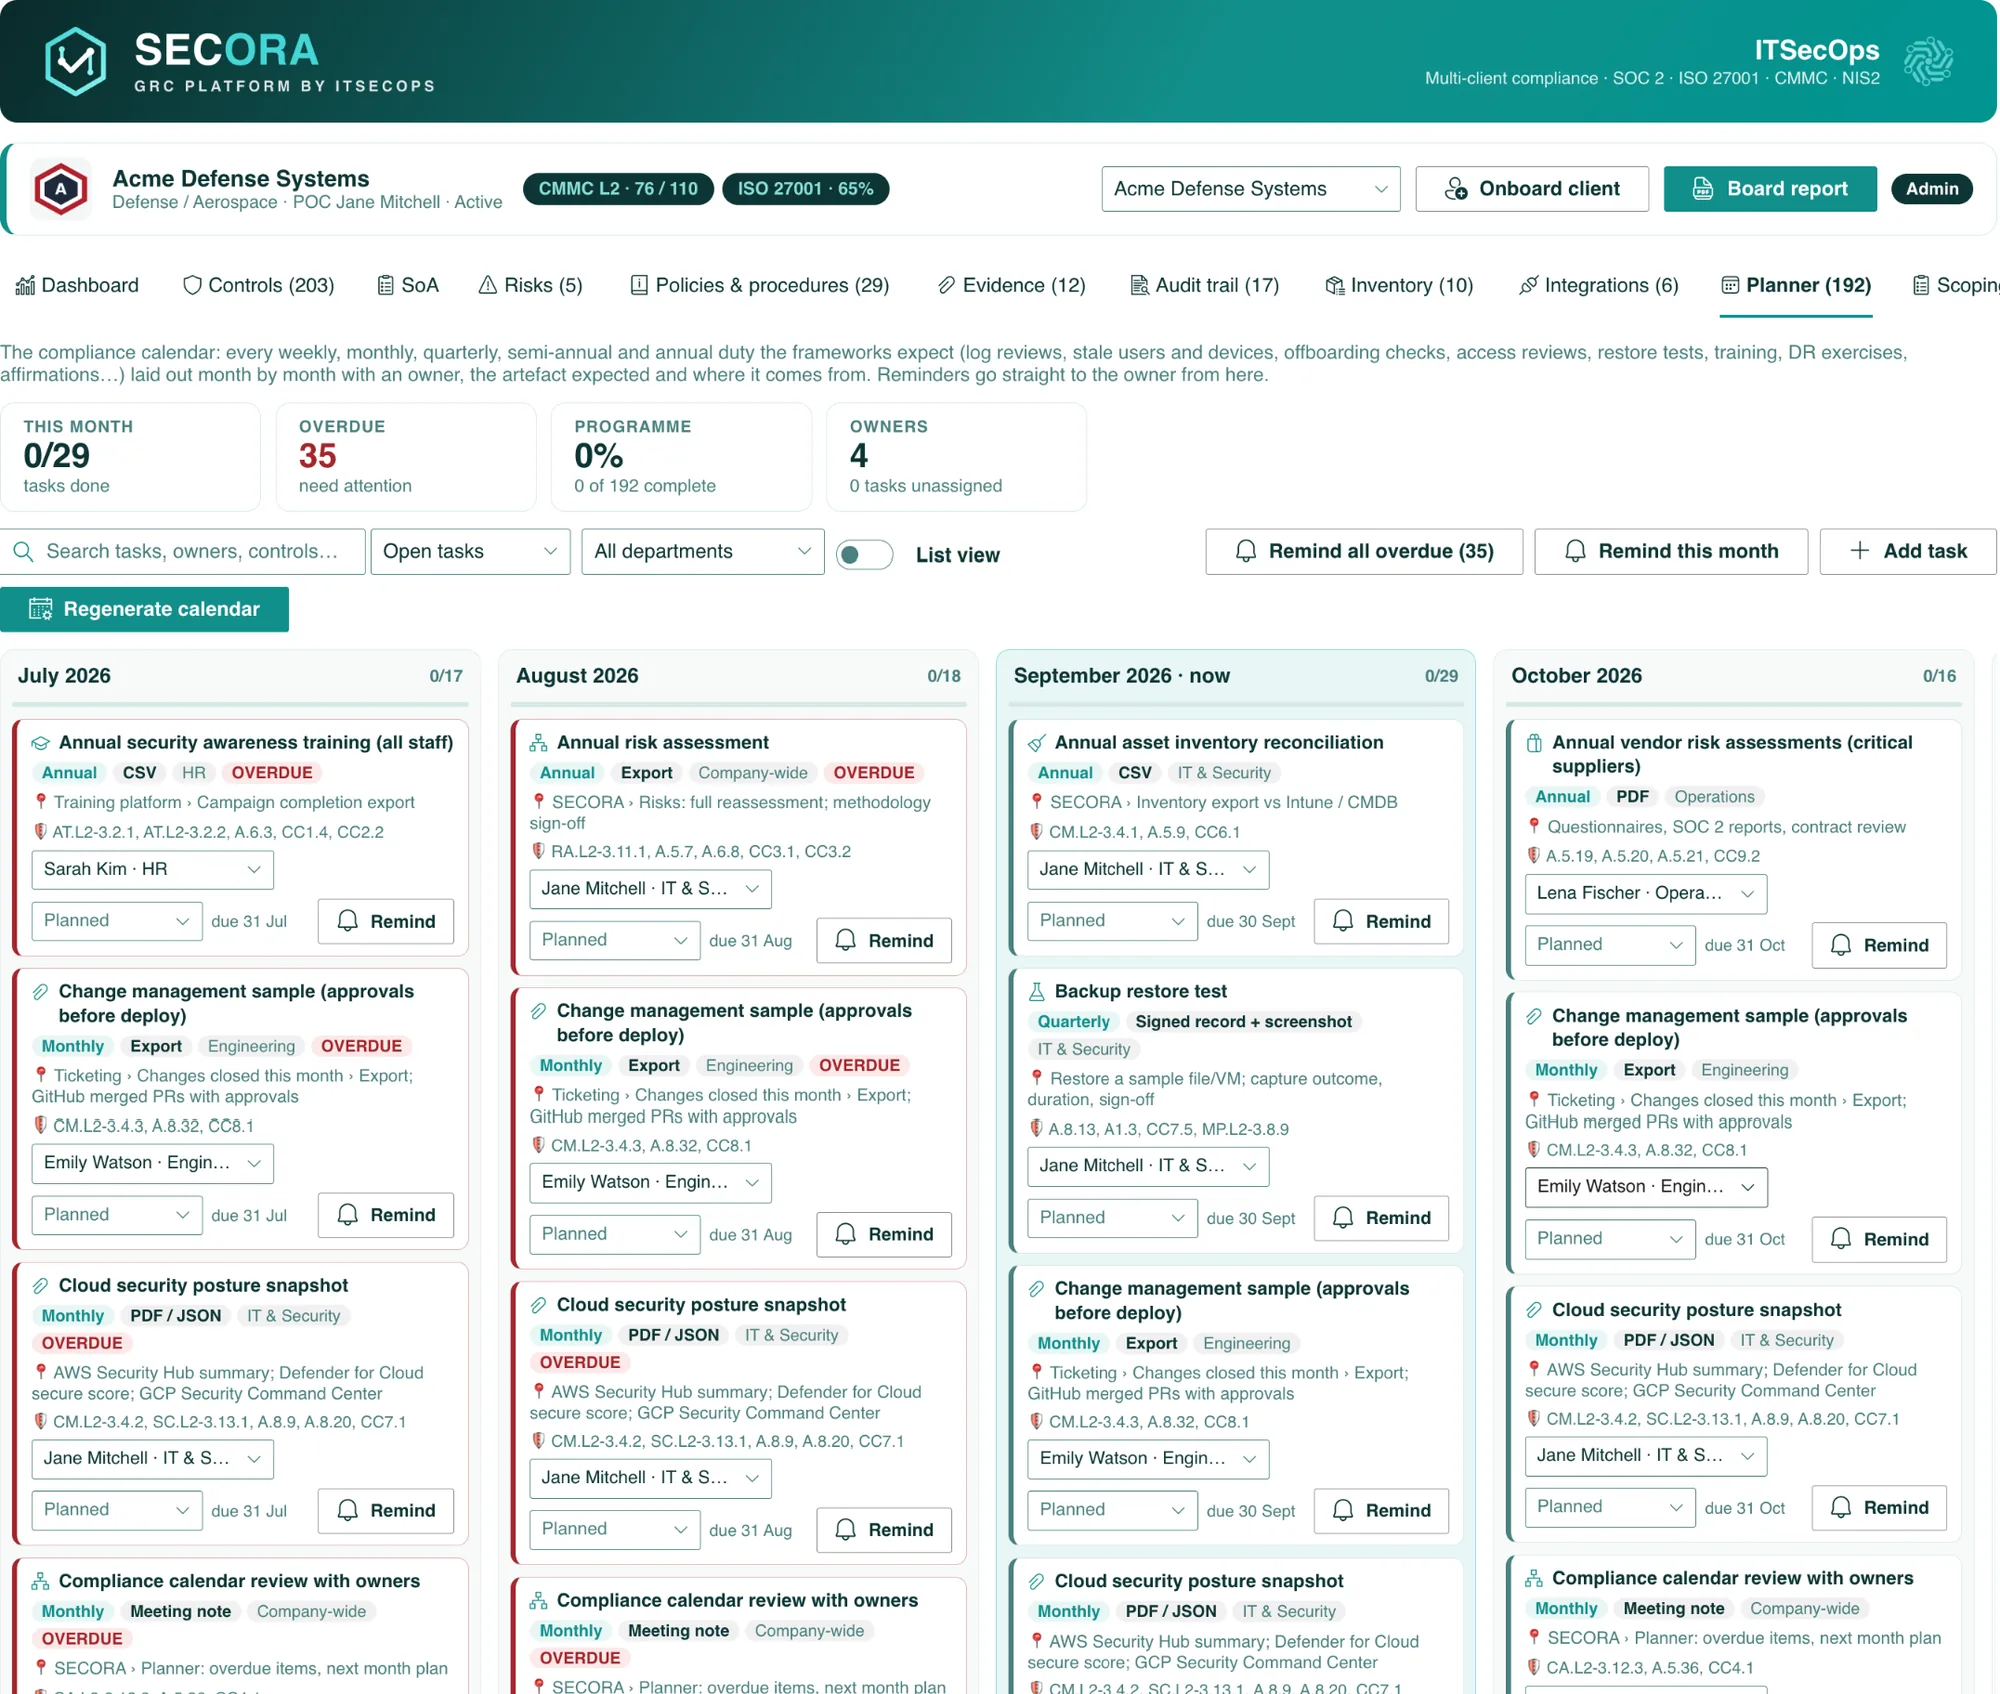
Frameworks are lost between audits, not during them. SECORA turns every weekly, monthly, quarterly, semi-annual and annual duty into a dated task with an owner, the artefact expected and where to get it, and pushes reminders to the owner through Microsoft Graph.

  • 45 recurring duties generated from your environment: SIEM triage, log reviews, stale users and devices, access reviews, restore tests, phishing, vendor check-ins, IR tabletop, pentest, management review, SSP and POA&M refresh.
  • Filtered by estate: Microsoft 365 and Sentinel clients get Purview and Sentinel exports; AWS clients get CloudTrail and IAM reports.
  • Why it matters: SOC 2 Type II is about operating effectiveness over a window, and CMMC assessors sample recurring practices.
Planner (192) · July to October 2026
Compliance calendar with month columns, owners, cadence and remind buttons
06 · SCOPING QUESTIONNAIRE

Ask once. Written everywhere.

Eighty-plus questions across eleven sections: who approves offboarding, the stale-account timeline, the user toolset, the application stack, Intune coverage, backup and DR cadence, SIEM retention, incident reporting windows. Answer once and every policy and procedure is customised, automatically.

  • Answers become the documents: every answer is a merge token and an "Appendix A: organisation-specific implementation" section inside each policy.
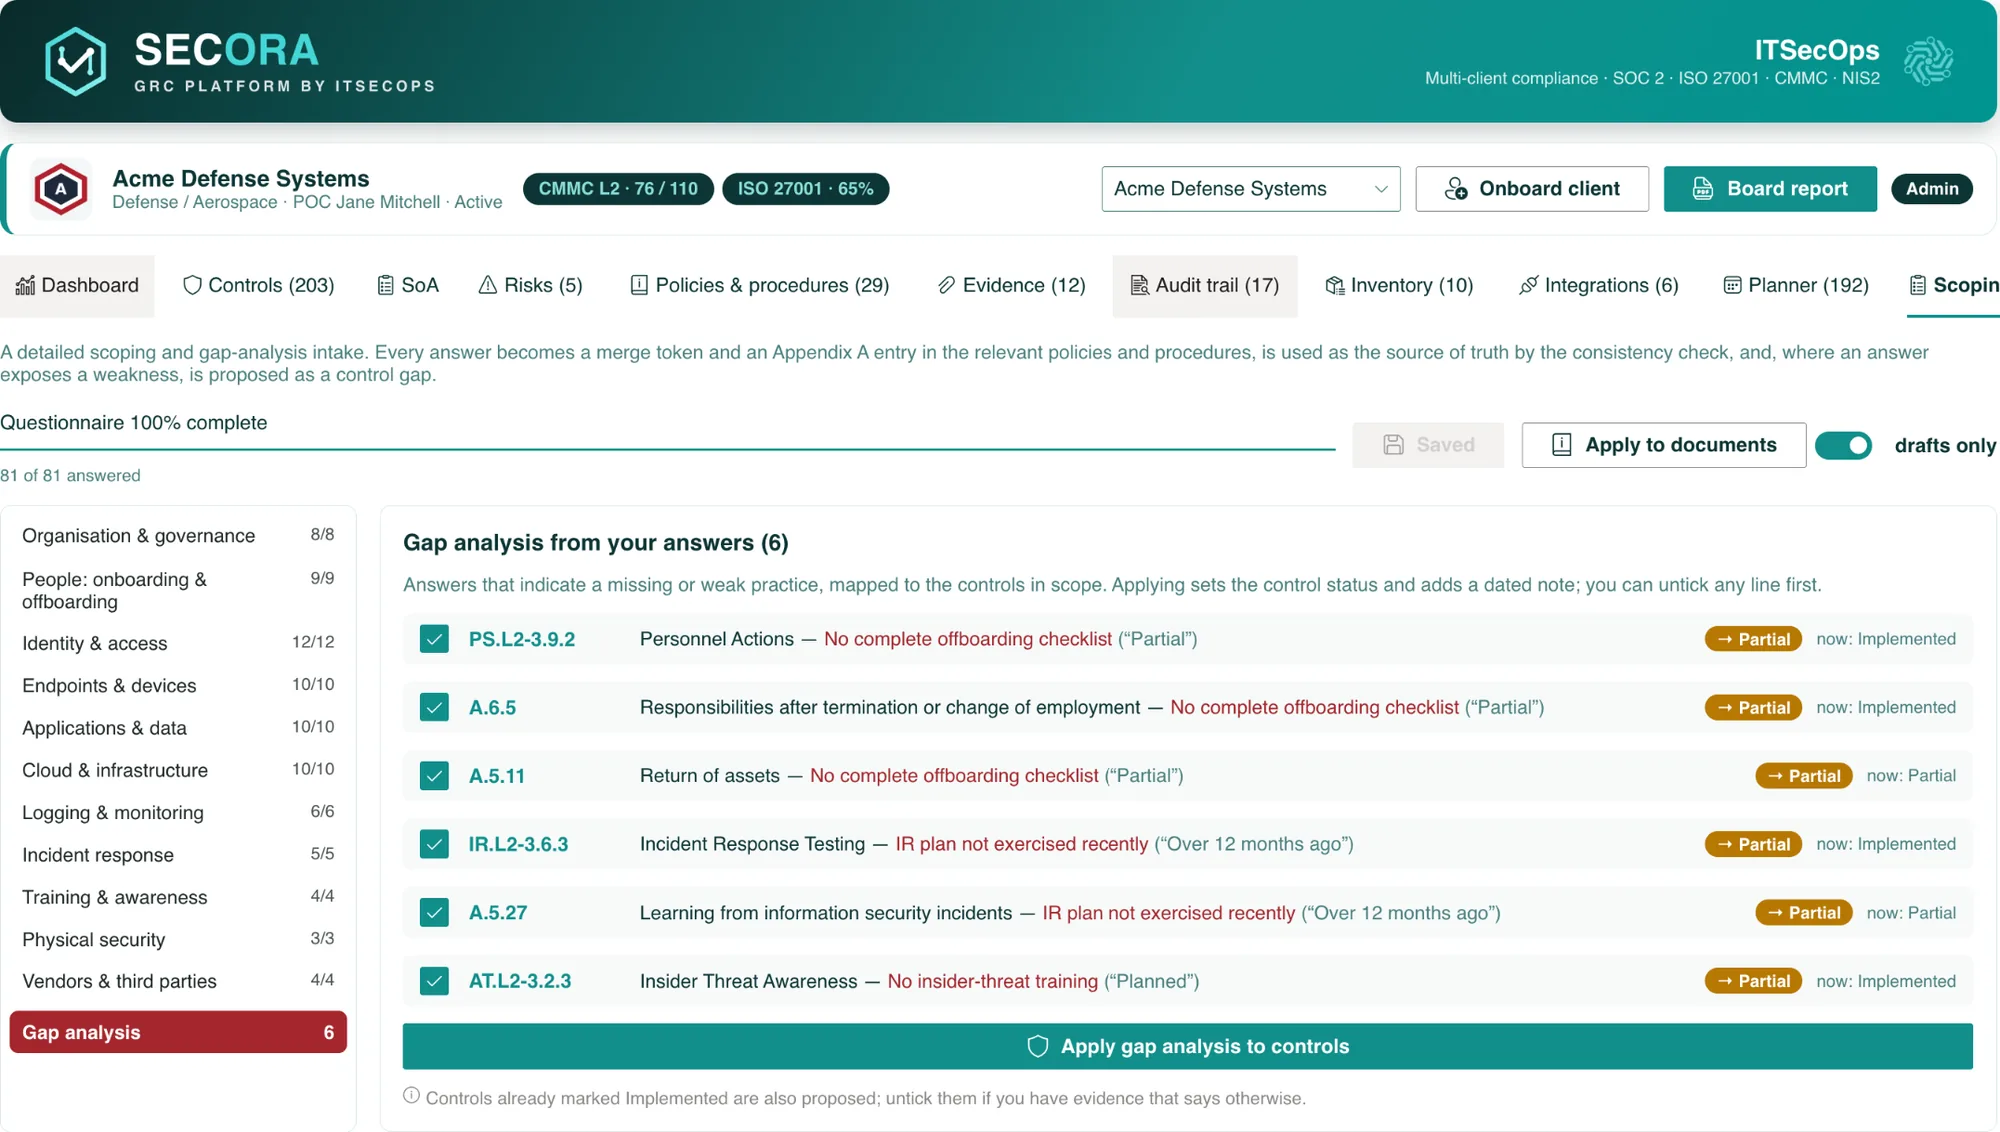
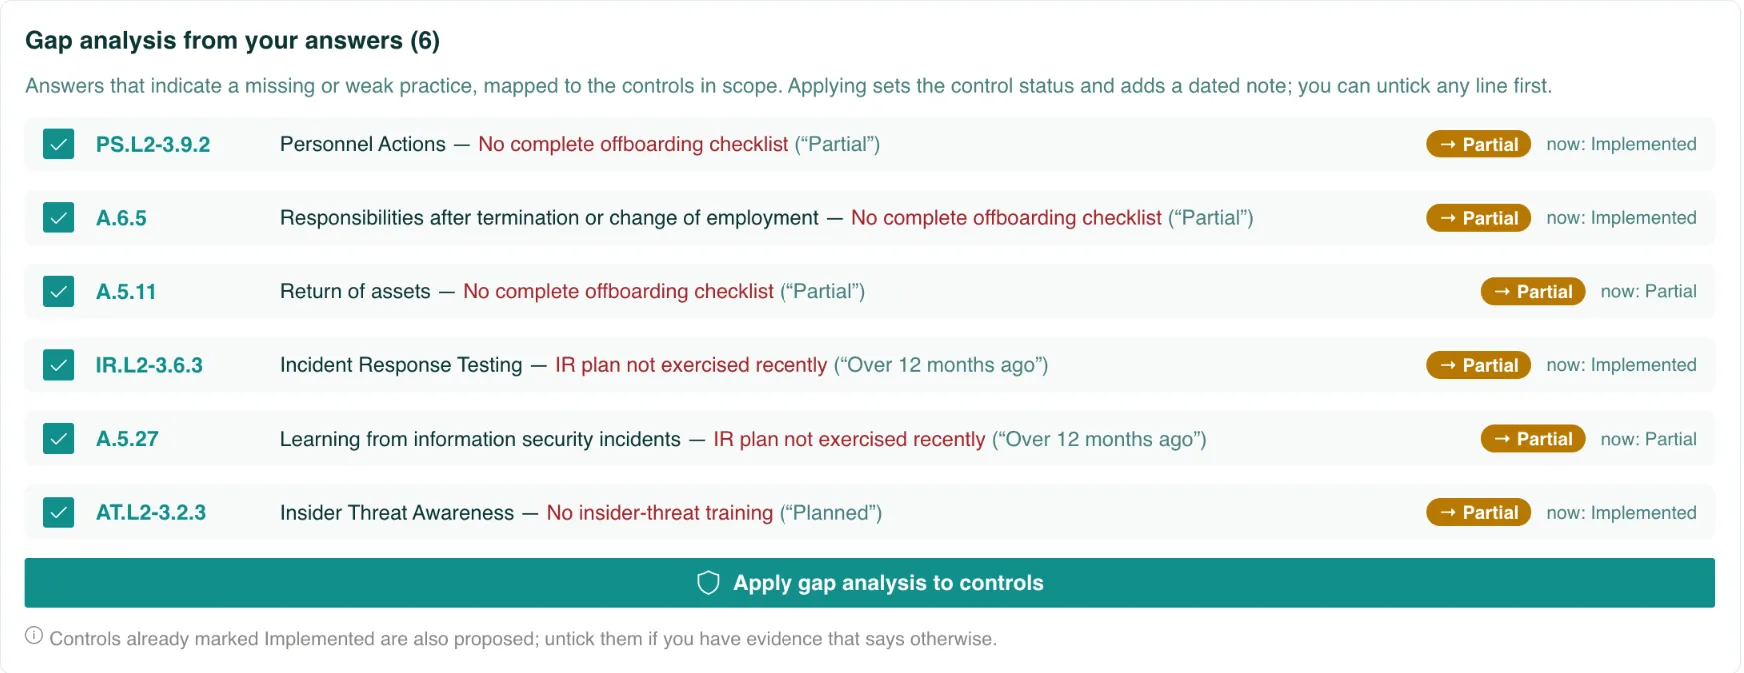
  • Answers become the gap analysis: "no offboarding checklist" maps to the CMMC, ISO and SOC 2 controls it affects, ready to apply or untick.
  • Answers become the source of truth for the consistency engine on the next tab.
Scoping · 81 of 81 answered
Scoping questionnaire with gap analysis from your answers
07 · SMART CONSISTENCY CHECK

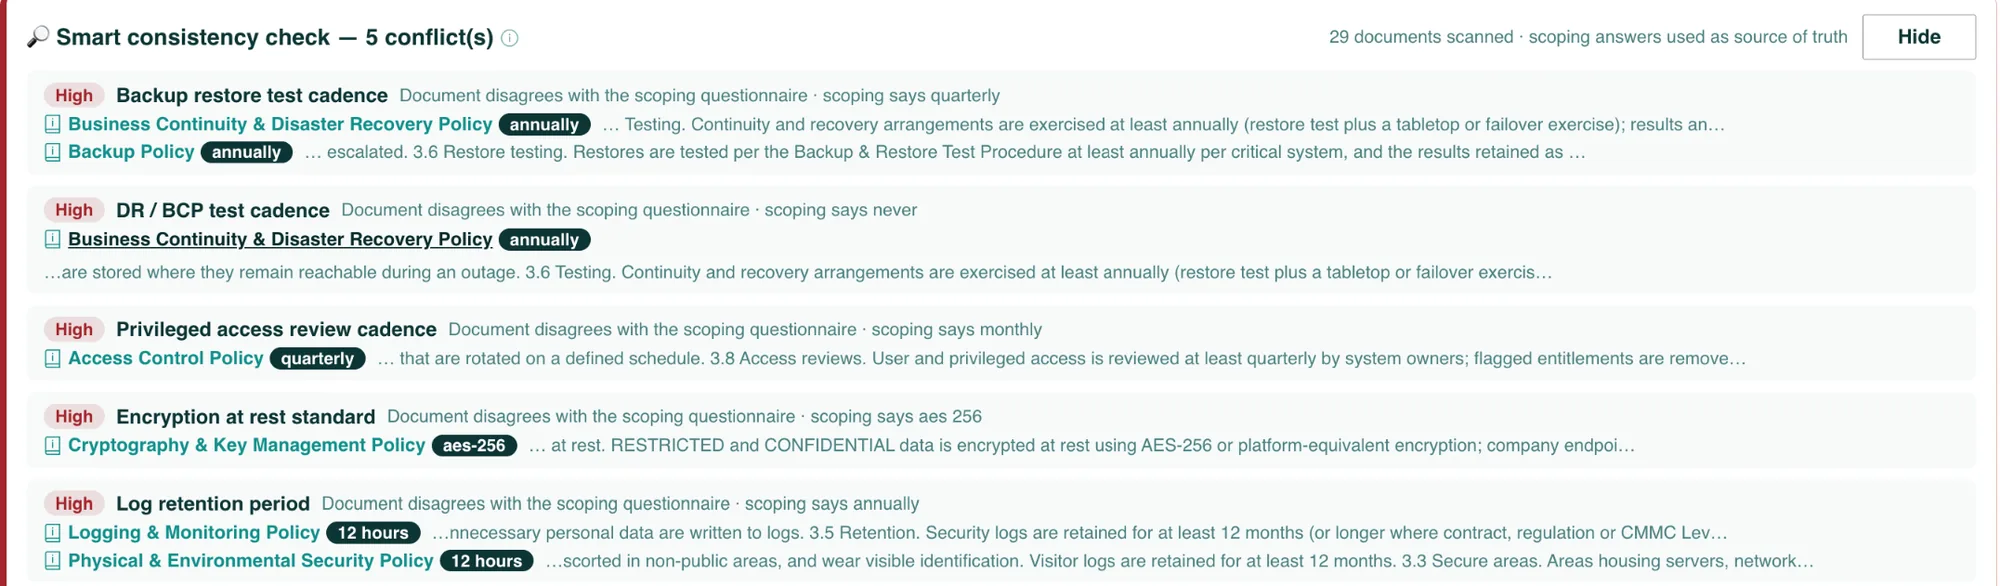
When a policy says "annually" and the procedure says "quarterly", SECORA notices.

Twenty-four measurable parameters (retention, review cadence, password length, offboarding window, lockout, patch SLAs, encryption, TLS, backup and DR cadence) are read out of every document and compared across policies, their linked procedures and your scoping answers. Conflicts carry a red chip and appear in the board report, before an assessor finds them.

Smart consistency check · 5 conflicts
Smart consistency check listing five conflicts between policies and scoping answers
Gap analysis from scoping answers
08 · ROADMAP, INVENTORY, AUDIT TRAIL

Plan it as a Gantt. Ground it in your real estate. Prove it with an append-only trail.

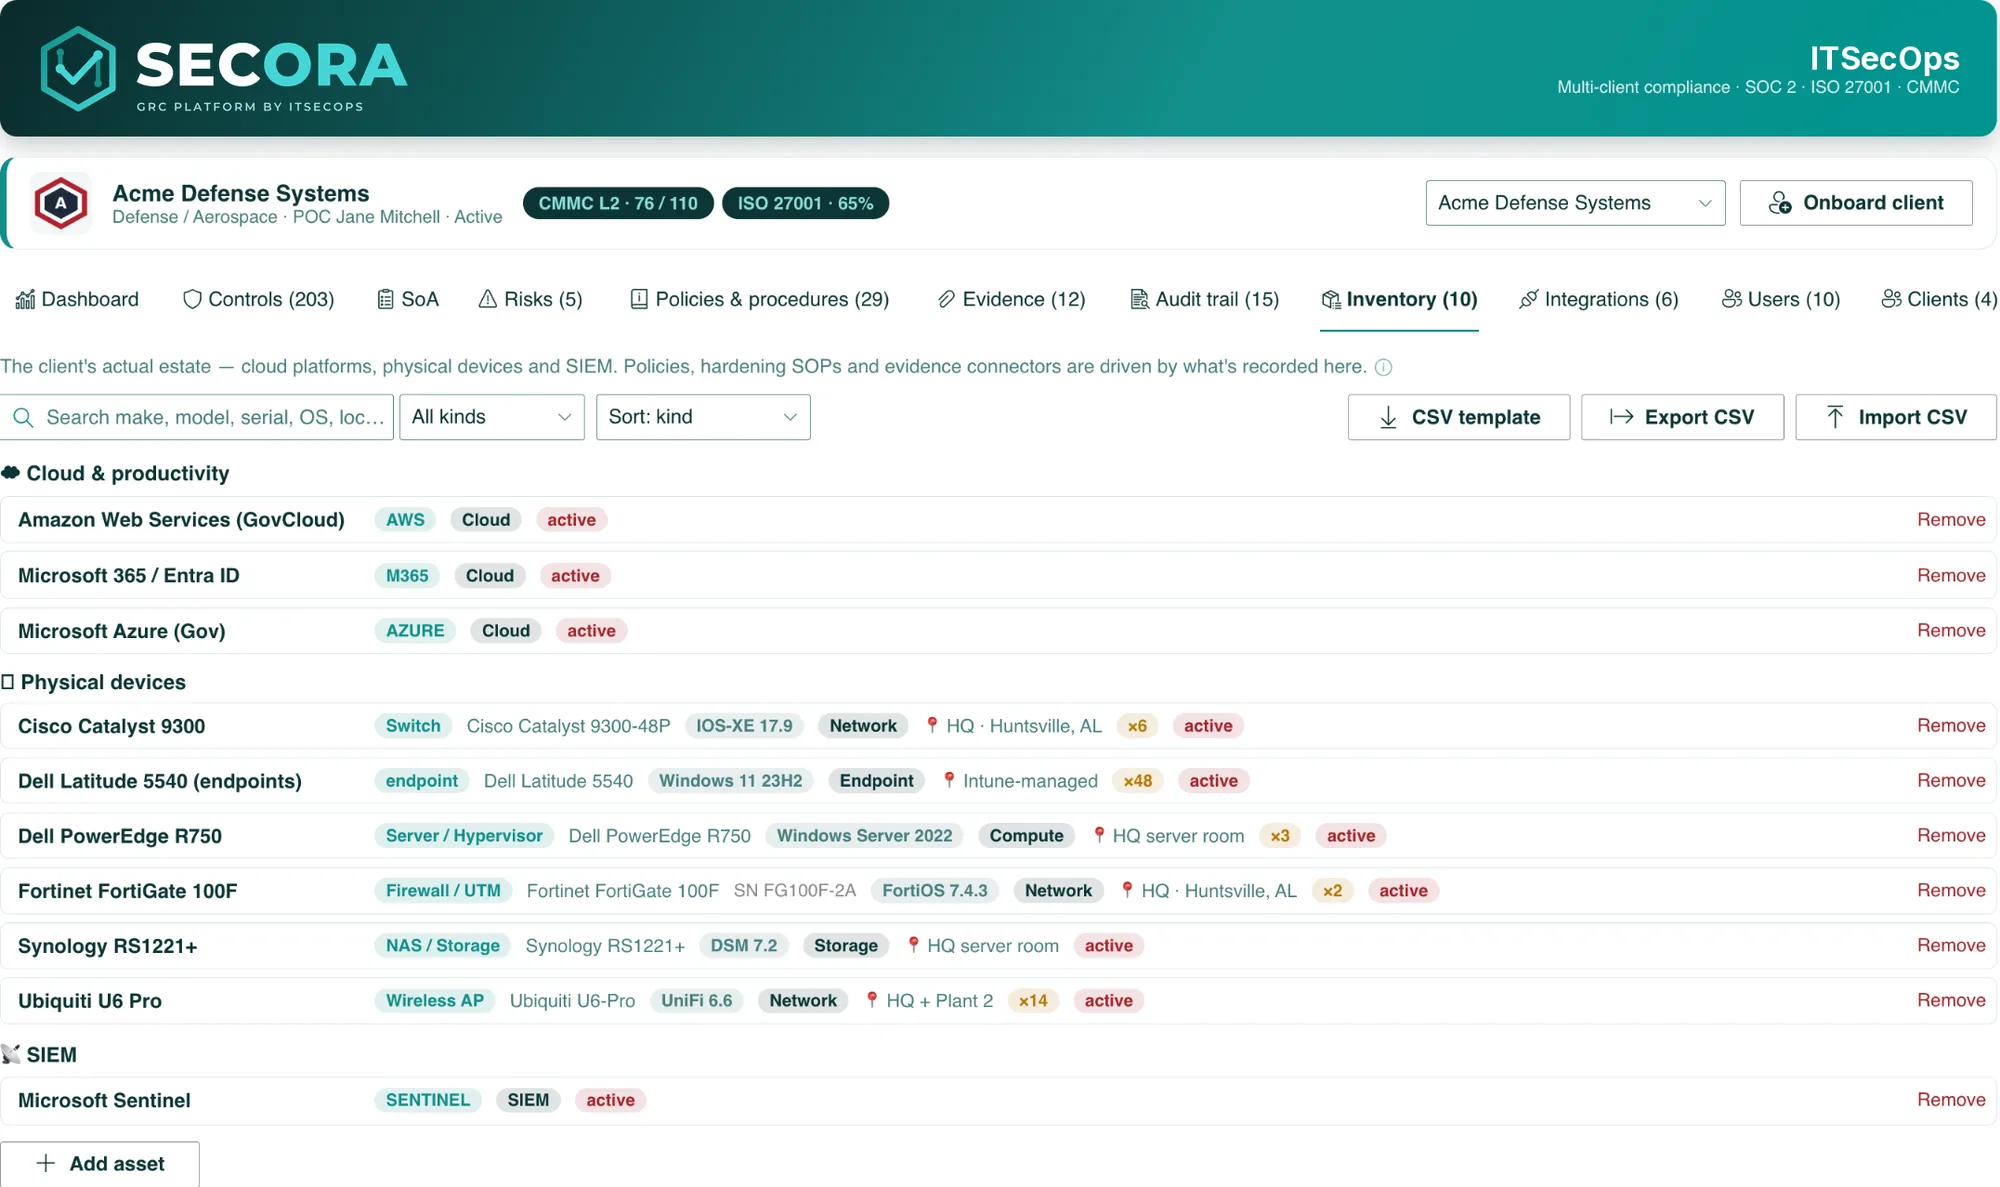
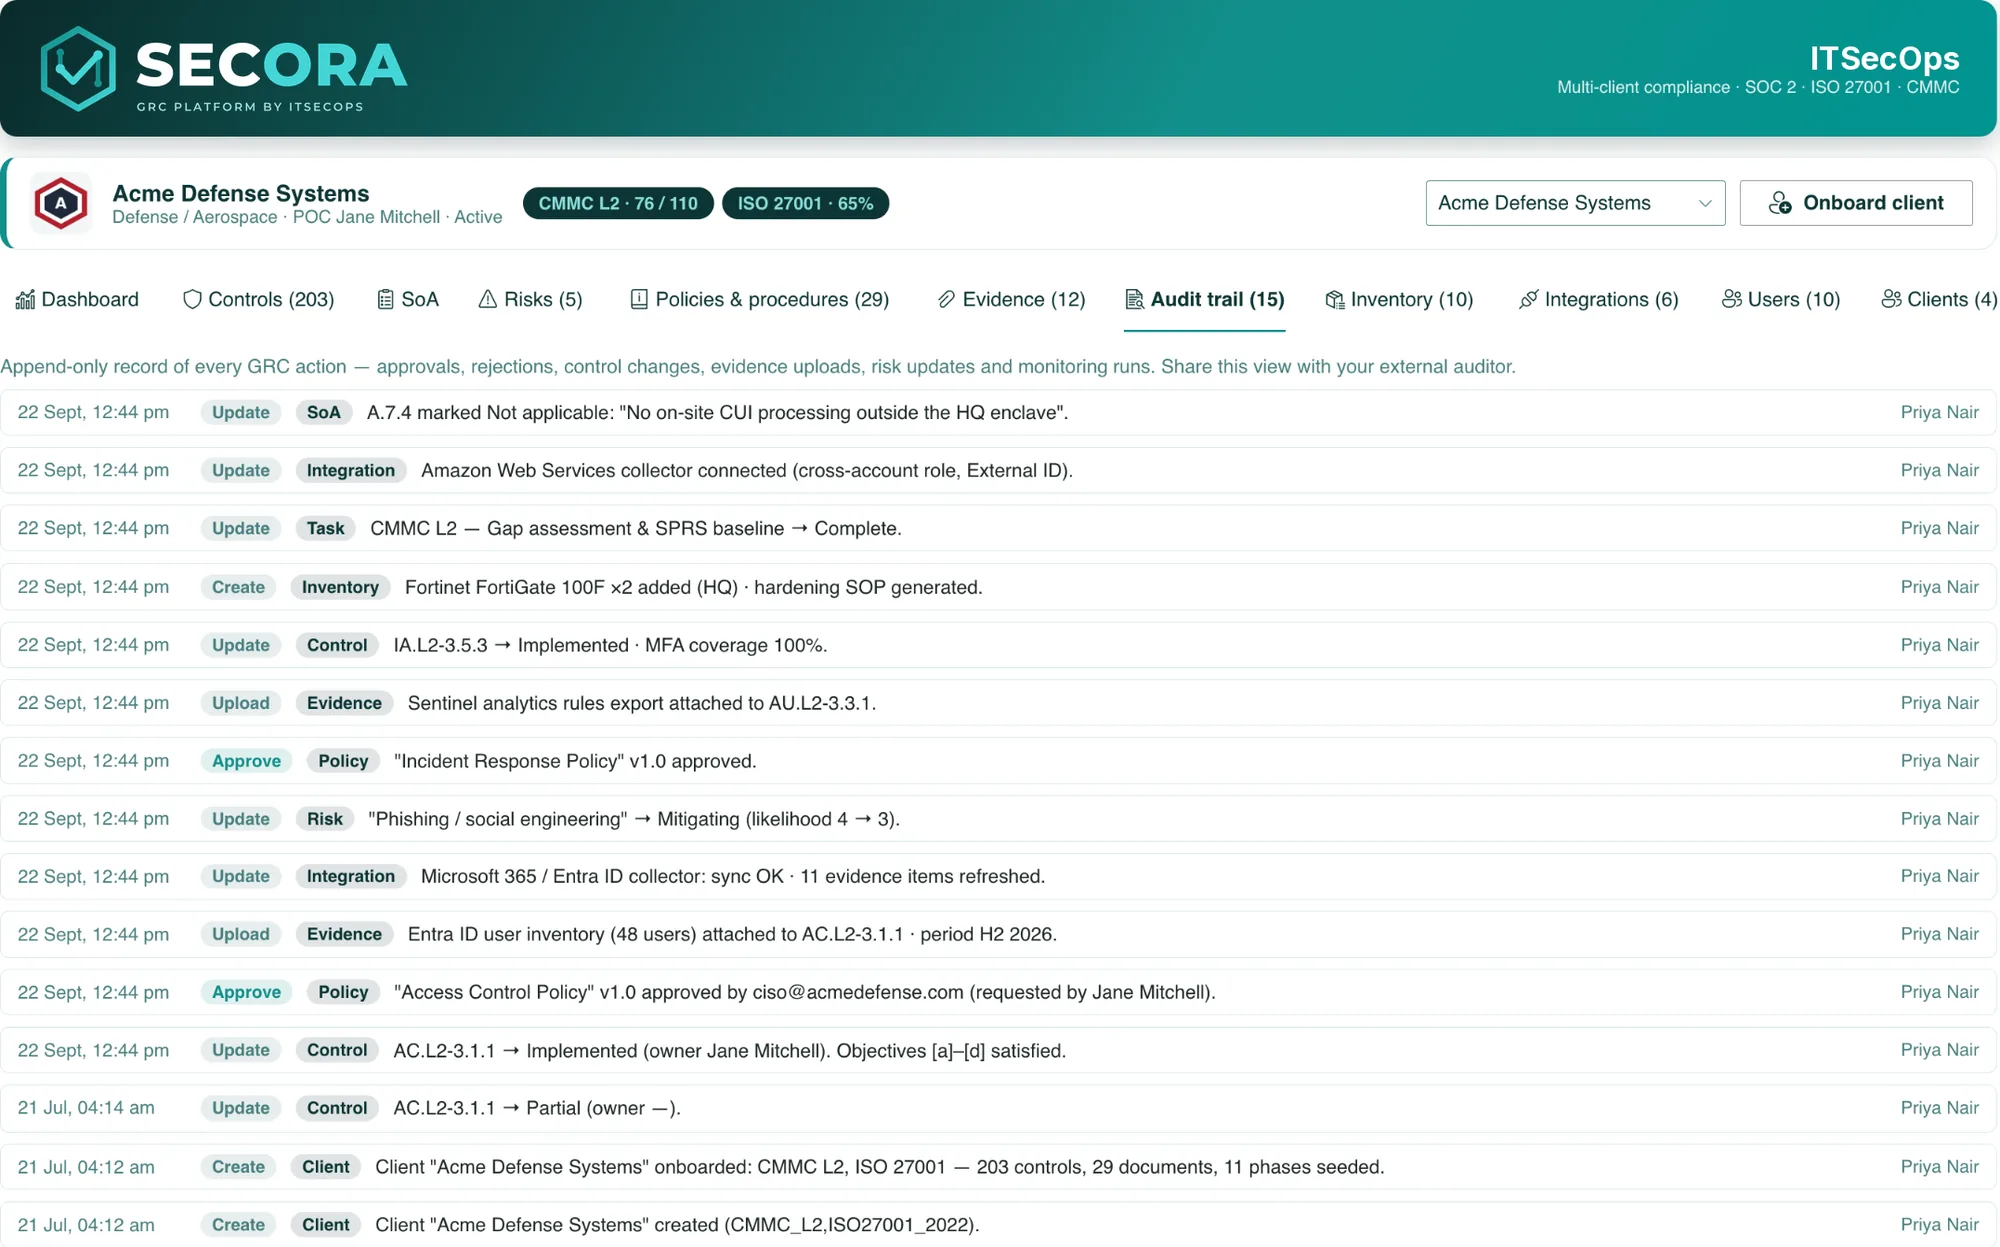
Engagement phases per framework with owners, status and a today marker. An inventory of cloud platforms, physical devices and SIEM that drives which policies, hardening SOPs and evidence connectors are seeded. And an immutable record of every approval, rejection, control change, evidence upload, risk update and monitoring run, shareable with your external auditor.

  • 17 vendor-specific hardening SOP blocks (Fortinet, Cisco, Ubiquiti, Dell and more) generated from your inventory.
  • Integrations catalogue for Microsoft 365, Azure, AWS, Google Cloud and Workspace, GitHub, Microsoft Sentinel, Wazuh, Splunk, Elastic and network devices, with manual evidence as a first-class option.
Inventory
Inventory of cloud platforms, devices and SIEM
Audit trail
Append-only audit trail of every GRC action
09 · ACCESS AND BOARD REPORT

Right people. Right slice. Board-ready in one click.

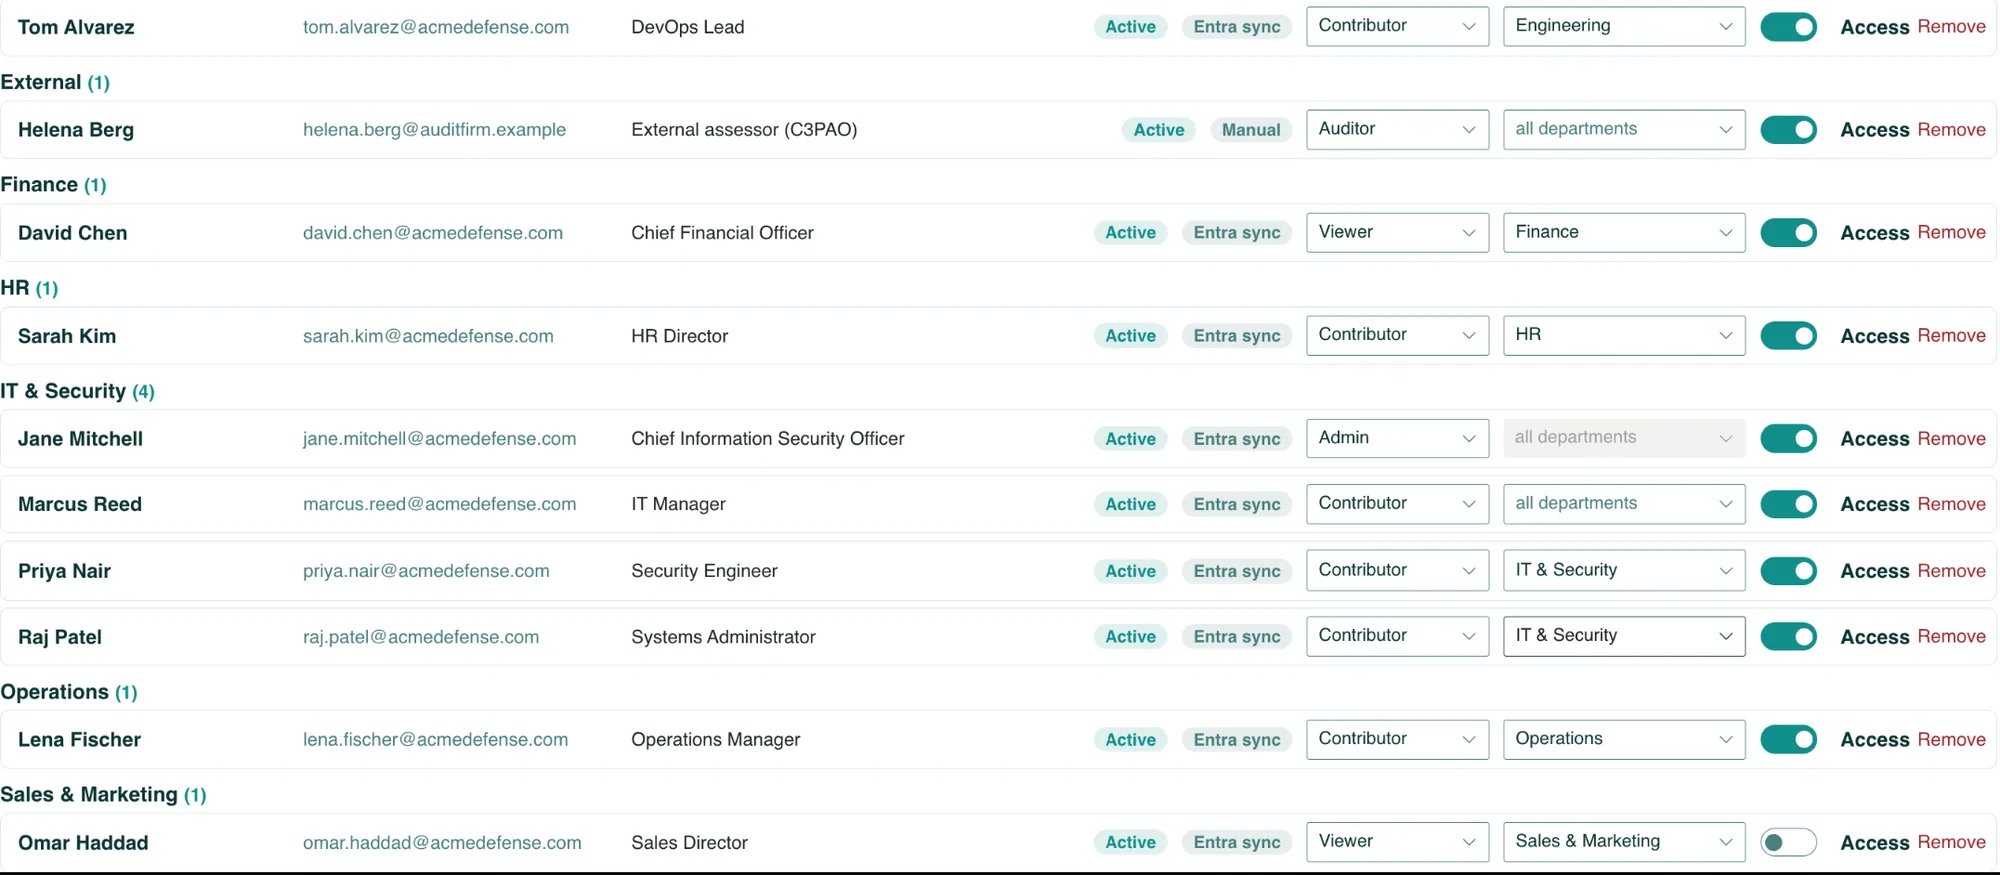
Four roles (Admin, Contributor, Viewer, Auditor) and department-level scope, enforced by SharePoint groups as well as the screen. An HR contributor scoped to HR sees only HR policies, procedures and evidence. Your external assessor is an Auditor with read-only access and the power to mark evidence Verified. Multi-client workspaces partition every record by client for consultancies and MSPs.

Users (10) · roles and department scope
Users table with role, department scope and access switch per person
Control detail panel with linked policies, evidence, checks and risks
0per-user or per-month licence fees, ever
0%of your compliance data stays in your tenant
0controls seeded automatically for a CMMC L2 + ISO 27001 client
0%of documents shared across frameworks in a typical CMMC + ISO programme
0client-branded policies and procedures from the template library
0recurring compliance duties scheduled with owners and reminders
0ready-made evidence recipes with the exact report, format and menu path
0months of maintenance, updates and support by ITSECOPS included

Frameworks

Every framework.
One workstream.

Select the frameworks during onboarding and SECORA seeds the controls, objectives, scoring model, policy set and roadmap. Add a framework later and only the extra controls appear; everything shared is already done. Try it: pick the frameworks you need.

Your programme, modelled
83%

of the document workstream is shared across the frameworks you selected. Do it once. Satisfy all of them.

203controls seeded
29policies and procedures
evidence collection for shared controls

Two frameworks selected: CMMC Level 2 and ISO/IEC 27001:2022. Figures follow the SECORA demo workspace (Acme Defense Systems). Your overlap depends on scope.

Security architecture

Safe by architecture,
not by promise.

SECORA has no cloud of its own. It borrows the one you already trust, secure and audit. Nothing in this picture is new to your risk register.

Your Microsoft 365 tenant · or SharePoint Server on-premises

SharePoint site: /sites/Compliance

Lists: Controls · Policies · Risks · Tasks · Inventory · Users · Integrations (status only) · Audit trail (append-only) · Monitor runs. Library: Evidence (versioned, retention labels).

Item-level permissions · Purview audit log

SECORA web part (SPFx)

Runs in the browser, no backend server. Reads and writes SharePoint REST in the user's context. Microsoft Graph: read-only, admin-consented scopes. No secrets stored, no external endpoints.

Signed package deployed via App Catalog

Microsoft Entra ID

SSO · MFA · Conditional Access · device compliance · PIM for admins · guest governance. Role model: Compliance admins (Full), Control owners (own department), Auditors (read-only).

Your identity policy is SECORA's identity policy

ITSECOPS

Deploys the signed package, configures frameworks, seeds the policy library, maintains it for 12 months. Optional headless evidence collector holds connector credentials outside SharePoint.

Not in the picture

  • Third-party SaaS tenant
  • Vendor cloud holding your evidence
  • AI service ingesting your data
  • Per-user licence server
  • New vendor in your risk register

Data residency and sovereignty

All records live in your tenant's SharePoint lists and libraries, in your Microsoft geography. Encryption at rest and in transit, backup, retention labels, eDiscovery and DLP are Microsoft 365 native and already covered by Microsoft's SOC 2 and ISO 27001 attestations.

Least-privilege Graph scopes

Directory, policy and report scopes are read-only and admin-consented once, tenant-wide. Nothing is granted with app-only write permissions. Every scope is listed in the deployment guide for your review.

No secrets in the portal

Connector credentials (app registrations, cloud roles, API tokens) never live in SharePoint. They are held by a separate, headless evidence collector; the portal stores connection status, last sync and credential age only.

Append-only audit trail

Approvals, rejections, control changes, evidence uploads, risk updates and monitoring runs are written to an immutable trail with actor and timestamp. Microsoft Purview captures views and downloads.

Client isolation for consultancies

Every list row carries a client key; the client switcher re-scopes every tab. Isolation is verified both ways at deployment. Optional guest access lets a client's POC see only their own workspace.

SOC 2 Type II defensible itself

Change control through versioned packages, documented permissions, continuous checks with run history, and evidence freshness that flips controls amber before an assessor does.

Commercial model

One price.
No seats.

SECORA is licensed per organisation, not per user. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over. Twelve months of maintenance by ITSECOPS are included. Optional maintenance renewal from year two. No per-user, no per-month, no per-framework charges.

Competitor figures below: Vendr observed contract medians, February 2026. Page updated 22 September 2026.

What "no per-user cost" means in practice
Invite every control owner, department head, internal auditor and external assessor. Add the next framework. None of it changes the bill.
  • SECORA package, deployment and configuration in your tenant
  • Frameworks of your choice with controls, objectives and scoring
  • Policy and procedure library, client-branded PDF output
  • Dashboard layout and department structure to your preferences
  • Continuous checks for your Microsoft estate
  • 12 months of maintenance, updates and support by ITSECOPS
Get my exact quote
Cost driverPer-user SaaS GRC (Vanta, Drata, Secureframe, Sprinto)SECORA by ITSECOPS
Licence modelPer user or headcount band, per framework, per integration; 5 to 10% annual uplift at renewalOne-time deployment fee per organisation
Adding control owners, auditors, board readersMore seats, more cost; questionnaire caps force tier jumpsUnlimited users in your tenant
Adding a second or third frameworkOften a tier upgrade, mid-contract adds cost 15 to 30% moreIncluded; shared controls already done
Hosting and data residencyVendor cloud (US by default); needs its own vendor risk assessmentYour Microsoft 365 tenant or on-premises SharePoint
Typical first-year spend (SMB, one or two frameworks)Vanta median $20,000, Drata median $25,000, Secureframe median $20,000, Sprinto $8,000 to $30,000, audit fees extraOne quote for your scope, frameworks and estate; no audit-fee lock-in
Maintenance and supportIncluded while you keep paying12 months included by ITSECOPS; optional renewal thereafter
ExitExport and lose historyNothing to export; the lists are already yours

Three-year cost model: per-seat SaaS against SECORA

Move the sliders to your situation. Prices convert to your local currency automatically. The exact SECORA quote for your scope arrives by email.

Currency
Cumulative spend over three years
Year 1
Year 2
Year 3
Per-user SaaS GRC (uplift, seats added over time)SECORA (one-time deployment, optional maintenance renewal)
about halflower three-year spend in this scenario, and the seats, frameworks and history stay yours.
Get my exact SECORA quoteBook a walkthrough instead

Illustrative only. Per-seat SaaS modelled as the selected year-1 subscription with the chosen uplift and 10% seat growth per year. SECORA modelled as a one-time deployment equal to 1.2× that first-year subscription plus an optional 15% annual maintenance renewal from year two, the same assumptions as the SECORA executive brochure. Your quote depends on scope, frameworks and estate size. Competitor medians: Vendr, Feb 2026.

Compare

Looking for a Vanta or Drata alternative that keeps evidence at home?

Every mainstream GRC platform is vendor-hosted, multi-tenant SaaS priced by headcount or seats, with AI evidence mapping that ingests your data. SECORA is the tenant-resident alternative. See how it compares, line by line.

CapabilitySECORAVantaDrataSecureframeSprintoHyperproof
Where your data livesYour Microsoft 365 tenant or SharePoint ServerVendor cloud (AWS, US default)Vendor cloud (US)Vendor cloudVendor cloud (AWS)Vendor cloud (Azure, US and EU)
Pricing modelOne-time per organisation + optional maintenancePer framework + headcount bands + add-onsCompany size + framework countEmployee count + frameworksScope-based bundleNamed users + frameworks + tier
Per-user or headcount feesNoneYesYesYesYesYes
Annual price escalatorNone on the platform5 to 10%5 to 10%5 to 10%Varies3 to 7%
Sign-inEntra ID, your Conditional AccessOwn accounts or SSO add-onOwn accounts or SSOOwn accounts or SSOOwn accounts or SSOOwn accounts or SSO
AI ingesting your evidenceNo, mapping is explicit and reviewableYes (AI agents)Yes (agentic)Yes (Comply AI)YesYes
New vendor in your risk registerNoYesYesYesYesYes
Multi-client edition for MSPs and consultanciesYes, row-level client isolationPartner programmePartner programmePartner programmePartner programmeYes
Deployed byITSECOPS consultants, CISA-certified, fixed scopeSelf-serve + CSMSelf-serve + CSMSelf-serve + CSMSelf-serve + CSMVendor services

Deployment and next steps

Live in your tenant in weeks, not quarters.

A fixed-scope engagement delivered by the people who built the platform.

1

Discovery

Frameworks, scope, departments, estate inventory, branding preferences and dashboard layout agreed in a short workshop.

2

Deploy in your tenant

Signed package uploaded to your App Catalog, sites and lists provisioned, permissions applied and verified with a non-admin test user.

3

Configure and seed

Frameworks, policy library, roadmap phases, connectors and your dashboard preferences configured by the ITSECOPS team. Optional migration from spreadsheets.

4

Hand-over and 12 months of care

Admin walkthrough, owner onboarding, documentation. Updates, framework content refreshes and support included for a year.

What is included

  • SECORA package, deployment and configuration in your tenant
  • Frameworks of your choice, with controls, objectives and scoring
  • Policy and procedure library, client-branded PDF output
  • Dashboard layout and department structure to your preferences
  • Continuous checks for your Microsoft estate
  • 12 months of maintenance, updates and support by ITSECOPS

Optional services

Who it is for

Built by practitioners, for practitioners

SECORA was developed by ITSECOPS, a cybersecurity and compliance consultancy that runs SOC 2, ISO 27001 and CMMC programmes for regulated SMBs and MSPs. It is the portal we wished the SaaS tools were: inventory-driven, auditor-friendly and honest about where your data lives.

Regulated SMBs

50 to 1,000 people on Microsoft 365 that need ISO 27001, SOC 2, NIS2, HIPAA or GDPR without a new vendor, a per-seat bill or a spreadsheet.

Defense contractors

CMMC Level 1 and 2 with 800-171A objectives, SPRS scoring that matches the DoD's, SSP and POA&M phases, and evidence that never leaves your GCC or commercial tenant.

MSPs and consultancies

The multi-client edition: every record partitioned by client, the switcher re-scopes every tab, guest access for each client's POC. Details

vCISO programmes

Pair SECORA with ITSECOPS vCISO coaching so the calendar, the evidence and the board report run themselves between quarterly reviews. vCISO + SECORA

Questions

Frequently asked about SECORA

No. SECORA is a signed SharePoint Framework package deployed into your own Microsoft 365 tenant, or onto a SharePoint Server you host. Controls, policies, risks, evidence, tasks and the audit trail are SharePoint lists and libraries in your tenant's Microsoft geography. There is no SECORA cloud, no vendor database and no third-party AI service holding your data.

CMMC Level 1 and Level 2 (with NIST SP 800-171A assessment objectives and official SPRS scoring), ISO/IEC 27001:2022 (93 Annex A controls and a live Statement of Applicability), SOC 2 Type II (Trust Services Criteria), NIS2 (Article 21 measures), HIPAA, GDPR and NIST CSF 2.0. Industry or customer-specific control sets, for example a prime contractor questionnaire, are loaded by the ITSECOPS team during deployment. Shared controls are collapsed into one workstream so evidence is collected once.

SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance and support by ITSECOPS included. There are no per-user, per-month or per-framework charges. Invite every control owner, department head and your external auditor without changing the bill. An optional maintenance renewal is available from year two. Use the three-year cost model above or request an exact quote.

Yes, for organisations that want the automation and structure of a GRC platform without a vendor-hosted SaaS, per-seat pricing or AI ingestion of their evidence. Vanta and Drata run in their own clouds and are priced by headcount and frameworks with typical 5 to 10% annual uplifts. SECORA runs in your Microsoft 365 tenant with a one-time deployment fee. Read the detailed SECORA vs Vanta and SECORA vs Drata comparisons.

Yes. SECORA deploys to Microsoft 365 commercial and GCC tenants and to SharePoint Server on-premises where SharePoint Framework is supported. Deployment to a sovereign or on-premises environment is scoped during discovery.

Your assessor is added as an Auditor: read-only across the portal, evidence-centric views, and the ability to mark evidence Verified. Roles map to SharePoint groups with Full, Contribute and Read permissions on every GRC list, so a Viewer or Auditor cannot write even through the REST API. The append-only audit trail can be shared as a view.

Microsoft 365, Entra ID and Microsoft Sentinel out of the box through read-only, admin-consented Graph scopes. The integrations catalogue also covers Azure, AWS, Google Cloud and Workspace, GitHub, Wazuh, Splunk, Elastic and network devices, delivered through a separate headless evidence collector so connector credentials never touch SharePoint. Manual evidence upload is a first-class option with 55 ready-made evidence recipes telling owners exactly what to export.

No evidence is sent to third-party AI services. Policies are generated from a template library merged with your scoping answers, inventory and branding, so every document describes your organisation and can be checked for consistency by a deterministic engine. Control mapping is explicit and reviewable.

Weeks, not quarters. Discovery workshop, deployment to your App Catalog, configuration and seeding of frameworks and policies, then hand-over. Migration from existing spreadsheets is optional. A walkthrough in your own tenant is the fastest way to see the timeline for your scope.

Yes. The multi-client edition partitions every record by client key, the client switcher re-scopes every tab instantly, and optional guest access lets each client's point of contact see only their own workspace. Isolation is verified both ways during deployment. SECORA for MSPs and consultancies.

SECORA, GRC platform by ITSECOPS

Ready for a walkthrough
in your own tenant?

Tell us your frameworks and estate. A CISA-certified ITSECOPS consultant replies within one business day with a walkthrough slot, the deployment scope for your tenant and a written quote. No newsletter, no phone call unless you ask for one.

What happens next: a consultant replies by email within 1 business day with slots and a written scope. No phone call unless you ask for one. No newsletter.

Book a walkthrough in your tenant