 SEC
 by ITSECOPS
Why buyers want GRC data in their own environment
A GRC platform holds a map of your weaknesses: every unimplemented control, every open risk, every policy exception and the evidence behind them. Three things pushed that concern to the front in 2026. The Klue OAuth supply-chain breach in June pulled Salesforce data from 195 organisations including a GRC vendor, the third such incident after Salesloft Drift and Gainsight. European sovereignty pressure produced Microsoft’s expanded EU Data Boundary and partner-operated sovereign clouds while regulators kept asking about US transfers. And defense contractors under CMMC keep learning that CUI-adjacent evidence in a US SaaS is still a question on the assessor’s list. Third-party involvement in breaches doubled from 15% to 30% in 2025.
The options, honestly compared
| Option | Examples | Where data lives | Who maintains it | Cost shape | Fit |
|---|---|---|---|---|---|
| Enterprise on-premises suites | Archer, ServiceNow IRM, IBM OpenPages | Your data centre or private cloud | Your team plus vendor services | Six figures plus implementation | Banks, insurers, large enterprise |
| Open source | Eramba, CISO Assistant, SimpleRisk, GovReady, VerifyWise | Your servers | Your engineers | Free or paid tier plus hosting and time | Teams with engineering capacity and appetite to build framework content |
| DIY SharePoint lists | Custom ISMS on SharePoint, ConvergePoint add-ins | Your Microsoft 365 tenant | Your team | Internal time, fragile | Small teams; usually outgrown at the first audit |
| Tenant-resident platform | SECORA by ITSECOPS | Your Microsoft 365 tenant or SharePoint Server | ITSECOPS (12 months included) | One-time deployment per organisation | Regulated SMBs, defense suppliers, NIS2 entities, MSPs on Microsoft 365 |
| Vendor SaaS | Vanta, Drata, Secureframe, Sprinto, Hyperproof | Vendor cloud | Vendor | Annual subscription per seat, headcount or module | Cloud-native startups with many SaaS integrations |
What tenant-resident means in practice
SECORA is a signed SharePoint Framework package. It runs in the browser against your SharePoint REST API in the user’s own context; there is no backend server, no database to expose, no inbound port and no external endpoint. Microsoft Graph scopes are read-only and admin-consented once. Connector credentials for AWS, Azure or SIEMs live in a separate headless collector, never in SharePoint. Updates are versioned packages you approve in your App Catalog. Your Entra ID Conditional Access, MFA, PIM, retention labels, eDiscovery, DLP and Purview audit apply to every record because they are simply SharePoint records.
That is the sovereignty of self-hosting without the self-hosting: no servers to patch, no framework content to write, no engineers on the hook, and a consultancy that deploys, seeds and maintains it for a year.
SharePoint Server on-premises
For organisations that cannot use Microsoft 365 at all, SECORA deploys onto SharePoint Server where the SharePoint Framework is supported. Evidence collection from cloud services is replaced by manual recipes or an on-premises collector; everything else works the same way.
If you are considering open source
Eramba, CISO Assistant and SimpleRisk are credible and improving. Budget for hosting, backups, patching, single sign-on integration, framework content (CMMC objectives, ISO 2022 controls, NIS2 measures), policy templates and the evidence recipes your owners will need. If your team has that capacity, they are a good choice. If it does not, the total cost of ownership usually exceeds a one-time SECORA deployment within the first year, and the audit still has to be passed.
How SECORA works in your tenant
SECORA is a signed SharePoint Framework (SPFx) package. ITSECOPS uploads it to your Microsoft 365 App Catalog (or a SharePoint Server you host), provisions a Compliance site with the GRC lists and an evidence library, applies permissions and seeds your frameworks. From then on your team signs in with Entra ID, under your MFA and Conditional Access, and every control, policy, risk, task and piece of evidence is a SharePoint record in your own Microsoft geography.
- Controls with family roll-ups, owners, priorities, SPRS weights, linked policies and evidence counts, mapped across every framework you select.
- Policies and procedures generated from 29 client-neutral templates, merged with your scoping answers, approved by email and exported as client-branded PDFs.
- Evidence library with a freshness clock per file, 55 evidence recipes that tell owners the exact report and menu path, and automated evidence from Microsoft 365, Entra ID and Sentinel.
- Risk register with a 5×5 heatmap, mitigation tracking and control mapping.
- Compliance calendar that turns 45 recurring duties into dated tasks with owners and reminders sent through Microsoft Graph.
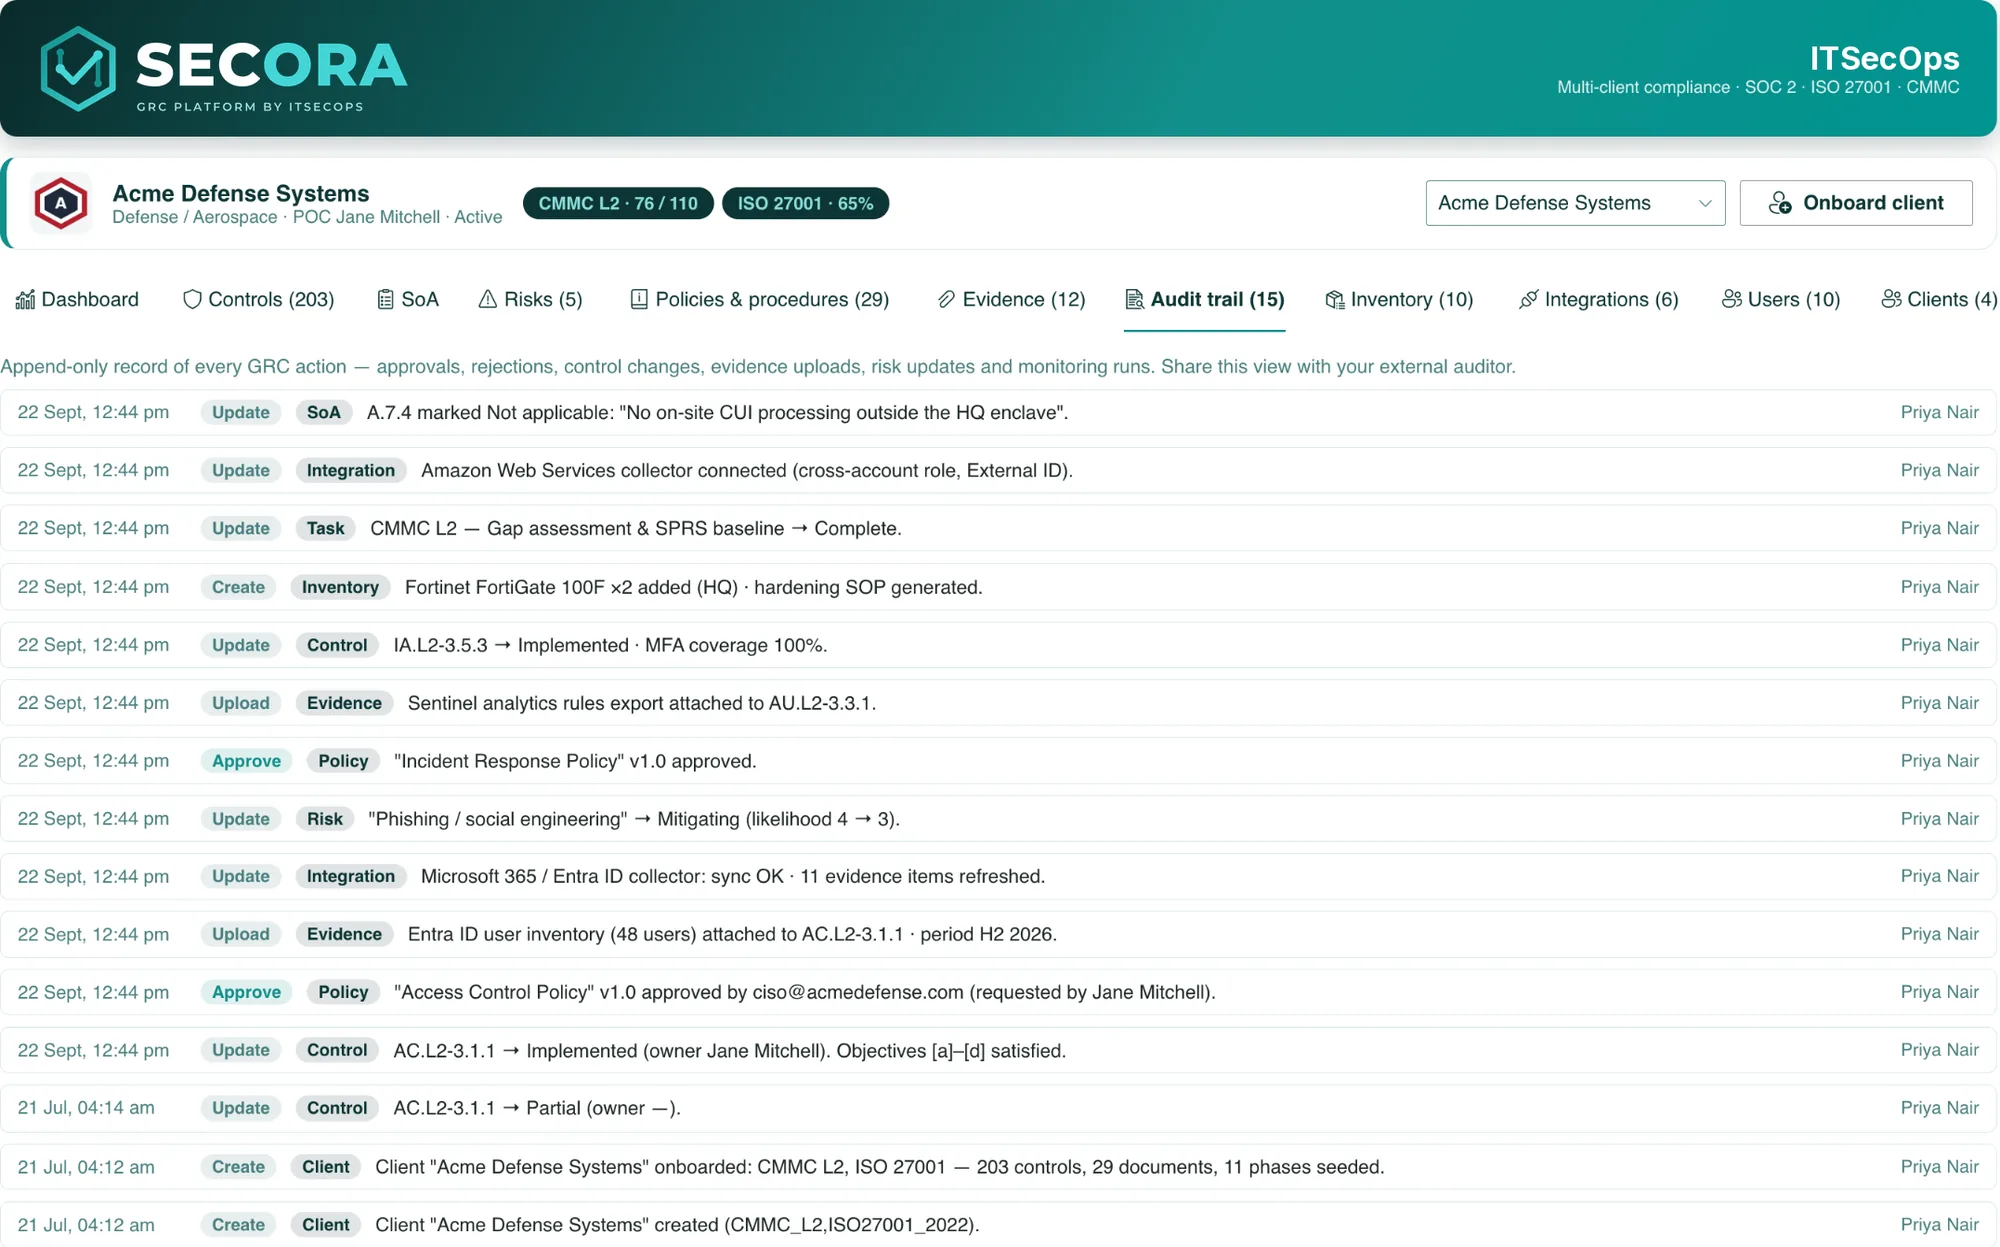
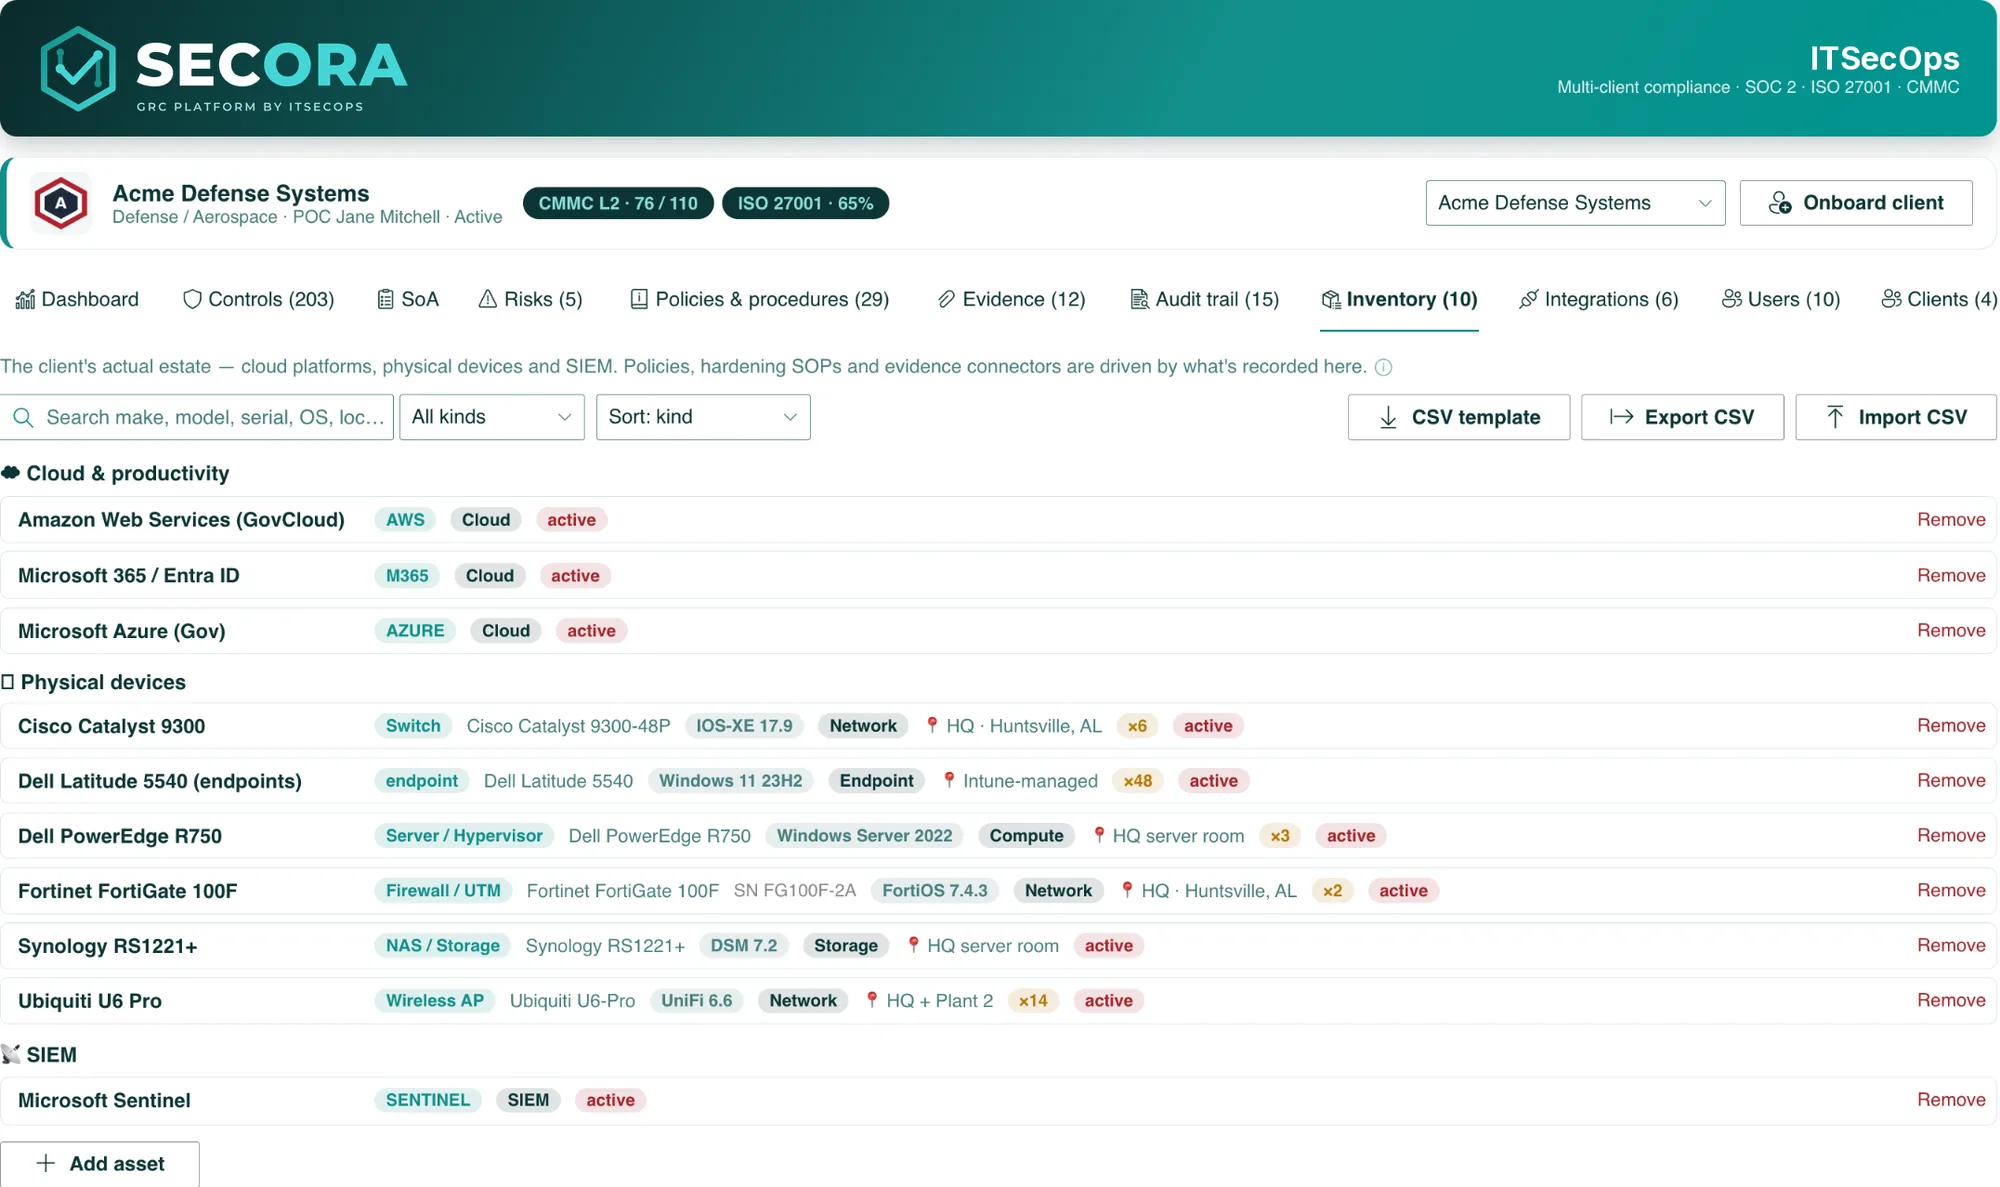
- Scoping questionnaire, consistency check, roadmap, inventory, append-only audit trail and one-click board report.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Sources: CSA research note: ShinyHunters OAuth SaaS abuse, Jul 2026 · KuppingerCole: Microsoft sovereign cloud 2026 · Cyber Sierra: GRC software own cloud deployment · Compyl: state of GRC 2026. Competitor figures are observed contract data or published estimates, not list prices; verify with the vendor.
Frequently asked
SECORA is tenant-resident: it runs inside your own Microsoft 365 tenant or SharePoint Server as a signed SharePoint Framework package. You get the data sovereignty of self-hosting without servers to run, because SharePoint is the host.
Not as a packaged product. Published guides show DIY ISMS trackers built on SharePoint lists; SECORA is the packaged, maintained alternative with framework content, policy templates, evidence recipes and a compliance calendar.
On SharePoint Server on-premises, yes, with manual evidence collection. Cloud evidence connectors need outbound access from the collector, not from the portal.
Nothing at rest. ITSECOPS deploys the package into your tenant and maintains it; there is no ITSECOPS cloud holding your data. Support access is granted by you, scoped and revocable.
In your own Microsoft 365 tenant or SharePoint Server: SharePoint lists for controls, policies, risks, tasks, inventory and the audit trail, and a versioned document library for evidence. SECORA has no cloud of its own and no vendor database.
No. SECORA is licensed per organisation with a one-time deployment fee and twelve months of maintenance included. Invite every control owner, department head and external auditor without changing the bill.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.