 SEC
 by ITSECOPS
Why the overlap is so high
Every serious framework asks for the same underlying practices with different numbering: an access control policy, MFA, logging and monitoring, backup and restore testing, incident response, vendor management, awareness training, change management and risk assessment. ISO/IEC 27001:2022 expresses them as 93 Annex A controls, CMMC Level 2 as 110 practices from NIST SP 800-171 with 320 assessment objectives, SOC 2 as Trust Services Criteria, NIS2 as ten Article 21 measure areas, HIPAA as administrative, physical and technical safeguards, NIST CSF 2.0 as 106 subcategories across Govern, Identify, Protect, Detect, Respond and Recover. In the SECORA demo workspace a CMMC Level 2 plus ISO 27001 client needs 29 documents, of which 24 cover both frameworks: 83% shared.
Common pairs, explained
ISO 27001 and SOC 2
The closest pair. SOC 2’s Common Criteria map to ISO’s organisational and technological controls almost one to one; SOC 2 adds the observation window and the availability, confidentiality and processing-integrity criteria. An ISO ISMS gets you most of a SOC 2 with the addition of continuous evidence over the period.
CMMC Level 2 and ISO 27001
CMMC is prescriptive (specific practices with assessment objectives) while ISO is risk-based. In practice the access, identification, audit, configuration and incident families cover the same ground as Annex A 5 to 8. CMMC adds CUI scoping, SPRS scoring and the SSP and POA&M documents; ISO adds the Statement of Applicability, management review and internal audit.
NIS2 and ISO 27001
NIS2 Article 21 lists the measure areas (risk analysis, incident handling, business continuity, supply chain, secure development, effectiveness assessment, training, cryptography, HR security and access control, MFA and secure communications). An ISO 27001 ISMS covers them; NIS2 adds the 24 hour early warning and 72 hour incident notification duties, management accountability and national registration.
HIPAA and SOC 2
The HIPAA Security Rule safeguards overlap with SOC 2 security and confidentiality criteria. HIPAA adds ePHI-specific items: business associate agreements, ePHI access audit logs and breach notification.
How SECORA collapses the overlap into one workstream
Select the frameworks at onboarding and SECORA seeds the controls, objectives, scoring model, policy set and roadmap. Shared controls are collapsed so evidence is collected once and satisfies every equivalent. Add a framework later and only the extra controls appear. Every framework is still scored the way its assessor scores it: SPRS points for CMMC, percentage of Annex A for ISO, criteria coverage for SOC 2.
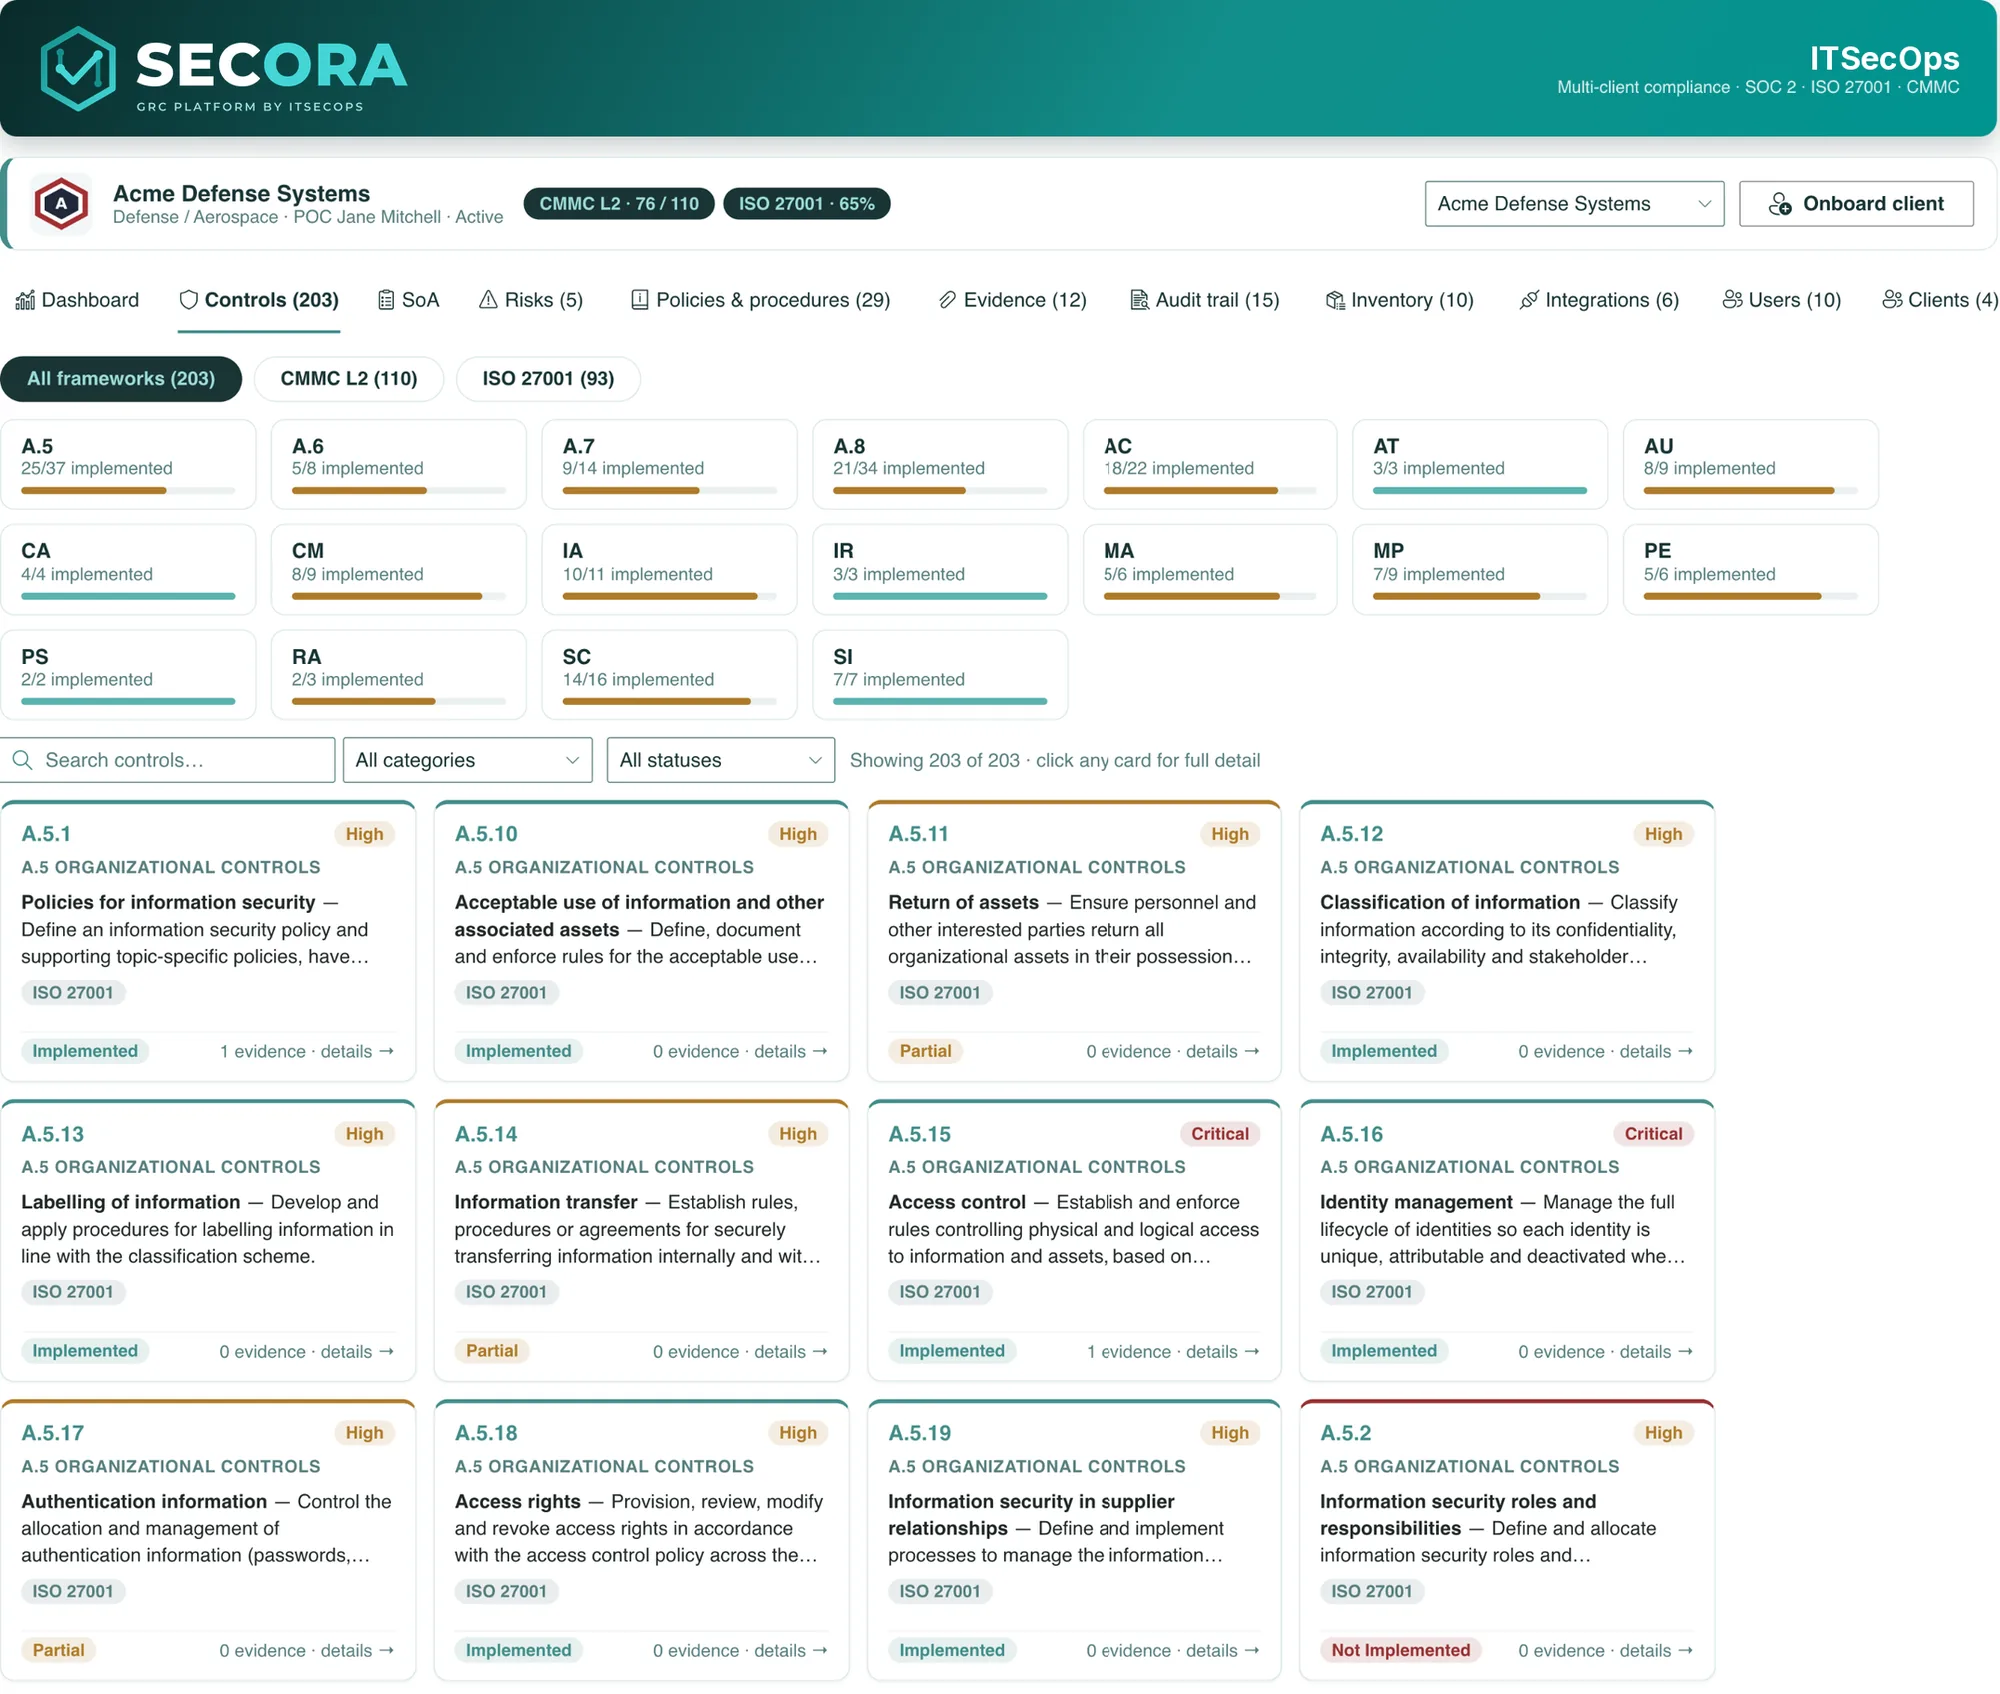
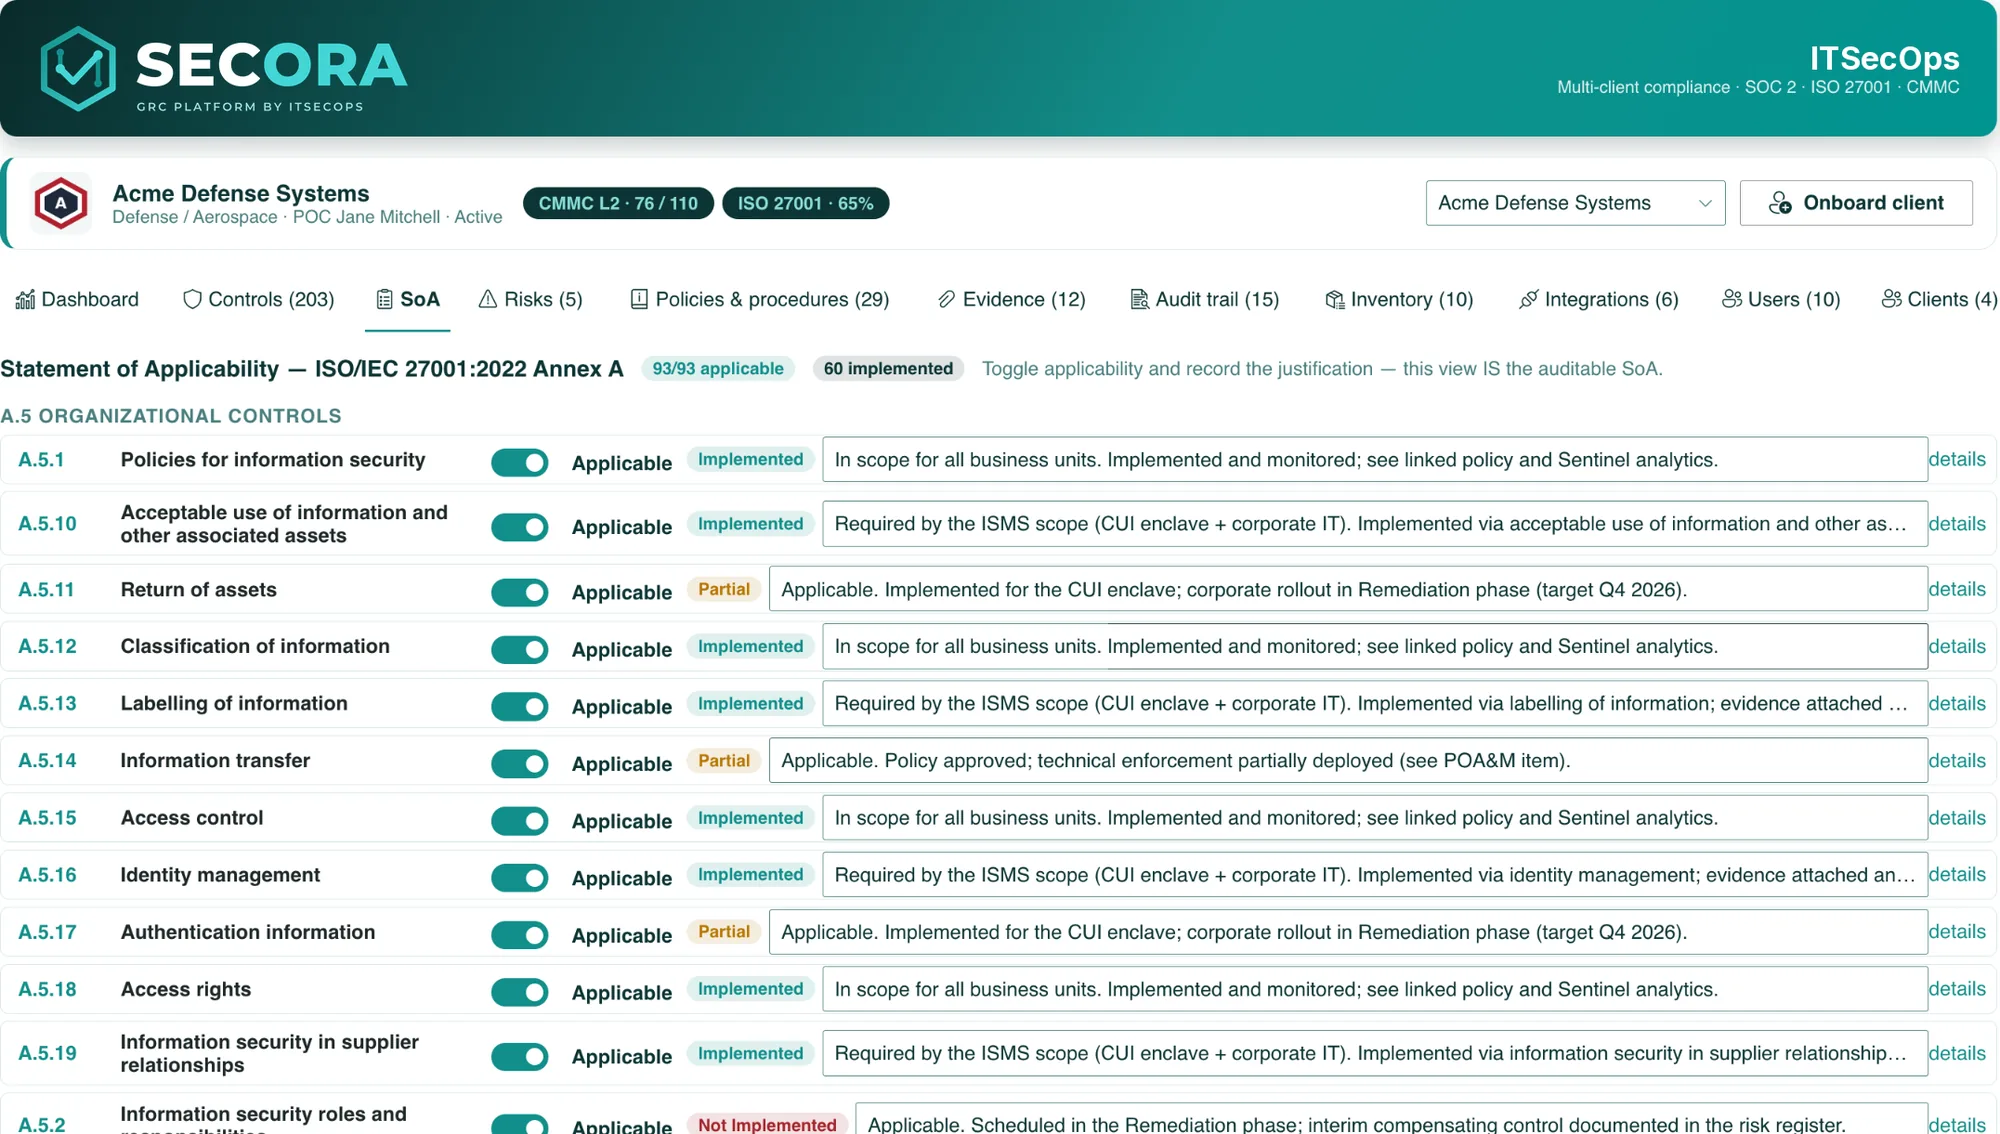
Framework pages: CMMC, ISO 27001, SOC 2, NIS2, HIPAA, GDPR, NIST CSF 2.0.
What SECORA costs
SECORA is licensed per organisation. You pay a one-time deployment fee that covers installation in your tenant, framework configuration, policy library seeding, dashboard customisation and hand-over, with twelve months of maintenance, updates and support by ITSECOPS included. There are no per-user, per-month or per-framework charges, and an optional maintenance renewal is available from year two. Because there is nothing to export at exit (the lists are already yours), there is no lock-in either. Model your own numbers in the three-year GRC cost calculator or request a written quote.
Frequently asked
Very heavily. SOC 2’s Common Criteria map almost one to one to ISO 27001 Annex A organisational and technological controls. In SECORA the shared documents cover both; SOC 2 adds the observation window and availability, confidentiality and processing-integrity criteria.
Not fully. CMMC’s 110 practices cover the access, identification, audit, configuration, incident and system protection families that overlap Annex A 5 to 8, but ISO adds the SoA, management review, internal audit and supplier controls. In the SECORA demo workspace a CMMC L2 plus ISO client needs 29 documents, 24 shared.
An ISO 27001 ISMS covers the Article 21 measure areas but NIS2 adds legal duties: 24 hour early warning, 72 hour notification, management accountability and registration with the national authority. SECORA tracks those as controls and risks alongside the shared library.
They are modelled on the SECORA demo workspace (Acme Defense Systems). Your control count is exact per framework; the document overlap depends on your scope and is confirmed during discovery.
See SECORA running in your own tenant
Walkthrough slots, deployment scope and a written quote within 1 business day.