
MDR vs XDR in one sentence: XDR (extended detection and response) is a technology that correlates security signals from endpoints, identity, email, cloud and network in one platform, and MDR (managed detection and response) is a service in which a 24×7 team investigates and responds to those signals for you. XDR costs $5 to $15 per device per month and still needs your people to watch it. MDR costs $6 to $22 per device per month with the people included. They are not alternatives: most MDR services in 2026 run on XDR telemetry, so the real question is whether you operate the platform yourself or pay a team to do it.
Updated October 6, 2026. Why this matters now: the Sophos Active Adversary Report 2026 traced 67 percent of incidents to identity-related root causes such as stolen credentials, and found 88 percent of ransomware encryption launched outside business hours. The first number is the argument for XDR, because endpoint-only tools do not see a stolen login. The second is the argument for MDR, because a platform nobody is watching at night stops nothing.
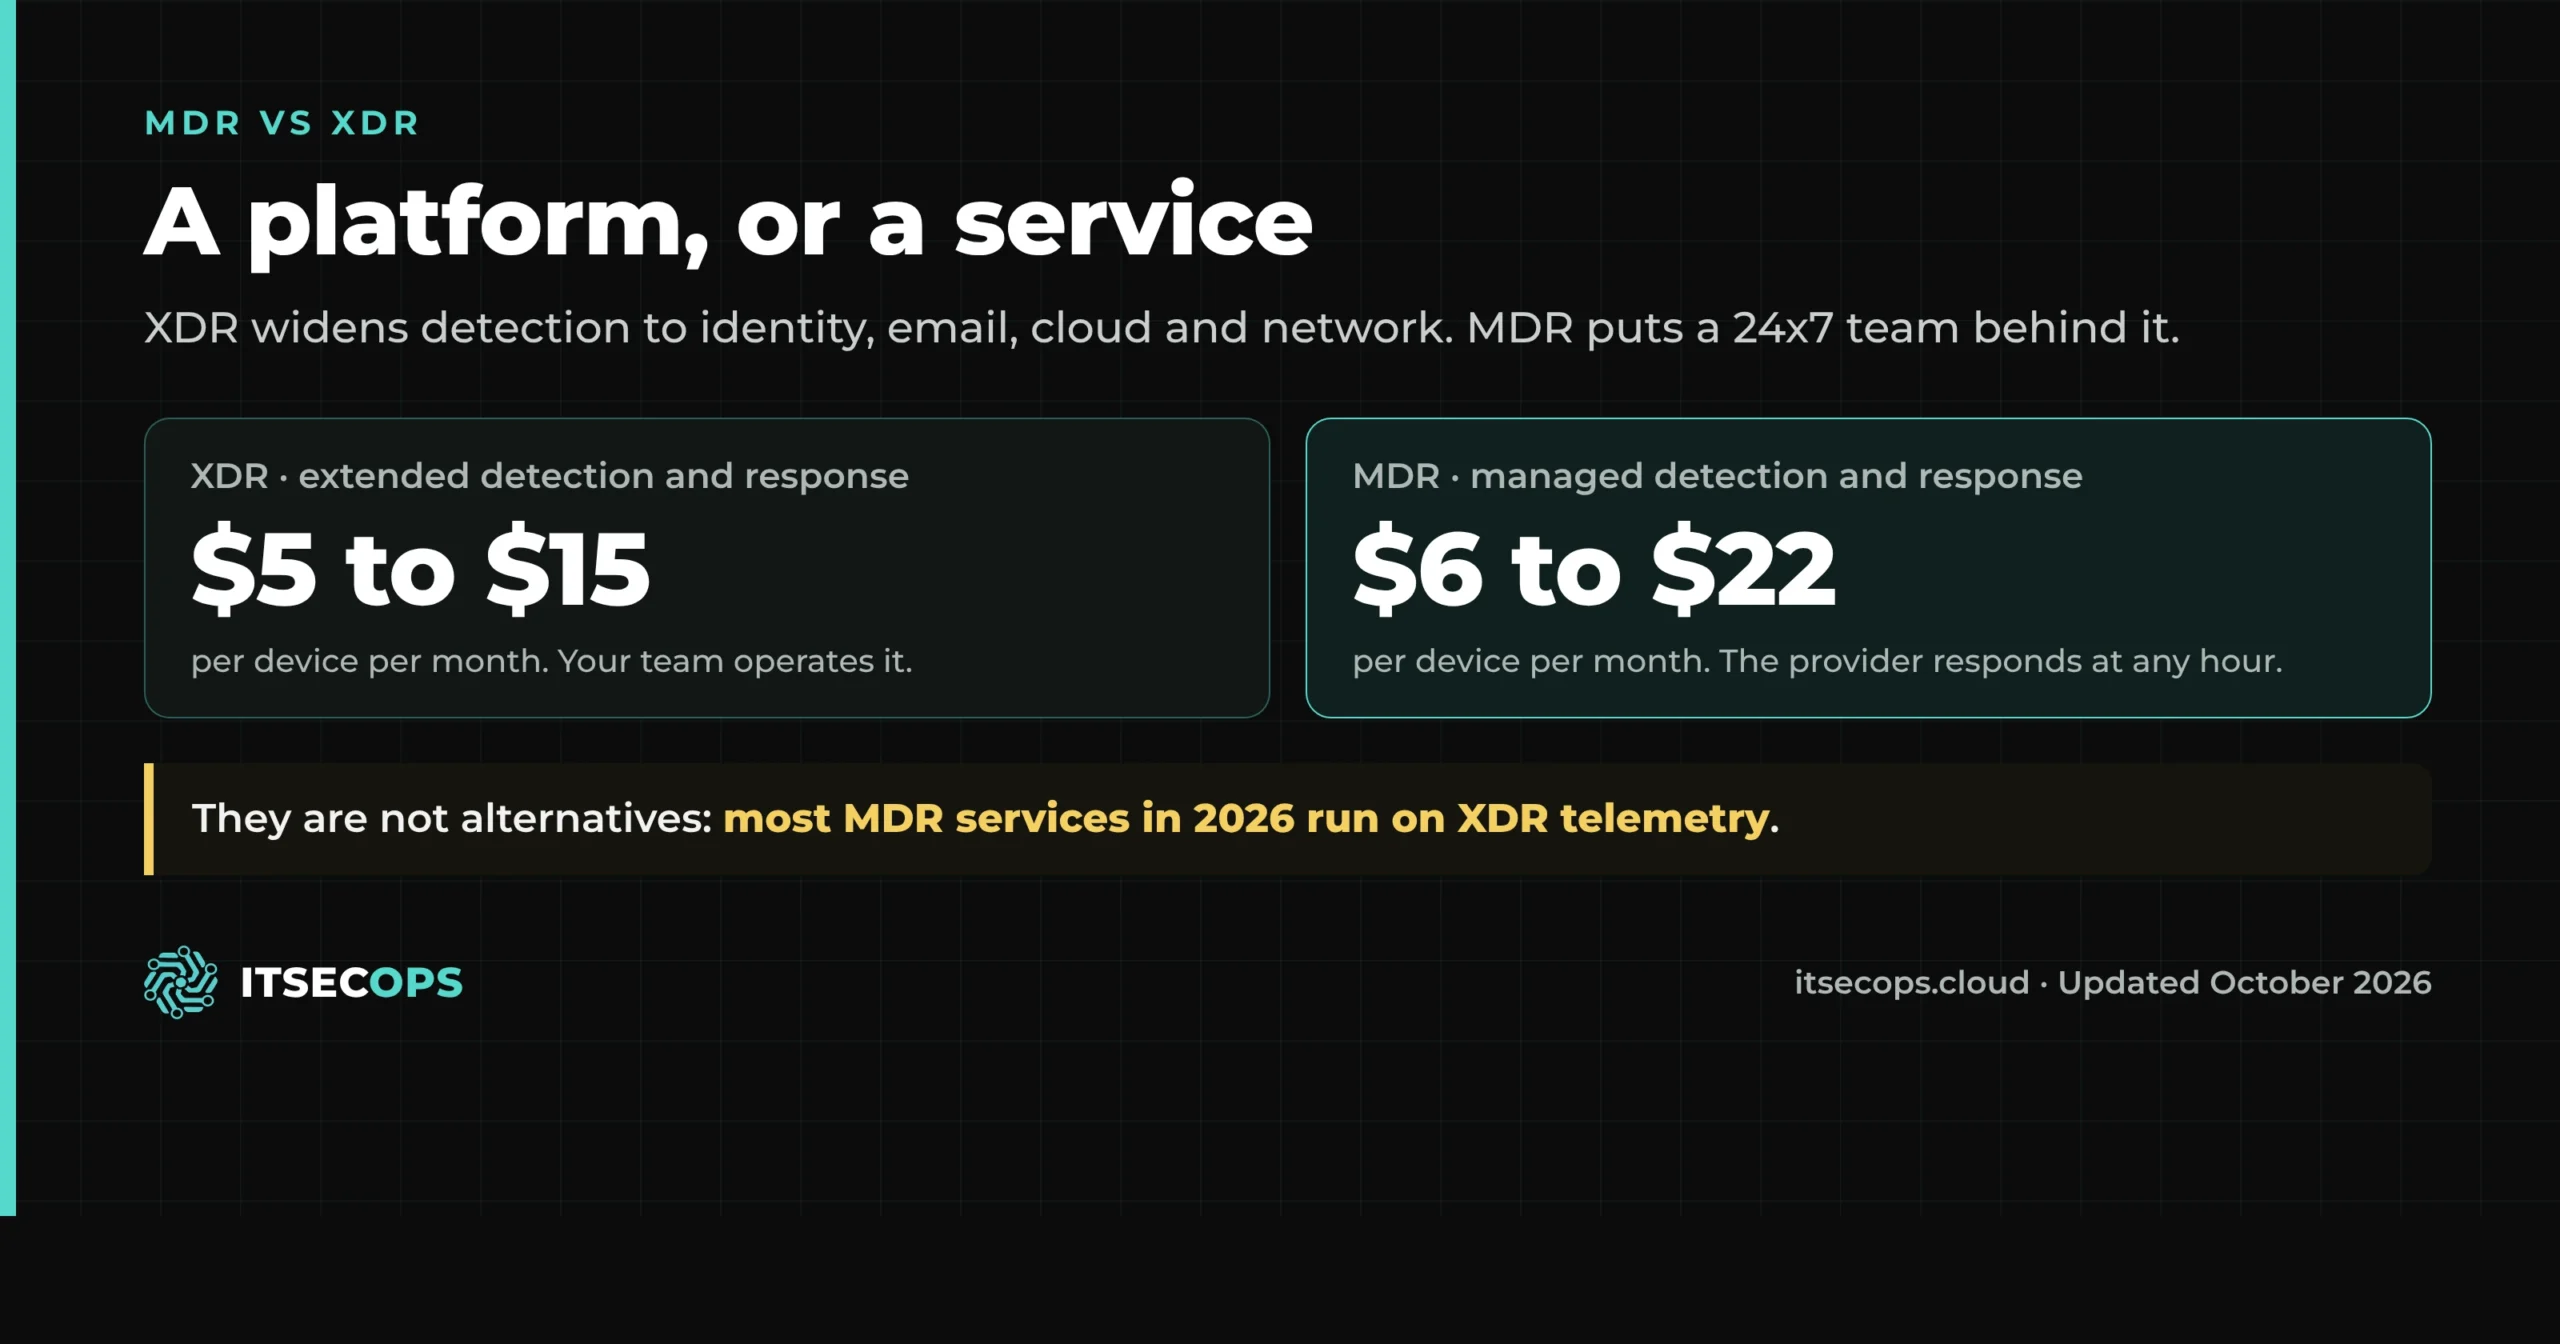
XDR vs MDR at a glance
| XDR | MDR | |
|---|---|---|
| What it is | A platform: EDR plus identity, email, cloud and network telemetry correlated in one console | A service: a 24×7 security team operating EDR or XDR on your behalf |
| What you are buying | Visibility and automation | Outcomes: investigation, containment and a report |
| Who responds | Your team, or playbooks your team builds | The provider, within minutes, at any hour |
| Staff you need | Security analysts with time to tune detections and watch the console | A contact for escalations |
| List price per device per month | $5 to $15 | $6 to $22 (ITSecOps: $8 to $16) |
| Best for | Companies with their own security operations team | Companies without one, which is most companies under 1,500 employees |
MDR or XDR: how to choose
- You have analysts on shift 24×7: buy XDR and run it yourself.
- You have a security or IT team during the day only: buy XDR with MDR on top, or keep your current tools and add after-hours SOC cover.
- You have no security staff: buy MDR and confirm in writing that identity and email are monitored as well as endpoints.
- You are under NIS2, CMMC, HIPAA or an insurance questionnaire: MDR, because each of them expects detection and response at any hour, with evidence.
What XDR and MDR cost at your size
| Devices | XDR licences per month | MDR per month | ITSecOps MDR per month |
|---|---|---|---|
| 50 | $250 to $750 | $300 to $1,100 | $400 to $800 |
| 100 | $500 to $1,500 | $600 to $2,200 | $800 to $1,600 |
| 250 | $1,250 to $3,750 | $1,500 to $5,500 | $2,000 to $4,000 |
| 500 | $2,500 to $7,500 | $3,000 to $11,000 | $4,000 to $8,000 |
XDR looks cheaper until you add the analysts. One seat covered around the clock takes at least five people. Full pricing by provider is on the MDR pricing page and in the cybersecurity price comparison.
GET XDR AND MDR QUOTED SIDE BY SIDE
Five questions to ask an MDR or XDR vendor
- Which log sources are monitored, and on which can you take action without calling us?
- What were your average time to acknowledge and time to contain last quarter?
- Is incident response included, or billed by the hour once an incident starts?
- Who owns the platform and the data if we leave?
- Is the price per device, per user or per gigabyte, and what makes it go up?
Where EDR and SOC fit
EDR is the endpoint-only starting point; see MDR vs EDR and the full MDR vs EDR vs XDR guide. A managed SOC is the widest option, covering every log source with one team; see managed SOC pricing by company size.
Compare and price it: MDR vs EDR · EDR vs MDR vs XDR · MDR pricing and cost per device
Frequently asked questions
What is the difference between MDR and XDR?
XDR is a technology: one platform that correlates signals from endpoints, identity, email, cloud and network. MDR is a service: a 24×7 team that investigates and responds using a platform like that. XDR answers what you can see. MDR answers who acts on it.
MDR or XDR: which should I buy?
If you have a security team that can watch a console around the clock, buy XDR. If you do not, buy MDR, and check that it runs on XDR telemetry so identity and email are covered as well as endpoints.
Is an XDR bundle overkill for a 50-person company?
As a tool you operate yourself, usually yes, because nobody has the hours to tune and watch it. As the telemetry underneath an MDR service it is not overkill at all: most attacks on small companies now start with a stolen identity or a phishing email, which endpoint-only tools see late.
Does MDR include XDR?
In 2026 most MDR services ingest identity and email signals as well as endpoint data, which is XDR in practice. Ask the provider to list the log sources that are monitored and the ones they can take action on.
How much do XDR and MDR cost?
XDR licences run $5 to $15 per device per month at list price. MDR runs $6 to $22 per device per month including the 24×7 team. ITSecOps MDR is $8 to $16 per device per month on Sophos, Microsoft Defender, SentinelOne or CrowdStrike.
Can I have both?
Yes, and that is the common outcome: an XDR platform you own, with an MDR team operating it. If you leave the provider you keep the platform and its data.
GET A WRITTEN MDR OR XDR RECOMMENDATION
Written reply within 1 business day · No phone call unless you ask · Partner pricing on Sophos, Microsoft, SentinelOne and CrowdStrike