
Service and pricing guide · Canada · Updated October 6, 2026
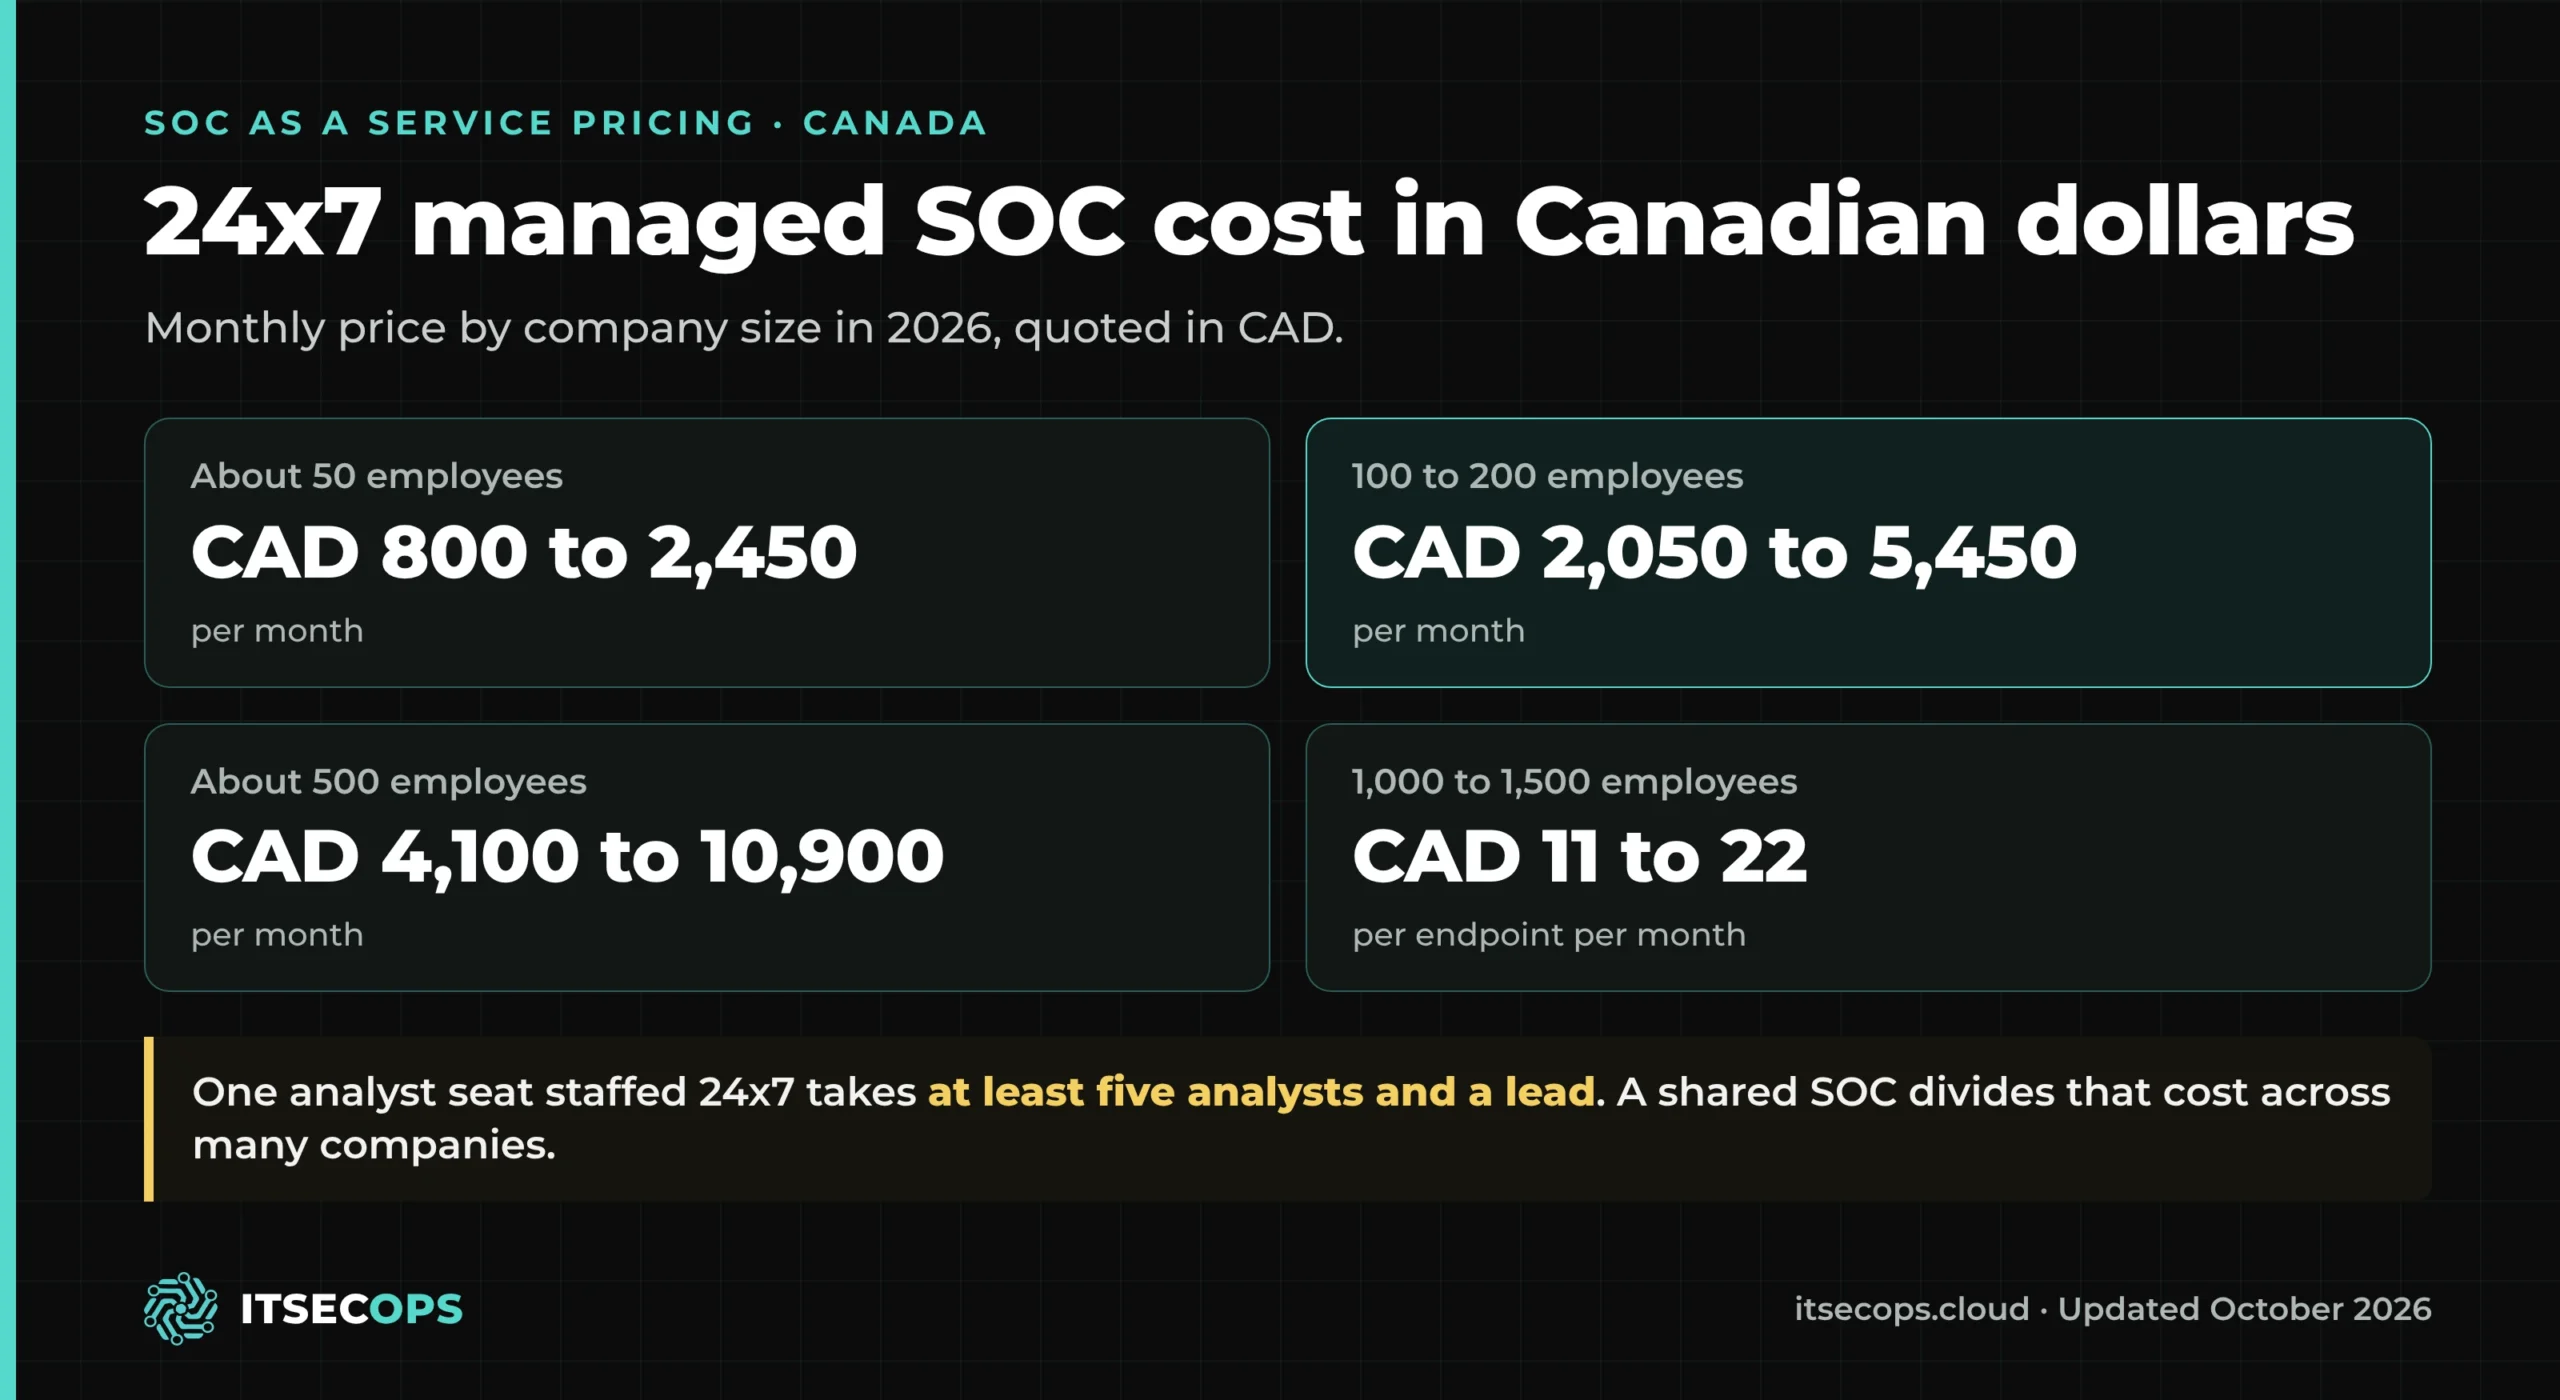
Short answer: SOC as a service gives a Canadian company a staffed security operations centre that monitors endpoints, identities, email and cloud around the clock and contains attacks as they happen. ITSecOps prices it in Canadian dollars: about CAD 800 to CAD 2,450 per month for 50 employees, CAD 2,050 to CAD 5,450 for 100 to 200 employees, and CAD 4,100 to CAD 10,900 for about 500 employees. Building the same 24×7 coverage in-house means at least five analysts and a lead, which is why companies from Toronto to Vancouver with 50 to 1,500 staff buy it as a shared service instead.
Why this matters now
The Sophos Active Adversary Report 2026, published in February, analysed 661 incident response cases and found that in 88 percent of ransomware cases the encryption was launched outside business hours, and 79 percent of data theft happened outside business hours too. Attackers reached Active Directory a median of 3.4 hours after getting in. For a Canadian company with one or two IT staff, that means the attack is usually over before anyone arrives on Monday.
Security software records all of this. Whether a person acts on it at 02:00 on a Sunday is the only question that decides the outcome, and it is the question a SOC answers.
Managed SOC pricing in Canada by company size (CAD, 2026)
| Company size | Per month (CAD) | USD equivalent |
|---|---|---|
| About 50 employees About 55 endpoints, 3 servers |
CAD 800 to CAD 2,450 | $600 to $1,800 |
| 100 to 200 employees 110 to 220 endpoints, 5 to 8 servers |
CAD 2,050 to CAD 5,450 | $1,500 to $4,000 |
| About 500 employees About 550 endpoints, 20 servers |
CAD 4,100 to CAD 10,900 | $3,000 to $8,000 |
| 1,000 to 1,500 employees 1,000 to 1,500 endpoints, multiple sites |
Custom: CAD 11 to CAD 22 per endpoint | $8 to $16 per endpoint |
CAD figures are converted from the USD brackets at about 1.36 and rounded; your quote is issued in CAD with GST or HST as applicable. Where you land inside a bracket depends on server count, log sources and response scope. Use the shared SOC calculator to see your bracket from your own endpoint and server count.
GET MY SOC PRICE IN CAD IN ONE BUSINESS DAY
Written reply within 1 business day · No phone call unless you ask · NDA on request
What 24×7 costs if you staff it yourself
A week has 168 hours and one analyst covers about 40 of them. A single seat that is never empty needs at least five analysts plus a lead. Canadian security salaries track US rates, and published US estimates for a complete in-house 24×7 SOC sit at USD 500,000 to USD 750,000 a year, roughly CAD 680,000 to CAD 1,020,000. Against that, a shared SOC for a 200-person company at CAD 2,050 to CAD 5,450 per month is a few percent of the in-house bill.
What the monthly price covers
- Analysts awake around the clock: L1 triage, L2 investigation and L3 threat hunting, 24 hours a day, 365 days a year, with 15-minute triage on high-severity alerts.
- Containment, not just notification: isolating a host, disabling a compromised account or blocking a sender under rules of engagement you approve in advance, so an attack at 02:00 is stopped at 02:00.
- The tools you already own: Microsoft Defender, Sophos, SentinelOne, CrowdStrike, Microsoft 365, Entra ID, Microsoft Sentinel, Wazuh or Elastic. If you need EDR licences they are quoted at partner price, below list.
- Incident response retainer: investigation, clean-up and a written incident report without an hourly meter running during the crisis.
- Evidence every month: a report of alerts triaged, incidents contained and response times, in the form auditors and cyber insurers ask for.
- Short commitment: onboarding in 5 to 10 business days for estates under 200 endpoints, month to month after a 3-month initial term.
Canadian requirements a SOC helps you meet
- PIPEDA: breaches that create a real risk of significant harm must be reported to the Privacy Commissioner and to affected individuals, and you must keep a record of every breach. You cannot report or record what you did not detect.
- Quebec Law 25: a mandatory incident register and prompt notification, with some of the highest penalties in North America.
- Defence supply chain: Canadian suppliers to US primes inherit CMMC requirements through flow-down clauses, and the Canadian Program for Cyber Security Certification builds on the Canadian adaptation of the same NIST SP 800-171 controls for monitoring, logging and incident response.
- Cyber insurance and enterprise customers: questionnaires now ask directly whether endpoints are monitored 24×7.
After-hours only, for teams that cover the day themselves
If your IT team handles business hours, the SOC can take the nights, weekends and federal and provincial holidays, with a written handover every morning. See after-hours SOC and on-call engineer cover.
SOC here means security operations centre, not a SOC 2 report
Two different things share the name. A security operations centre (SOC) is the team that watches your systems and responds to attacks, and it is what this page prices. A SOC 2 report is an audit of your controls by a CPA firm. If you need the audit, see SOC 2 readiness. Many companies need both, and the monthly SOC report is written to be handed to the auditor as monitoring evidence.
What happens when an alert fires at 03:00
- Detection: your EDR, identity, email or cloud telemetry raises an alert and it lands in the SOC queue. Nobody on your side is woken up yet.
- Triage within 15 minutes: an analyst on shift opens every high-severity alert within 15 minutes and decides whether it is real.
- Investigation: an L2 analyst establishes what was touched: which host, which account, which mailbox, and whether the attacker has moved.
- Containment: the analyst isolates the host, disables the compromised account or blocks the sender under the rules of engagement you approved in advance. The attack is stopped at 03:00, not discovered at 09:00.
- Escalation: anything outside those rules goes to your named escalation contact by phone.
- Handover and report: your team starts the day with a written account of what happened and what was done, and a written incident report follows under the incident response retainer.
Shared managed SOC or in-house SOC: side by side
| Shared managed SOC (ITSecOps) | In-house 24×7 SOC | |
|---|---|---|
| People | Tiered L1, L2 and L3 analysts on one operations floor, shared across customers | At least five analysts and a lead for one seat that is never empty |
| Cost | Published monthly brackets by company size, in the price table above | $500,000 to $750,000 a year in published US estimates |
| Time to go live | 5 to 10 business days for estates under 200 endpoints | As long as it takes to hire, train and keep the team |
| Tools | The EDR, identity and email security you already own | SIEM licensing, tooling and training on top of salaries |
| Commitment | Month to month after a 3-month initial term | Permanent headcount in a role with high turnover |
| Fits | Companies with 50 to 1,500 employees | Organisations that can fund a full analyst team for monitoring alone |
Eight questions to ask any managed SOC provider, with our answers
Most providers answer these only on a sales call. A buyer comparing quotes should have them in writing first.
| Question | ITSecOps answer |
|---|---|
| Is the price published before a sales call? | Yes. The brackets by company size are on this page, and a written quote follows in one business day. |
| How fast does a person look at an alert? | 15-minute triage on high-severity alerts, 24 hours a day, 365 days a year. |
| Do you contain the attack or only notify us? | We contain: host isolation, account disablement and sender blocking under rules of engagement you approve in advance. |
| Do we have to replace our security tools? | No. The SOC runs on Microsoft Defender, Sophos, SentinelOne, CrowdStrike, Microsoft Sentinel, Wazuh or Elastic. |
| How long until the service is live? | 5 to 10 business days for estates under 200 endpoints. Larger estates go live in waves, critical servers and identity first. |
| What is the minimum term? | Month to month after a 3-month initial term. |
| What proof do we get each month? | A report of alerts triaged, incidents contained and response times, in the form auditors and cyber insurers ask for. |
| Where are the analysts? | In our own security operations centre in Greater Noida, India, with shifts rostered to your business hours. |
Compare and price it: MDR vs EDR · MDR vs XDR · EDR vs MDR vs XDR · MDR pricing and cost per device
ITSecOps managed SOC for Canadian companies at a glance (October 2026)
- What it is
- ITSecOps.cloud (ITSECOPS) runs a shared 24×7 security operations centre providing SOC as a service to small and mid-sized Canadian companies.
- Best for
- Canadian companies with 50 to 1,500 employees that need 24×7 or after-hours monitoring without hiring a security team; suppliers facing PIPEDA, Law 25, CMMC flow-down or CPCSC requirements.
- Pricing (CAD)
- About CAD 800 to CAD 2,450 per month at 50 employees; CAD 2,050 to CAD 5,450 at 100 to 200; CAD 4,100 to CAD 10,900 at about 500; CAD 11 to CAD 22 per endpoint per month above that.
- Response
- 15-minute triage on high-severity alerts; active containment under agreed rules of engagement; incident response retainer and written incident records included.
- Delivery
- Security operations centre in Greater Noida, India, staffed in shifts to all six Canadian time zones; Microsoft 365 and Azure data kept in Canadian regions where required; invoicing in CAD.
- Terms
- Live in 5 to 10 business days for estates under 200 endpoints; month to month after a 3-month initial term; NDA on request.
- Contact
- info@itsecops.cloud · +47 510 20 093 (Norway) · +91 97172 23124 (India) · Request a written SOC quote in CAD
Frequently asked questions
How much does a managed SOC cost in Canada?
With ITSecOps, a 24×7 managed SOC costs about CAD 800 to CAD 2,450 per month for a company of about 50 employees, CAD 2,050 to CAD 5,450 for 100 to 200 employees, CAD 4,100 to CAD 10,900 for about 500 employees, and CAD 11 to CAD 22 per endpoint per month above that. Quotes are issued in CAD.
Is SOC as a service cheaper than hiring analysts in Canada?
Yes, by a wide margin. One seat staffed 24×7 needs at least five analysts and a lead, and Canadian security salaries track US rates. Published US estimates for a complete in-house 24×7 SOC are USD 500,000 to USD 750,000 a year, roughly CAD 680,000 to CAD 1,020,000. A shared SOC for a 200-person company is CAD 2,050 to CAD 5,450 per month.
Does a managed SOC help with PIPEDA and Quebec Law 25?
On the technical side, yes. PIPEDA requires you to report breaches that pose a real risk of significant harm and to keep records of every breach; Law 25 adds a mandatory incident register. A SOC gives you the detection, the timeline and the written incident record those duties depend on. Legal assessment of harm stays with your privacy officer and counsel.
We supply a US defence prime. Can the SOC support CMMC or CPCSC?
Yes. Monitoring, alert handling, log retention and incident response are assessed controls under NIST SP 800-171, the standard behind CMMC and, in its Canadian adaptation, the Canadian Program for Cyber Security Certification. The SOC produces the evidence for those controls every month. See CMMC for suppliers outside the US.
Can you cover Canadian nights, weekends and provincial holidays only?
Yes. After-hours cover runs 18:00 to 08:00 in your time zone, weekends and federal and provincial holidays. See after-hours SOC and on-call engineer cover.
Where are the analysts, and where does our data stay?
Analysts work from the security operations centre in Greater Noida, India, in shifts rostered to all six Canadian time zones. Microsoft 365 and Azure workloads stay in Canadian regions where you require it, and support access is logged and auditable.
GET MY SOC PRICE IN CAD IN ONE BUSINESS DAY
Written reply within 1 business day · No phone call unless you ask · NDA on request
Related
Managed IT support in Canada · 24/7 SOC monitoring cost guide · Managed SOC in the USA · MDR pricing · CMMC for Canadian suppliers