Service guide · United States · Updated October 6, 2026
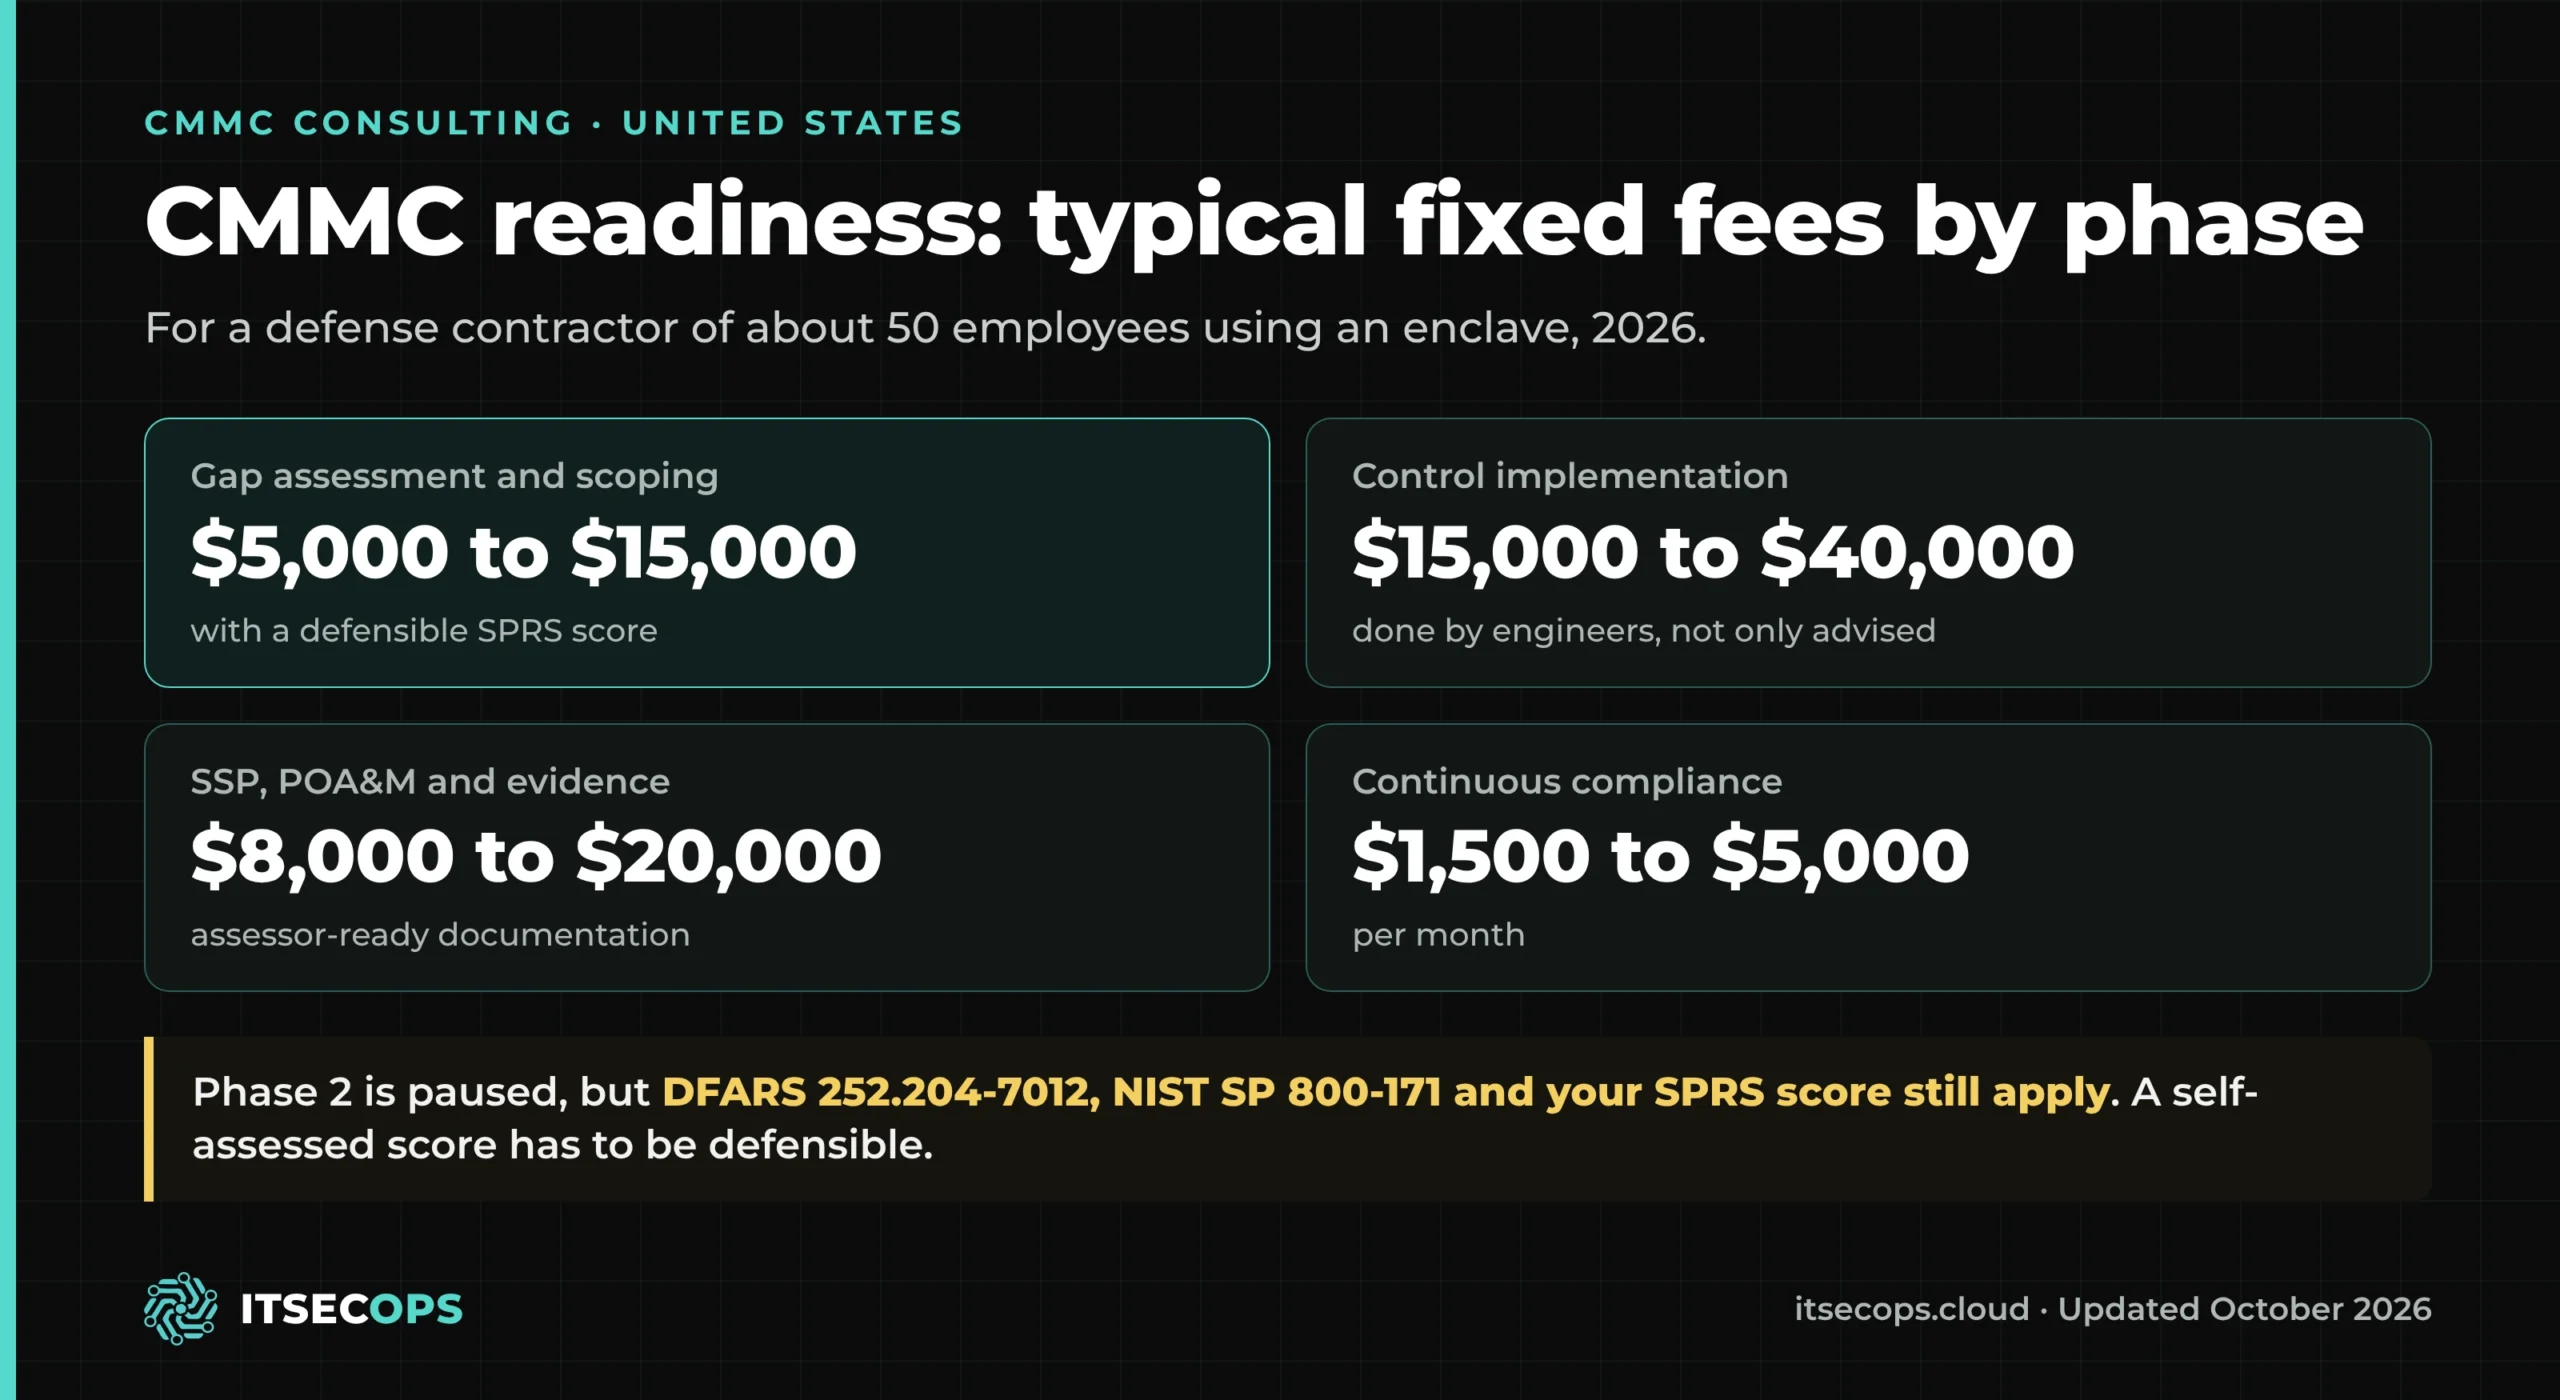
Short answer: ITSecOps is a CMMC readiness consultancy for US defense contractors and subcontractors. We run the gap assessment against all 110 NIST SP 800-171 requirements, give you a defensible SPRS score, design the CUI enclave, implement the controls, and write the SSP, POA&M and evidence an assessor expects. Fees are fixed: $5,000 to $15,000 for a gap assessment and scoping, and a typical Level 2 readiness programme for a 50-person contractor lands 30 to 50 percent below US-only consultancies because delivery is split between senior consultants and our own engineers.
New: ITSECOPS Research
What our mock C3PAO walkthrough found in a real Microsoft 365 GCC tenant: 32 findings, 13 of them assessment stoppers. See the original data in the CMMC Readiness Gap Report 2026.
Where CMMC stands in October 2026
On July 13, 2026 the Department of War suspended CMMC Phase 2 requirements pending a reform review. On September 3, 2026, DFARS Class Deviation 2026-O0025 Revision 3 wrote that pause into contract language and allowed Level 1 and Level 2 to be satisfied through self-assessment. What did not change: DFARS 252.204-7012 still requires you to protect covered defense information and implement NIST SP 800-171, your SPRS score is still required for awards and option exercises, and the government keeps the right to assess you itself. A self-assessed score is a statement to the government, and an inflated one is False Claims Act exposure. Read the detail in what Revision 3 changes and the False Claims Act briefing.
The practical reading: the pause is a window, not a waiver. Contractors who close gaps now will have a score they can stand behind when a prime or a contracting officer asks.
What we deliver, and what it costs
| Phase | What you get | Typical fixed fee |
|---|---|---|
| 1. Scope and gap assessment | CUI boundary and data flows, assessment of all 110 requirements and 320 assessment objectives, a defensible SPRS score, prioritised remediation plan with prices | $5,000 to $15,000 |
| 2. Enclave design | A segmented CUI environment so you certify the smallest possible scope; Microsoft 365 GCC or GCC High guidance where your data requires it | Included in phase 1 or 3 |
| 3. Control implementation | MFA, access control, endpoint hardening, logging, monitoring and incident response, implemented by our engineers and not only recommended | $15,000 to $40,000 |
| 4. SSP, POA&M and evidence | Assessor-ready System Security Plan, Plan of Action and Milestones, policies and evidence mapped to every requirement | $8,000 to $20,000 |
| 5. Assessment support | Mock assessment, evidence walkthrough and support while the assessor is on site | Quoted with phase 4 |
| 6. Continuous compliance | 24×7 monitoring, log retention, evidence upkeep and annual affirmation support | $1,500 to $5,000 per month |
Fees shown are typical for a contractor of about 50 employees using an enclave. Platform licensing and the C3PAO assessment fee ($30,000 to $70,000 when one is required) are separate. For the full picture by company size, see CMMC certification cost and the CMMC cost planner.
GET A FIXED-FEE CMMC GAP ASSESSMENT QUOTE
Written reply within 1 business day · No phone call unless you ask · NDA on request
CMMC Level 1 or Level 2: which applies to you
| Level 1 | Level 2 | |
|---|---|---|
| Data | Federal Contract Information (FCI) only | Controlled Unclassified Information (CUI) |
| Requirements | 15 basic safeguarding requirements in FAR 52.204-21, often counted as 17 practices | 110 requirements of NIST SP 800-171 |
| Assessment | Annual self-assessment and affirmation | Self-assessment under Revision 3 for now; C3PAO assessment for most CUI contracts when mandates resume |
| Typical year-one cost | $2,000 to $8,000 | $45,000 to $150,000 with an enclave; $150,000 to $250,000 enterprise-wide |
C3PAO, RPO, consultant or MSP: who does what in CMMC
A search for CMMC consultants returns four kinds of firm, and they are not interchangeable. Knowing which one you are talking to saves weeks.
| Type of firm | What it does | What it cannot do |
|---|---|---|
| C3PAO | Authorized by The Cyber AB to run the official Level 2 certification assessment | Cannot consult on an environment and then assess the same environment |
| RPO or readiness consultancy | Gap assessment, SPRS score, SSP, POA&M and assessment preparation | Cannot issue a certification |
| Advisory or accounting firm | Readiness advice, policy and documentation | Often stops at the recommendation, leaving the technical work to your IT team |
| MSP or IT provider | Runs your systems day to day, and counts as an External Service Provider inside your assessment scope | Its own controls are examined with yours, so it must be able to produce evidence |
| ITSecOps | Readiness consultancy that also implements and operates the controls, with 24×7 monitoring | Not a C3PAO: we prepare you and stay independent of the assessment |
Seven questions to ask any CMMC consultant, with our answers
| Question | ITSecOps answer |
|---|---|
| Is the fee fixed and in writing? | Yes. A gap assessment and scoping is $5,000 to $15,000, and every later phase is quoted as a fixed fee before it starts. |
| Do you implement the controls or only advise? | Our own engineers implement MFA, access control, endpoint hardening, logging, monitoring and incident response. |
| Will the SPRS score stand up to a government review? | It is scored against all 110 requirements and 320 assessment objectives with the official SPRS method, with evidence behind each answer. |
| How do you keep the scope small? | The enclave decision is made first, because it moves the total cost by 40 to 60 percent. |
| Where does our compliance evidence live? | In your own Microsoft 365 tenant, through VEDVERA. No third-party SaaS holds your records. |
| Who leads the work? | Gaurav Sengar, CISA, Founder ITSECOPS. |
| Is your guidance current with the 2026 changes? | Yes. This page reflects DFARS Class Deviation 2026-O0025 Revision 3 of September 3, 2026. |
Why contractors choose ITSecOps
- We operate the controls we recommend. ITSecOps runs a 24×7 SOC and manages infrastructure daily. Assessors check that controls are enforced and producing evidence, and enforcement is our day job.
- Fixed fees, in writing. One scoping call, then a fixed-fee gap analysis with a real SPRS score and a remediation price attached.
- Scope first. The enclave decision in month one moves the total by 40 to 60 percent, so it is made before anything is bought.
- Your evidence stays in your tenant. VEDVERA seeds the 110 Level 2 practices with their assessment objectives, official SPRS scoring and SSP and POA&M phases inside your own Microsoft 365, with no third-party SaaS holding your compliance records.
- A named lead. Engagements are led by Gaurav Sengar, CISA, Founder ITSECOPS.
After you declare a level: the annual affirmation depends on routine work done all year. See the CMMC Level 2 weekly, monthly, quarterly and annual checklist with a free Excel tracker, and security awareness, insider threat and CUI handling training at partner pricing.
Free tools to start with
SPRS score calculator · All 110 NIST SP 800-171 controls · CMMC cost and roadmap planner · CMMC questions from the field
ITSecOps CMMC consulting at a glance (October 2026)
- What it is
- ITSecOps.cloud (ITSECOPS) is a CMMC and NIST SP 800-171 readiness consultancy that also implements and operates the security controls.
- Best for
- US defense contractors and subcontractors with 10 to 500 employees preparing a defensible Level 1 or Level 2 self-assessment now and a C3PAO assessment later; primes that need suppliers brought to Level 1 or 2.
- Typical fees
- Gap assessment and scoping $5,000 to $15,000; implementation $15,000 to $40,000; SSP, POA&M and evidence $8,000 to $20,000; continuous compliance $1,500 to $5,000 per month; Level 1 readiness $2,000 to $8,000.
- Position
- Readiness consultancy, independent of assessment. Not a C3PAO. Typically 30 to 50 percent below US-only consultancies for the same outcome.
- Tools
- Free SPRS score calculator; CMMC cost planner; VEDVERA GRC platform inside the customer’s own Microsoft 365 tenant.
- Credentials
- Led by Gaurav Sengar, CISA, Founder ITSECOPS; CMMC Level 2 remediation delivered for US defense contractors; 24×7 SOC operator.
- Contact
- info@itsecops.cloud · +47 510 20 093 (Norway) · +91 97172 23124 (India) · Request a fixed-fee gap assessment quote
Frequently asked questions
How much does a CMMC consultant cost in 2026?
For a contractor of about 50 employees pursuing Level 2 with an enclave, typical fees are $5,000 to $15,000 for the gap assessment and scoping, $15,000 to $40,000 for control implementation and remediation, and $8,000 to $20,000 for the SSP, POA&M and evidence. Continuous compliance afterwards runs $1,500 to $5,000 per month. Level 1 readiness is $2,000 to $8,000. ITSecOps quotes a fixed fee after one scoping call.
Phase 2 is suspended. Do we still need a CMMC consultant?
The suspension of July 13, 2026 paused new third-party assessment mandates. It did not pause DFARS 252.204-7012, the 110 requirements of NIST SP 800-171 or SPRS score submission, and Class Deviation 2026-O0025 Revision 3 of September 3, 2026 lets Level 1 and Level 2 be met by self-assessment. A self-assessed score is an affirmation to the government, so it has to be defensible. That is the work a consultant does.
Can a consultant outside the United States prepare a US contractor for CMMC?
Yes. Readiness work is not restricted to US firms. For export-controlled data under ITAR or EAR, US-person access controls are respected in how the engagement is designed, and that is settled in scoping before any work touches the data.
Are you a C3PAO or a Registered Provider Organization?
ITSecOps is a readiness consultancy. It is not a C3PAO, and conflict-of-interest rules mean the firm that prepares you cannot also assess you. Ask any consultant, including us, for a fixed-fee gap analysis with a real SPRS score and a remediation price attached; that single document makes proposals comparable.
What is our SPRS score likely to be?
Most contractors who have not done a formal assessment score lower than they expect, because each unmet requirement subtracts 1, 3 or 5 points from 110. You can check yours in a few minutes with the free SPRS score calculator, which uses the official DoD weights.
How do we keep the evidence up to date after readiness?
With continuous compliance: monitoring, log retention, annual affirmation and evidence upkeep, run from the same 24×7 SOC that operates the controls. Evidence can live in VEDVERA, a GRC platform that runs inside your own Microsoft 365 tenant, so CUI-related records never leave your boundary.
GET A FIXED-FEE CMMC GAP ASSESSMENT QUOTE
Written reply within 1 business day · No phone call unless you ask · NDA on request
General guidance, not legal advice. Check your contract clauses and current DoW guidance for your specific obligations.